






Karsten Wenzlaff, Advisor
August 26th, 2025
Karsten Wenzlaff is a Crowdfunding and Fintech Expert from Germany. He is Secretary-General of Digit[...]


August 28, 2026 | NCFA Insight | Open Banking Open Finance And Data Sharing, Digital Identity And Trust, Risk Compliance And Regtech, Cybersecurity And Fraud
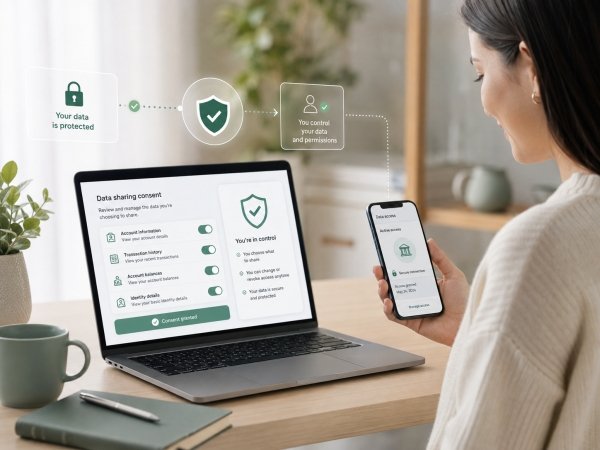
On August 26, 2026, Canada’s Office of the Privacy Commissioner (OPC) called for five changes to Canada’s proposed Consumer-Driven Banking Regulations including what financial data can be shared, what firms must prove before accreditation, when public data can be reused without consent, how security keeps pace with new threats, and how the Bank of Canada and Privacy Commissioner coordinate oversight.
The submission arrived on the last day of the government's 60-day consultation, which closed August 26. Finance Canada now has to decide which recommendations make it into the final regulations before Canada's open banking system starts moving from rulemaking into accreditation and implementation.
The Commissioner supports consumer-directed data sharing, multi-factor authentication and mandatory breach reporting to the Bank of Canada. The five requested changes go further and could affect compliance costs, product design, consumer trust and which fintechs can afford to participate.
The proposed regulations cover identity information, account identifiers, fees and terms, balances, transactions and information about financial products. The OPC says those categories aren't detailed enough for consumers to know exactly what information they are agreeing to share and points to Australia’s Consumer Data Right as a more precise model.
It's important when someone is looking at a consent screen. "Identity data" doesn't tell a customer whether a provider will receive a name, address, email, phone number or other information.
The issue becomes more important as firms combine bank data with other sources and use it for credit, fraud, pricing or financial recommendations. Open banking decision intelligence becomes more valuable as firms infer more from permissioned financial data, which makes precision about what was actually shared even more important.
If Canada wants meaningful consent, people need to know what is leaving their bank before they approve it.
The proposed rules offer four accreditation routes under Bank of Canada oversight, including streamlined treatment for payment service providers already registered under the Retail Payment Activities Act. The OPC wants stronger proof from some applicants, including evidence that security controls are working, technical standards are being met and authentication and complaint processes are ready.
It also wants certain financial institutions to show that people responsible for consumer-driven banking have been assessed for good character and integrity, and that insurance or other guarantees are available to manage data-related risks.
That raises the accreditation bar for good reason. Accredited firms may receive account identifiers, balances, transaction histories and other highly sensitive information. The commercial question now is how much proof Canada requires and what it costs credible firms to provide it.
Finance Canada estimates the proposed regulations will generate C$13.2 billion in benefits over ten years while adding about C$457.7 million in regulatory costs. Under the government's central scenario, roughly 680 businesses participate initially, including 578 small businesses, with an estimated average annualized regulatory cost of C$89,133 for each small business.
Large financial institutions can spread fixed security, legal and reporting costs across millions of customers. Smaller fintechs can't. Canada needs to keep poorly prepared firms away from consumer financial data without making the cost of proving readiness another advantage for incumbents.
The OPC also wants Finance Canada to narrow an exception that allows some publicly available information to be used without consent. Its recommendation is that public data should not include information where a consumer still has a reasonable expectation of privacy.
Information can technically be public without someone expecting it to be collected, combined with financial records and reused inside a commercial service. Open banking makes those combinations easier and potentially more valuable.
The final rules therefore need to protect against a consent loophole where one piece of public information becomes a reason to use financial information in ways the customer didn't reasonably expect.
The proposed regulations already require vulnerability management, authentication, encryption, network protection, employee training and tested incident-response plans, with those controls applied in proportion to the sensitivity of the data. The OPC wants an additional obligation requiring firms to keep those safeguards appropriate as technology and cyber risks evolve.
That's certainly more demanding than completing a checklist once. After a breach, a firm could still have to show that its security was appropriate for the data it held and the risks it should reasonably have been managing.
For banks and fintechs, security readiness therefore becomes an ongoing operating requirement. Canada's proposed open banking requirements already span accreditation, authentication, security, technical standards, liability, complaints and Bank of Canada supervision. Companies preparing to participate need proof that those controls actually work, not just policies saying they exist.
The Bank of Canada will supervise consumer-driven banking participants while the Privacy Commissioner continues to oversee federal private-sector privacy obligations. A serious data breach can involve both, so the OPC wants explicit authority for the regulators to coordinate their work and share information where necessary.
Without that, companies can face overlapping requests and investigations while an important issue still falls between mandates. When customer data is exposed, management needs to know who must be notified, what each regulator expects and how the two authorities will divide the work.
Clear coordination is especially important because Canada is trying to replace a system millions of people already use. Finance Canada estimates roughly nine million Canadians currently rely on financial-data services using credential-based screen scraping. Regulated API access should reduce important security and liability risks, but only if supervision works cleanly when something goes wrong.
The OPC is asking Finance Canada to be more precise about what data moves, who can receive it and what firms must prove before they get access. Those protections however cost money. Independent security work, technical compliance, authentication, insurance, reporting and complaint processes all consume capital that a younger company could otherwise spend on product development, hiring or customer acquisition.
The answer isn't weaker safeguards. Financial transaction data is too sensitive for that. The challenge is to determine whether each requirement addresses a real risk and whether the cost is proportionate to the firm, activity and data involved.
Canada's C$13.2 billion benefit estimate assumes firms enter the market and build services people want to use. Open banking opportunities in Canada already span verification, cash-flow tools, SME services, financial management and future payment initiation, but APIs alone won't create competition.
Consumers need providers they trust, and credible challengers need a realistic way to qualify. The final rules will help decide both.
How high can Canada raise the privacy and security bar for open banking before the cost of clearing it starts protecting incumbents from the competition the system is supposed to create?
 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
The Privacy Commissioner wants clearer rules in five areas: exactly what financial data can be shared, what firms must prove before accreditation, when publicly available data can be used without consent, how security safeguards should keep pace with changing threats, and how the Bank of Canada and Privacy Commissioner coordinate oversight.
No. The 60-day consultation on the proposed Consumer-Driven Banking Regulations closed on August 26, 2026. Finance Canada now has to decide what changes to make before the regulations are finalized.
Yes. Stronger accreditation, security, insurance and compliance requirements can improve consumer trust and keep poorly prepared firms out, but they also raise the cost of participation. The challenge is setting a high enough bar to protect financial data without making open banking too expensive for credible smaller fintechs to enter.
 |  |  |
|---|---|---|
 |  |  |



August 26th, 2025

January 4th, 2024

June 1st, 2021

September 9th, 2020

July 9th, 2018

January 3rd, 2018

September 25th, 2017

June 20th, 2017

May 10th, 2017

December 14th, 2016

Leave a Reply