





Karsten Wenzlaff, Advisor
August 26th, 2025
Karsten Wenzlaff is a Crowdfunding and Fintech Expert from Germany. He is Secretary-General of Digit[...]


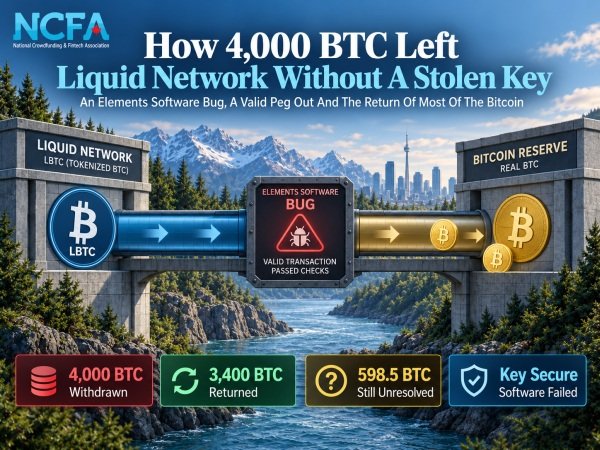
On September 6, 2026, the Liquid Network reported a 4,000 BTC withdrawal from the Bitcoin backing its sidechain. The bitcoin was worth about US$320 million when the incident was disclosed and represented roughly 95% of the approximately 4,200 BTC then reported in the federation wallet.
The size alone made it one of the year's most consequential digital asset security incidents. The mechanics made it stranger. SideSwap says the authorization key used in the peg out was not compromised. Instead, the 4,000 LBTC submitted for redemption was later attributed to a bug in Elements, the software underlying Liquid.
Most of the bitcoin has since come back. On September 7, the withdrawing party returned 3,400 BTC after an unusual onchain exchange with Blockstream over the software patch. Roughly 598.5 BTC, worth about US$47 million on September 8, remained at the withdrawal linked address when this Story was prepared.
Nearly an entire reported Bitcoin reserve left through an apparently valid redemption process even though the authorization key itself had not been stolen.
Protecting private keys is essential. Liquid's incident shows why the software deciding which assets are valid can matter just as much as the cryptography authorizing their redemption.
Liquid is a Bitcoin sidechain. Users lock bitcoin and receive LBTC that can circulate on Liquid before being redeemed back into bitcoin.
Before the incident, reporting put the federation wallet at roughly 4,200 BTC. About 4,000 BTC left during the withdrawal, putting almost the whole reported reserve behind one incident.
The response was immediate. Liquid activity was paused, bridge nodes were disabled and exchanges were asked to suspend LBTC deposits and withdrawals. SideSwap also stopped swaps, peg ins and peg outs.
That bought developers time to work out how such a large redemption had been accepted before normal bridge activity continued.
A stolen withdrawal key would have provided a familiar explanation. SideSwap says that didn't happen. The service processed a valid authorization, which pushed attention back toward the LBTC that entered the redemption process.
SideSwap says 4,000 LBTC was sent to its peg out service. The service burned the tokens against a valid authorization, after which the Liquid Federation released roughly 3,996 BTC to a Bitcoin address.
SideSwap says neither its systems nor its Peg out Authorization Key was compromised.
The crucial discovery came afterward. According to the account of the investigation, Blockstream determined that the LBTC involved had been created through a bug in Elements.
Elements is the open source software on which Liquid runs. The failure therefore appears to have happened before the final Bitcoin redemption rather than through theft of the SideSwap authorization key.
The peg out machinery can receive a valid authorization and release real bitcoin while the LBTC entering that process has already been corrupted by a software failure. Securing the key is necessary. It doesn't cover every route to an invalid redemption.
Then the incident took an unusual turn. The withdrawing party described itself as white hat and began communicating through messages recorded on Bitcoin.
Blockstream contacted the party through an onchain transaction. The party later told Blockstream to fix the bug and make sure the relevant nodes were patched before the bitcoin would be returned.
The white hat description remains the party's own characterization. It isn't an independently established status.
Blockstream later sent an authenticated message saying its bridge nodes had been patched. The response was followed by a transaction returning exactly 3,400 BTC to the federation address.
That recovered about 85% of the withdrawn bitcoin. The same transaction left approximately 598.5 BTC at the withdrawal linked address.
Neither Blockstream nor Liquid had publicly identified that remaining bitcoin as an agreed payment when this Story was prepared.
A party controlling hundreds of millions of dollars in bitcoin communicates with the infrastructure provider through the blockchain itself, waits for a software repair and then returns most of the funds. It's an extraordinary sequence, but it doesn't establish that the original withdrawal was authorized or benevolent.
Independent security researchers have begun explaining how the Elements failure may have happened.
CertiK's incident analysis points to Elements' handling of rangeproof verification caching. Its reconstruction says a flaw could allow different validation contexts to share a cached result and cause invalid value to be accepted.
That could explain how LBTC that shouldn't have been valid reached the peg out process.
The technical analysis is developing faster than the official explanation.
Blockstream hadn't published a complete technical postmortem when this Story was prepared. The exact affected software versions, complete code path, deployment history and remediation therefore aren't settled yet.
The confirmed finding is narrower and important enough on its own. Blockstream identified an Elements software bug as the source of the LBTC involved in the withdrawal, according to SideSwap's account.
When a token represents an underlying financial asset, software validation becomes part of the reserve control. If the system accepts an asset state it should reject, that mistake can become a claim on real assets even when the keys protecting them remain secure.
The size of the withdrawal makes that connection hard to miss. Roughly 95% of the reported bitcoin reserve was involved before most of the funds came back.
That doesn't mean Liquid permanently lost 95% of its backing. It means a software failure produced a redemption event large enough to put almost the entire reported reserve into question at once.
For digital asset firms, reserve security therefore extends well beyond storing keys.
Supply verification, transaction validation, reserve reconciliation, withdrawal monitoring, circuit controls and incident response all become part of the same operating problem.
That same issue appears in how crypto custody regulation is changing, as the market moves beyond simply holding private keys toward segregation, authority, resilience and accountability.
A secure key can't compensate for software that accepts an asset state it should reject. Issuance, validation, reserves and redemption all have to work together because a failure in one can reach the value protected by another.
Liquid's federation also gave operators a practical advantage during the response. Identifiable participants could coordinate, stop infrastructure, patch bridge nodes and prepare a restart.
That can make emergency intervention faster. It also means federation governance and operating procedures are part of the security model rather than something separate from it.
The same problem gets more important as financial institutions put securities, funds, deposits and other assets onto programmable infrastructure.
Tokenization becoming a business investors can measure captures the commercial side of that development. Liquid exposes the other requirement. Redemption and reserve systems still have to work when software doesn't.
Returning 3,400 BTC dramatically reduces the financial exposure, but it doesn't explain why nearly the whole reported reserve could leave through one sequence or what now prevents a recurrence. Those answers will determine whether this remains a contained software failure or becomes a longer trust problem for Liquid.
Liquid's authorization key reportedly held. Its validation software didn't. Nearly 4,000 BTC still left before most of it came back, showing why tokenized asset security depends on much more than protecting the keys that authorize redemption.
 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer to peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit www.ncfacanada.org
 |  |  |
|---|---|---|
 |  |  |



August 26th, 2025

January 4th, 2024

June 1st, 2021

September 9th, 2020

July 9th, 2018

January 3rd, 2018

September 25th, 2017

June 20th, 2017

May 10th, 2017

December 14th, 2016

Leave a Reply