Going public puts every control your fintech owns or outsources under a microscope. Auditors, regulators, and future shareholders want hard evidence that third-party weak spots cannot derail your debut.
Roughly 30% of breaches trace back to external suppliers, and each incident costs an average $4.44 million, according to IBM's 2024 Cost of a Data Breach Report. Advisers preparing S-1 filings increasingly want a repeatable way to assess outside cyber risk before the SEC asks, and investors read disciplined third-party oversight as a proxy for operational maturity.
Here is the catch: your SOC 2 program alone will not clear the public-company bar. SOC 2 demonstrates protection of customer data, while SOX 404 focuses on financial-reporting integrity. A purpose-built vendor-risk platform bridges that gap by connecting vendor security evidence to the controls auditors expect in an IPO cycle. We ranked five platforms on the criteria that matter most for IPO prep: compliance fit, automation depth, auditor acceptance, and cost-to-value.
How we ran the numbers
We started with fifteen tools from analyst waves, forums, and twenty competitor write-ups, then removed anything lacking a purpose-built vendor-risk module or fintech case study, leaving five contenders. We scored each on a 100-point scale across four questions:
IPO-compliance coverage (25 pts): Does it map evidence to SOC 2 and carry it forward into SOX 404 testing? Audit-ready exports earn full marks; static PDFs do not.
Automation & AI depth (25 pts): How much manual vendor-review work disappears? We looked for AI that flags risky answers and missing evidence, not chatbots that rephrase text.
Auditor & investor acceptance (20 pts): Big Four familiarity, repeat fintech IPOs, and recognizable trust signals reduce friction.
Cost-to-value ratio (15 pts): Subscription cost balanced against headcount savings and eleventh-hour consultants.
Two CISOs who took fintechs to market last year reviewed the weighting, confirming it reflects where auditors press hardest.
1. Vanta: your single pane of glass for vendor risk
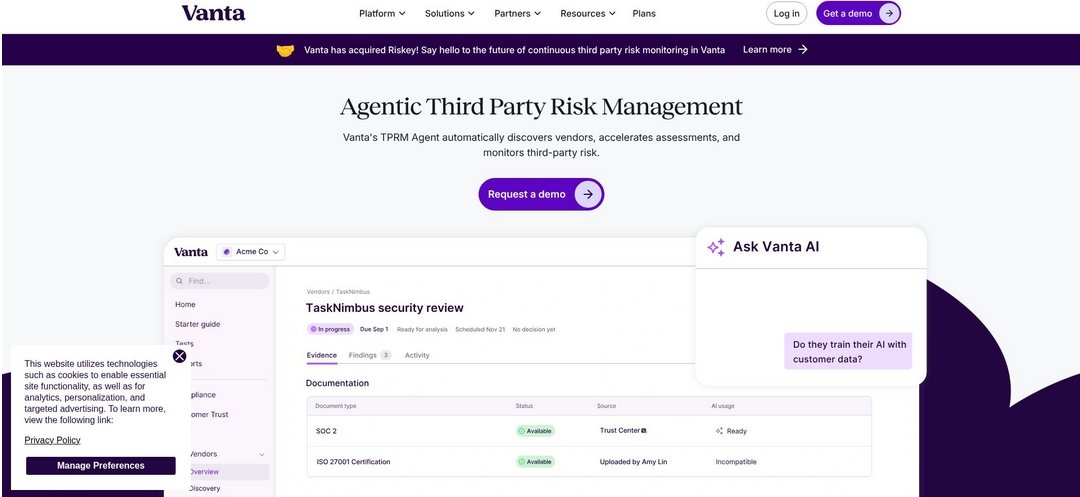
Vanta folds vendor oversight into the same dashboard you use for SOC 2, helping teams remediate risk up to 45% faster. VRM, compliance automation, Trust Center, and SOX ITGC live in one system with shared evidence and cross-framework mapping.
Ideal for: fintech security/compliance teams (~50 to 5,000 employees) running SOC 2 and standing up SOX ITGC readiness who want one platform over bespoke bank-style customization.
Vendor risk: three phases (discovery/onboarding, security reviews, continuous monitoring). Bulk CSV import, configurable intake (business criticality, integration access, data types). Shadow-SaaS discovery via Okta, Azure AD/Entra, and Google Workspace, extended through Jamf, Intune, and JumpCloud.
AI/automation: AI Questionnaire Review reads SOC 2 reports, ISO statements of applicability, PCI attestations, contracts, and trust-center materials, then drafts cited answers; gaps push to Jira and Slack.
Compliance depth: 35+ frameworks with cross-mapping. SOX ITGC out of the box with 33 controls and 15 core policies, an estimated 10 to 20 hours to complete, covering access management, change management, and IT operations (ITGC, not full financial process controls).
Monitoring/ecosystem: continuous vendor monitoring via the Riskey acquisition (third, fourth, nth-party signals); 400+ integrations (recent figures 430 to 450), 1,300+ automated tests including 146+ for AWS and 52 for Azure, tests can run hourly.
Implementation/pricing: VRM setup under one day with an existing identity provider; ~30-minute AI-assisted vendor reviews. VRM add-on around $300 per vendor per year, or about $600 bundled with Continuous Monitoring.
Limitations: no contract lifecycle management; limited board-level TPRM portfolio reporting; no proprietary vendor security rating; SOX financial process controls not native.
Customer signals: BVNK, MoonPay, Tyro Payments; SOX ITGC use at Ginkgo Bioworks and Taboola.
Verdict: best fit if your IPO plan needs one platform to run SOC 2, stand up SOX ITGC, and operationalize vendor oversight. If you need managed analyst services or board-ready vendor portfolio reporting, compare TPRM-specialized options.
Optro rebranded from AuditBoard in March 2026. It keeps the same product family public-company SOX teams know: SOXHUB (SOX program management), CrossComply (multi-framework compliance), and a connected TPRM module. More than half of the Fortune 500 use it, and it is one of the most common SOX systems Big Four auditors are comfortable testing.
Ideal for: late-stage fintechs (often 500+ employees) running or standing up a formal SOX program, where Finance/Internal Audit own SOX 404 and Security owns SOC 2, and a Big Four firm is expected.
Core capabilities: SOXHUB runs SOX 404 end to end (risk assessment, narrative documentation, walkthroughs, control testing, deficiency tracking, management response). Out-of-the-box content covers ITGC and key financial process controls including revenue, order-to-cash, and procure-to-pay. CrossComply extends to SOC 2 and ISO 27001; TPRM handles inherent-risk tiering, assessments, and remediation.
SOC 2/monitoring: lacks the compliance-automation flywheel (Trust Center, hourly tests, AI questionnaire review); continuous vendor monitoring relies on SecurityScorecard or BitSight.
AI: Optro AI for control mapping, document analysis, and narrative drafting; acquired FairNow in 2025 for AI governance. Enterprise-process AI rather than self-serve vendor-review agents.
Implementation/pricing: enterprise deployment, typically a few months to a couple of quarters, often partner-supported; quote-based pricing commonly in the high five to six figures annually.
Limitations: heavier and slower than compliance-automation platforms; TPRM is a module, not the centerpiece; no Trust Center; longer rollouts with professional services.
Verdict: choose Optro if full SOX 404 depth (ITGC plus financial process controls) and audit-firm fluency top your list. For SOC 2 day-to-day, a Trust Center, and AI-compressed vendor reviews, you will likely pair it with another platform.
3. OneTrust: enterprise GRC depth alongside privacy and ethics
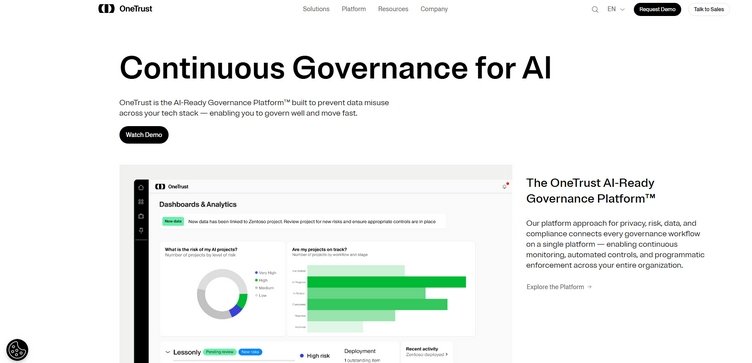
OneTrust grew from privacy management into a broad GRC suite with a substantive third-party risk module, serving 14,000+ customers across regulated industries. It fits when vendor oversight has to live next to privacy, ethics, and ESG in one control fabric.
Ideal for: mid-market and enterprise fintechs (typically 250+ employees) with multi-jurisdictional exposure (EU, UK, US state privacy laws) and an established privacy program.
TPRM capabilities: full vendor lifecycle (tiering, risk rubrics, questionnaires, evidence, remediation, reassessment). The Vendorpedia exchange offers 6,000+ pre-completed vendor profiles.
SOC 2/SOX: supports SOC 2 program work but not as a fast-path; no out-of-the-box SOX 404 / ITGC content, a real gap for IPO programs.
Monitoring: continuous monitoring usually built on BitSight, SecurityScorecard, or RiskRecon (separate subscriptions).
Framework breadth: pre-built mappings across 20+ standards including DORA, NIS2, PCI DSS, and GDPR. Third-Party Risk Agent launched September 2025 with PDF-limited analysis; roughly 100 integrations, fewer than 50 out-of-the-box evidence collectors; SAP Ariba and ServiceNow are common pairings.
Pricing: small-business plans around $600 per month; enterprise deployments commonly $50K to $300K per year; the TPRM module $40K to $500K per year. Breadth comes partly from 11+ acquisitions, adding admin overhead.
Limitations: no out-of-the-box SOX 404 / ITGC; continuous monitoring depends on paid feeds; AI less mature; longer implementation; no fast-path SOC 2 flywheel.
Verdict: right when vendor risk must sit alongside privacy, ethics, and ESG in one enterprise fabric and you can absorb a longer rollout. To consolidate SOC 2, SOX ITGC, and AI-assisted reviews into one fast-moving platform, OneTrust typically needs pairing.
4. Prevalent (Mitratech): bank-grade TPRM depth
Prevalent is a pure-play TPRM platform with more than two decades of specialization, acquired by Mitratech in October 2024 and rated a Strong Performer in Forrester's Third-Party Risk Management Wave (Q1 2026). It is the heavyweight option when vendor risk itself is the program.
Ideal for: later-stage fintechs (often 500+ employees) with a dedicated TPRM function, bank-partner due diligence, or multinational regulatory requirements.
Core capabilities: full vendor lifecycle with 800+ pre-built assessment templates mapped across security, privacy, and financial-services requirements; inherent and residual risk scoring on a likelihood-and-impact model; shared assessment repositories via Vendor Intelligence Networks.
Continuous monitoring: 2,000+ data sources across five domains (cyber, operational, reputational, financial, regulatory), correlated with assessment results.
SOC 2/SOX: maps vendor responses to AICPA Trust Services Criteria and to SOX requirements for third-party oversight, but does not deliver SOC 2 for your org or SOX ITGC automation/testing.
Discovery/AI/integrations: no automated vendor discovery or shadow-IT detection; AI is NLP/ML document analysis; integrations target TPRM workflows (CLM, procurement) and risk feeds, not infrastructure testing.
Implementation/pricing: weeks to months, with "clunky" and "dated UI/UX" feedback and Forrester notes on workflow inflexibility; enterprise quote-based pricing with optional managed services.
Limitations: no GRC/compliance automation for your own SOC 2; no Trust Center; no automated discovery; longer implementation.
Verdict: choose Prevalent for bank-style TPRM depth, broad regulatory mapping, and multi-domain continuous monitoring. To collapse SOC 2, SOX ITGC, and vendor oversight into one platform, expect to add complementary tools.
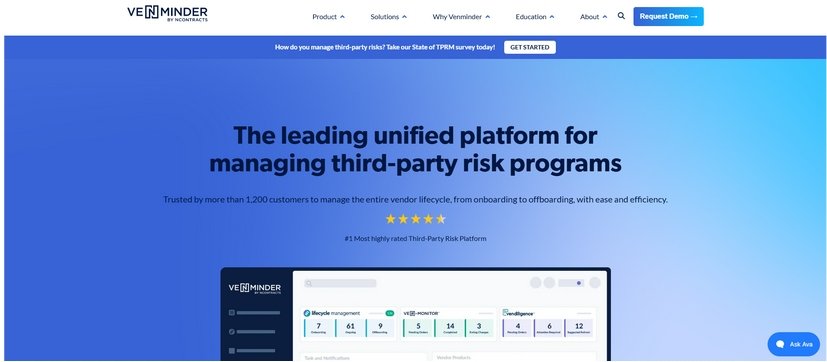
5. Venminder: continuous oversight with managed services built in
Venminder is a TPRM platform for regulated financial-services teams that want to outsource a share of vendor due diligence. It pairs software with managed services where certified analysts review vendor materials and deliver risk-rated outputs. Venminder was acquired by Ncontracts in September 2024 (Hg Capital-backed); it has 1,200+ customers, and the combined entity serves 5,000+.
Ideal for: lean compliance teams (often 1 to 5 people), banking/financial-services orgs optimizing for FFIEC-style oversight and examiner-ready reporting, and teams that value contract/SLA oversight.
Core capabilities: risk assessments with configurable scoring; template-driven questionnaires (including SIG variants) via a vendor portal; oversight and issue management; contract and SLA management with Venminder paralegals extracting key dates and renewal notifications. VenDiligence managed services use certified analysts (CISSP, CTPRP, CISA, CPA) to produce risk-rated reports.
SOC 2 fit: does not help you achieve SOC 2; its SOC Assessment service is an analyst-led review of a vendor's SOC 1 or SOC 2 report, including subservice organizations and complementary user entity controls (CUECs).
SOX: no explicit SOX 404 or ITGC support; plan a separate SOX approach.
Monitoring/integrations: Venmonitor integrates with SecurityScorecard and ArgosRisk across cyber, business health, privacy, ESG, and adverse-media signals; pre-built integrations include RSA Archer, SecurityScorecard, and ArgosRisk, with an API add-on.
Implementation/pricing: 30 to 90 days, code-free. Professional estimated $50,000 to $75,000 per year; Enterprise around $125,000 per year (AWS Marketplace), both with unlimited users and vendors; managed services priced per assessment.
Signals/limitations: 4.6/5 Gartner Peer Insights, 4.7/5 G2, Forrester Strong Performer; named customers include Billtrust, NewRez, Nations Lending, and MassHousing, with Flushing Bank and Frost Bank case studies. VRM-only with no GRC automation, no automated discovery, no AI questionnaire automation, limited integrations, and "rudimentary" reporting per Forrester.
Verdict: strong when capacity and expertise are the constraint and you want platform-plus-analysts diligence with contract oversight. To consolidate SOC 2 evidence, SOX ITGC, and VRM into one system, Venminder adds tool sprawl rather than reducing it.
Conclusion: Bridging SOC 2 and SOX, one vendor list, two audits
In most fintechs, SOC 2 lives with Security and SOX 404 with Finance, and your vendors sit in the overlap. Treat them as two programs and you get two inventories and two sets of audit questions that never reconcile. Build one vendor register that serves both audits instead.
Build one third-party inventory. Tag each vendor with two questions: does it handle customer data in your SOC 2 scope, and does it touch systems or reports that roll into your financial statements? The highest-scrutiny group is the vendors that are both.
Collect the right evidence for the overlap vendors. Pull the vendor's SOC 2 report (security controls) and SOC 1 report or equivalent (financial-control design), and store both under the same vendor record.
Cross-reference controls so one file supports two checks. If a vendor's change-management clause supports SOC 2 CC8, note that it also supports SOX ITGC Change-Management CM-1. Repeat for access reviews, incident response, and backup testing.
Hand auditors a consolidated register showing which vendors matter to SOC 2, which to SOX, which to both, and where the evidence lives. That cuts follow-up meetings and keeps your IPO timeline from stalling in evidence-chasing.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org







 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org










Leave a Reply