





Karsten Wenzlaff, Advisor
August 26th, 2025
Karsten Wenzlaff is a Crowdfunding and Fintech Expert from Germany. He is Secretary-General of Digit[...]


January 27, 2026 | NCFA Resource | Open Banking And Consumer Driven Finance, Risk Compliance And Regtech, Artificial Intelligence And Data
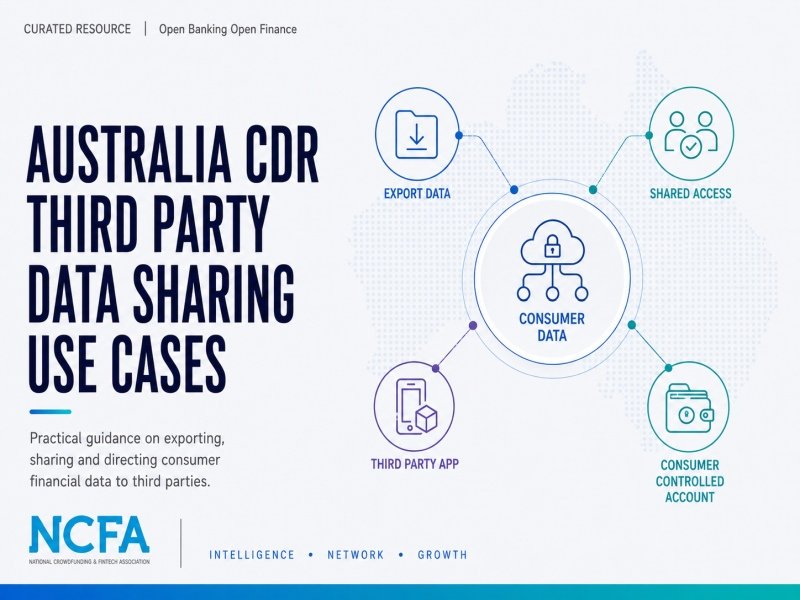
On January 27, 2026, Australia’s Consumer Data Right updated its Third Party Data Sharing Use Cases with practical examples showing how consumers can export financial data, give another person access, send data to another application or direct it into an account they control.
The Australian Competition and Consumer Commission developed the guidance with input from Treasury. It tackles a straightforward product question. After an accredited provider receives a consumer’s financial data, what can the consumer do with it next?
The answer depends on who initiates the sharing, where the information goes and who controls the destination. Those details affect consent, privacy and the provider’s responsibilities.
The guidance organizes third party sharing into four situations:
Who initiates the sharing is the key distinction. The ACCC says these consumer directed scenarios are unlikely to raise compliance concerns when the consumer makes a clear and informed choice. Downloading data, configuring access or instructing the provider to send information helps establish that the consumer chose the disclosure.
If the provider is making the disclosure itself, the permitted use and disclosure rules apply. The provider needs the authority and consent required under Australia’s Consumer Data Right rules.
That difference becomes concrete in product design. Letting someone download transaction history for personal analysis carries different responsibilities from automatically sending customer information to another company. Giving an accountant controlled access inside an SME finance platform is also different from transmitting the data outside that service.
Where the financial data remains inside the accredited provider’s service, the provider continues to carry the relevant Consumer Data Right obligations. These include privacy safeguards covering data security and the destruction or de-identification of information that is no longer required.
When consumers send their data outside that environment, they need to know how the recipient will handle it. The ACCC says providers should explain that other privacy laws may apply and encourage consumers to review the recipient’s data handling policies.
The same framework can support a single disclosure or recurring sharing for a defined period. The provider must hold the collection and use consents required for the service. Consumer Data Right consent generally lasts for up to 12 months, while some business consumer consents can extend for up to seven years.
Fintech product teams can use these examples when building financial data portability into real services. A personal finance app could let customers export transaction data for their own analysis. An SME platform could give an accountant controlled access to business records. A lending or cash flow application could let customers send selected information into another service they already use.
Compliance and legal teams can review the same features by asking a few direct questions. Who initiated the disclosure? Who controls the destination? Does the information stay inside the accredited service? What consent supports the sharing? Which obligations continue once the data leaves?
Banks and other financial institutions can use the examples to anticipate how customers may expect data portability to work. Consumers are unlikely to organize their behaviour around regulatory terminology. They will want financial information to work with budgeting software, accounting systems, lending applications, analytics tools and other services they choose.
Canada will face similar product questions as Consumer Driven Banking reaches implementation. Canada Open Banking And Consumer Driven Banking Rules tracks accreditation, authentication, consent, data sharing, security and liability requirements. Australia’s examples show what product teams have to consider after the first regulated transfer, when a customer wants to reuse the information somewhere else.
Standardized financial data can support credit assessment, fraud detection, cash flow analysis and financial guidance as well. NCFA’s Open Banking Decision Intelligence looks at how firms can turn permissioned financial data into better decisions. Third party sharing gives consumers and businesses more control over which tools can participate in those workflows.
The four examples are specific enough to use in product and compliance discussions. Teams can look at an export button, an accountant access feature, an application-to-application transfer or recurring sharing arrangement and ask exactly who controls the data at each point.
The guidance also shows why interface design and compliance cannot be separated. A button that lets the consumer choose where information goes can create a different regulatory position from a service that sends the same information on its own. Consent, control of the destination and whether the provider continues to hold the data all affect the answer.
That's useful context for Canadian teams working through consent and downstream data use. Canada can define who participates in regulated sharing and how financial institutions transfer data to accredited recipients. Customers will still want to download that information, share it with professionals, use it in another application or authorize access over time.
Australia’s rules do not determine what Canadian firms can do. The two countries have different legislation, privacy requirements, accreditation models and regulatory terminology. The Australian examples are useful because they expose practical questions Canadian product, compliance and policy teams will also have to answer.
The ACCC also makes clear that the article is general guidance. Whether a particular implementation complies with Australia’s Consumer Data Right depends on the circumstances, and providers remain responsible for assessing their legal obligations.
Consumer Data Right (Australian framework, participants and consumer information)
Legal Obligations For Data Recipients (collection, consent, use and disclosure requirements)
CDR Privacy Safeguard Guidelines (privacy requirements for handling consumer financial data)
Canada’s Open Banking Strategy Starts With Trust (consent, fraud, liability and consumer protection in Canada)
 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
 |  |  |
|---|---|---|
 |  |  |



August 26th, 2025

January 4th, 2024

June 1st, 2021

September 9th, 2020

July 9th, 2018

January 3rd, 2018

September 25th, 2017

June 20th, 2017

May 10th, 2017

December 14th, 2016

Leave a Reply