Category Archives: Innovation and Resources

DuckDice Canada Crypto Casino Exciting Features

Jun 30, 2026

AI Image – Gaming and crypto in a modern workspace

DuckDice Crypto Casino Overview for Canadian Players and Gamers

For those exploring a fresh online entertainment experience, this platform offers an impressive array of functionalities that cater to diverse preferences. Take advantage of the enticing welcome bonuses designed to give newcomers a robust start, enhancing their initial experience significantly.

The interactive environment features a user-friendly interface that simplifies navigation, making gameplay intuitive for both novices and seasoned players. Real-time statistics and analytics allow participants to track their performances and adjust their strategies accordingly, leading to tailored gaming sessions.

Additionally, engagement opportunities abound through community-driven events and tournaments that encourage friendly competition. Loyalty programs reward consistent players with perks and incentives, fostering a welcoming atmosphere. All these elements contribute to a dynamic and enjoyable online experience that is hard to resist.

Innovative Game Selection and Formats

An extensive array of gaming options caters to various preferences, ensuring that players can find something that suits their style. Unique titles often feature inventive gameplay mechanics, elevating the overall experience. Look out for offerings that combine traditional casino elements with modern twists, such as skill-based components or story-driven adventures, especially when exploring platforms in the crypto casino Canada segment.

Live-action games have transformed the entertainment landscape, allowing players to engage with real dealers in real-time. This format delivers an immersive atmosphere that mimics the ambiance of a physical venue, fostering social interaction. Consider trying out themed live shows, which blend popular culture elements into classic formats for an added layer of enjoyment.

Add-on features like progressive jackpots or customizable game settings enhance user engagement and provide opportunities for increased rewards. These options encourage diverse play styles, appealing to both casual gamers and high rollers. Regularly updated libraries help maintain interest, as new titles are introduced frequently, offering fresh and exciting challenges to explore.

Exclusive Promotions and Loyalty Programs

To enhance the gaming experience, consider engaging with various limited-time offers and promotional events. Often, these promotions come in the form of deposit bonuses, where additional funds are credited to your account upon making a qualifying deposit. Pay attention to the details, as each promotion may have specific requirements.

Another attractive option is the referral program. By inviting friends to join, players can earn bonuses or free credits for each successful signup. This not only provides rewards but also creates a sense of community among users, fostering interaction and competition.

Loyalty schemes are designed to recognize and reward consistent participation. Players accumulate points based on their activities, which can later be exchanged for bonuses, gifts, or even exclusive experiences. Regularly check the loyalty program tiers to maximize benefits as you advance through levels.

Seasonal promotions often bring additional excitement, aligning offers with holidays or significant events. Participating during these times can lead to substantial bonuses and unique prizes. Ensure to monitor announcements for these opportunities, as they can significantly boost the gaming experience.

Lastly, subscribing to newsletters or notifications is a practical way to stay informed about the latest campaigns. This ensures that players never miss an opportunity to take advantage of exclusive offers, enhancing both engagement and rewards in the long run.

User-Friendly Interface and Experience

To enhance your engagement, the platform offers an intuitive layout designed for seamless interaction. Clear navigation bars and organized menus ensure that all available activities are easily accessible, minimizing time spent searching for options.

The color scheme is soothing, with a modern aesthetic that enhances visibility. Users can quickly identify sections such as betting options, account management, and help resources. This thoughtful design allows users to focus on their gaming experience without distractions.

  • Responsive Design: The site is optimized for both desktop and mobile use, maintaining functionality across devices.
  • Quick Load Times: Pages load rapidly, ensuring that users can jump from one activity to another without delays.
  • Clear Call-to-Action Buttons: Important features like "Join," "Withdraw," and "Deposit" are highlighted, which helps in smooth transactions.

Customer support is easily accessible, with a dedicated help center and live chat functionality. This feature enables users to receive assistance quickly, contributing to a positive overall experience.

Regular updates and user feedback integration demonstrate commitment to enhancing the interface. Continuous monitoring and tweaks based on popular user requests foster a community-focused environment, where player satisfaction is prioritized.

Secure Transactions and Cryptocurrency Options

A wide range of multi-currency wallets is recommended for seamless and secure financial transfers. Look for options that support popular coins including Bitcoin, Ethereum, and various altcoins, enabling users to deposit, withdraw, and place bets with their preferred digital assets.

Security measures play a critical role in the reliability of online transactions. Implementing two-factor authentication (2FA) adds an extra layer of protection for users. Always ensure that the platform utilizes encryption protocols (like SSL) to keep personal and financial data secure from unauthorized access.

Consider utilizing platforms that offer blockchain technology for transparency. Each transaction is recorded on a public ledger, making it easier to verify and trace payments. This not only enhances privacy but also builds trust between users and the service provider.

For enhanced convenience, many users prefer platforms that enable direct cryptocurrency payments without the need for currency conversion. This can mitigate the risk associated with volatile exchange rates and hidden fees during conversions.

Cryptocurrency Transaction Speed Typical Transaction Fees
Bitcoin 10 minutes $1-10
Ethereum 15 seconds $0.50-5
Litecoin 2.5 minutes $0.01-0.05
Ripple 3-5 seconds Minimal

Evaluate the transaction limits imposed by the service. Understanding the minimum and maximum deposit and withdrawal thresholds can help manage your gameplay or betting strategy. This information is often available in the FAQ section or customer support.

Ep27-Mar 1: Blockchain Gaming and Esports with Shidan Gouran

Regularly monitor the platform’s policy on transaction discrepancies. A responsive customer support team is beneficial in resolving any issues swiftly, ensuring a hassle-free gaming experience. Always choose platforms that offer clear communication channels for such concerns.


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Canada’s Open Banking Regulatory Intelligence Guide

Jun 29, 2026 | NCFA Resource | Open Banking Open Finance, Regulation And Policy

Last updated: September 11, 2026

Canada open banking and Consumer Driven Banking regulatory intelligence guide

Canada Open Banking Rules For Readiness And Consultation

NCFA has published a new Regulatory Intelligence guide to Canada Open Banking and Consumer Driven Banking Rules. The interactive resource organizes the proposed regulations, implementation requirements, consultation questions and strategic issues shaping Canada’s regulated open banking framework.

For a broader view of Open Banking and Consumer-Driven Finance, including the Canadian market map, 146 learning modules, company intelligence, global benchmarks and interactive discussions, explore NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence.

The guide tracks accreditation, data scope, consent, authentication, security, technical standards, liability, reporting, complaints, national security review, fees and administrative monetary penalties. It also explains why consumer trust, fraud prevention and clear accountability are central to implementation. For further analysis, see Canada's Open Banking Strategy Starts With Trust.

What It Does In Practice

The resource gives readers a structured way to understand what the proposed Consumer Driven Banking Regulations would require before final rules are published.

Instead of treating the regulations as one long legal document, the guide breaks them into operating topics. Each section separates regulatory requirements, implementation work, consultation considerations and NCFA’s strategic perspective.

Canada’s open banking framework is progressing from policy design into regulatory implementation. Firms need to understand more than API access. They need to prepare evidence for accreditation, consumer consent flows, registry checks, authentication records, security safeguards, breach response, complaint procedures, service standards, reporting obligations and board level accountability.

The 60-day Canada Gazette consultation closed on August 26, 2026. The proposed regulations remain subject to finalization, while firms continue preparing for accreditation, supervision, data-sharing, consent, security and operational requirements.

Who Gets Value

This resource is useful for fintech founders, open banking platforms, financial institutions, credit unions, payment service providers, data aggregators, regtech providers, compliance teams, investors, policymakers and industry associations.

It is especially useful for organizations assessing accreditation, product design, consent architecture, data sharing duties, technical standards, cybersecurity, consumer protection and implementation costs.

Strengths And Limits

The strength of this resource is its focus on regulatory readiness. It converts the proposed Consumer Driven Banking Regulations into a practical intelligence layer that can support planning, consultation, product design and ecosystem coordination.

The guide connects the proposed regulations to Canada’s policy objectives, including stronger consumer protection, fraud mitigation, secure financial data sharing, competition and confidence in the open banking framework.

It also connects regulation to commercial opportunity. The guide identifies where read access, data portability, identity and income verification, cash flow analysis, embedded workflows, write access and open finance may create future product and infrastructure demand.

The regulations remain proposed and may change following consultation. Readers should use the guide for ecosystem intelligence and planning, not as legal, financial, investment, compliance or professional advice.

Key Resources

Canada Open Banking and Consumer Driven Banking Rules (primary NCFA Regulatory Intelligence guide)

NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence (market map, 146 learning modules, company intelligence, discussions and global benchmarks)

Canada's Open Banking Strategy Starts With Trust (consumer protection and fraud readiness)

Open Banking In Canada Opportunity Brief (commercial opportunity layer)

NCFA Financial Innovation Map (ecosystem context)

Proposed Consumer-Driven Banking Regulations (official Canada Gazette source)


National Crowdfunding and Fintech Association of CanadaThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Canada Open Banking and Consumer Driven Banking Rules

NCFA Regulatory Intelligence - Canada Open Banking And Consumer Driven Banking Rules
NCFA Canada | Regulatory Intelligence | Open Banking and Consumer Driven Banking | Last updated September 11, 2026 | Status proposed regulations, consultation closed
NCFA Regulatory Intelligence
This guide explains Canada’s open banking framework through the proposed Consumer Driven Banking Regulations, including accreditation, consent, data sharing, security, liability, supervision and implementation. Sources include the Canada Gazette, the Regulatory Impact Analysis Statement, the Consumer Driven Banking Act, Finance Canada, Bank of Canada materials and the Office of the Privacy Commissioner of Canada’s August 26 submission.
Canada Open Banking

Proposed Consumer Driven Banking Regulations

Canada Open Banking and Consumer Driven Banking Rules

Canada’s proposed Consumer Driven Banking Regulations establish the operating framework for open banking. They address accreditation, consumer consent, data sharing, security, technical standards, liability, complaints, reporting, national security review and enforcement.

Use this guide to understand the proposed requirements, the implementation work they create and the post-consultation issues that may affect banks, credit unions, payment service providers, fintechs, consumers and small businesses.

The 60-day consultation closed August 26, 2026. The regulations remain proposed while Finance Canada considers feedback and prepares the next regulatory steps. Firms can use the published draft for planning, but final requirements and implementation timing may still change.

For a broader view of Open Banking and Consumer-Driven Finance beyond the regulatory framework, explore NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence, including the Canadian Market Map, 146 learning modules, company intelligence, discussions, innovation themes and global benchmarks.

Canada’s Open Banking and Consumer Driven Banking Journey

Canada has advanced from open banking policy development into proposed Consumer Driven Banking Regulations under Bank of Canada oversight. The consultation closed on August 26, 2026. The current stage is regulatory finalization and supervisory preparation.
Launch read access and data mobility
Next write access
Consultation2018 to 2022 open banking policy review
Framework2023 to 2024 Consumer Driven Banking design
2026 Currentconsultation closed, final rules pending Bank of Canada supervision framework and implementation preparation
Read Accesslaunch phase secure data sharing and data mobility
Data Productsnear term verification, cash flow and embedded workflows
Write Accessnext phase payment initiation and account actions
Open Financelonger term broader financial product scope

Impact Analysis

Key figures from the Regulatory Impact Analysis Statement and proposed regulations.
$13.2BEstimated 10 year benefits
$457.7MEstimated 10 year costs
9MCanadians using data sharing services
680Affected businesses in central scenario
578Small businesses affected
$89,133Average annualized small business cost estimate
99.5%Monthly endpoint availability
$10MMaximum entity or ATPSP penalty

Regulatory Intelligence Explorer

Navigate the proposed regulations by topic. Each section separates requirements, implementation work, post-consultation issues to watch and NCFA’s strategic perspective.

Overview

Requirements The proposed regulations support implementation of the Consumer Driven Banking Act and create the operating layer for Canada’s open banking framework. They prescribe the data covered by the Act, accreditation information and requirements, accreditation fees, review timelines, revocation notices, accredited third party service provider requirements, national security information requirements, Ministerial review timelines, data sharing duties, exceptions to sharing, service standards, security safeguards, breach reports, responsible officer information, authentication steps, consumer signs, change notices, annual reporting, record keeping, liability related consumer notices, complaint procedures, technical standards body reporting, evidentiary privilege, assessments, administrative monetary penalties and coming into force rules.
  • Definition of Act and prescribed covered data
  • Accreditation applications for federal or provincial financial institutions, RPAA registered payment service providers, other entities and accredited third party service providers
  • Bank of Canada electronic application system, accreditation fee, refusal review and revocation processes
  • National security information package, Ministerial decision period, review period, extensions and review rights
  • Registry based verification before sharing data and exceptions where sharing can be withheld
  • Service standards for response times, endpoint availability, planned outages and traffic management
  • Security safeguards, breach reporting and responsible officer reporting
  • Authentication, acknowledgement and consent connected to secure data sharing
  • Notices, annual reporting, record keeping, liability, complaints, technical standards body reporting, assessments and violations
Implementation Organizations should build a regulatory inventory that maps each requirement to a system, policy owner, evidence file and supervisory reporting obligation. The Bank of Canada says its supervisory framework will cover participating entities, governance, risk management, operational resilience and monitoring of trends and issues. The first implementation work is not only API build. It includes accreditation evidence, national security information, data classification, registry checks, consent design, authentication records, breach playbooks, service monitoring, complaint intake, record retention, change notices, fee modelling, ATPSP contracts and board level accountability.
Post-Consultation Watch
  • Whether the framework gives enough implementation runway between final regulations, Bank of Canada guidance and coming into force
  • Whether proportionality is strong enough for small firms and RPAA registered payment service providers without reducing consumer trust
  • Whether guidance should clarify connections between fraud, consent, complaints, liability, security events and record keeping
  • Whether the technical standards body, conformance testing and service performance rules should be clearer before launch
  • Whether the cost and reporting model supports competition or favours organizations with existing compliance infrastructure
  • Whether consumers and SMEs will be able to understand which entities are accredited, which data is covered and how complaints or deletion requests work
August 26 Privacy Commissioner Submission The Office of the Privacy Commissioner of Canada supports the aims of consumer-driven banking and several privacy protections in the proposed regulations, but recommends changes before finalization.
  • Specify the individual data elements covered by the framework more clearly so consumers can understand what may be shared
  • Strengthen accreditation evidence in several pathways, including safeguards, complaints, authentication, dashboards, technical-standard evidence and selected insurance or integrity requirements
  • Narrow the consent exception for publicly available data so it does not capture information where a consumer has a reasonable expectation of privacy
  • Add an overarching requirement for safeguards appropriate to the sensitivity of the data as technology and threats change
  • Clarify coordination between the Privacy Commissioner and the Bank of Canada where privacy and supervisory responsibilities intersect
NCFA Perspective This is a trust and market structure test. Canada is defining the participation standard for a regulated financial data market. The strongest framework will not be the one with the most rules. It will be the one that makes safe participation practical, keeps consumer control understandable and lets credible new entrants compete without pushing the ecosystem into a narrow, incumbent led implementation path.

Application and Data

Requirements The regulations define the Act and prescribe the data to which the consumer driven banking framework applies. Covered data includes data relating to consumers of the covered products or services, account and product identifiers, the terms under which products and services are provided, balances or amounts owing, completed, pending and pre authorized transactions, and information about products or services available or offered to consumers. The data scope is tied to the products and services referred to in the Act and must be shared only through the regulated framework once the relevant duties apply.
  • Identity related data for consumers of covered products or services
  • Account numbers, branch numbers, transit numbers and other product or service identifiers
  • Product and service terms, including fees, interest rates and authorizations
  • Current and past balances or amounts owing
  • Completed, pending and pre authorized transaction data
  • Information about products or services available or offered to consumers, including terms
  • Historical limits apply in the data sharing rules for balances, transactions and available or offered products and services older than 24 months
  • Covered data must be tied to a valid data sharing request, participant verification, consumer authentication and consent
Implementation Participants need a data inventory that maps each covered category to source systems, product owners, API fields, consent screens, retention rules, deletion workflows, complaints, liability records and service monitoring. Data providers should identify where product terms, balances, transaction history and account identifiers are stored, how far history is available, what data is excluded, and how data quality issues will be handled when another participant relies on the information.
Post-Consultation Watch
  • Whether Finance Canada adopts the Privacy Commissioner’s recommendation to specify the individual data elements within each covered category more clearly
  • Whether the treatment of derived, inferred or enriched data needs clearer boundaries
  • Whether the 24 month historical limit is sufficient for SME finance, lending, accounting and cash flow use cases
  • Whether business accounts, joint accounts, delegated authority and multi user permissions need more detailed guidance
  • Whether future open finance expansion should be signalled earlier to reduce later redesign
  • Whether data quality, correction and dispute processes need a clearer connection to complaints and liability
NCFA Perspective Data scope is the first market boundary. A narrow read access model can still support verification, underwriting, cash flow analysis, switching, accounting and embedded workflows. The larger Canadian opportunity depends on whether this foundation can expand cleanly into write access, payment initiation and broader open finance without rebuilding the trust layer from scratch.

Accreditation

Requirements The accreditation rules prescribe different application pathways for federal or provincial financial institutions, RPAA registered payment service providers, other entities and accredited third party service providers. Applications must be submitted through the Bank of Canada electronic system. Common information includes legal and trade names, formation details, civic and mailing addresses, contact information, website, application contact, organizational and governance structure, regulatory or supervisory oversight, foreign open banking registration or accreditation status, designated officer or employee details, consumer complaint contact information, technical standard evidence and national security information. RPAA registered PSPs and other entities must also provide Canadian place of business declarations, whether they operate from a dwelling house, independent third party confirmation of security safeguards, insurance or guarantee evidence, and integrity and good character policies for individuals with significant responsibility. Other entities must additionally describe how they will meet specified Act requirements, complaint procedures, external complaints body membership status and estimated consumer numbers.
  • Federal or provincial financial institution applications include security compliance declaration, designated officer details, complaint contact, technical standard evidence and national security information
  • RPAA registered PSP applications include Canadian place of business, dwelling house declaration, independent security confirmation, technical standard evidence, insurance or guarantee and integrity policy or good character information
  • Other entity applications include similar information plus descriptions of how they will meet specified duties, complaint procedures, external complaints body membership and estimated consumer numbers
  • RPAA registered PSPs and other entities must maintain place of business, insurance or guarantee and integrity or good character requirements after accreditation
  • The accreditation fee is $2,500 in the first year and then indexed to September CPI, rounded to the nearest $100, with no decrease from the previous year
  • An applicant has 30 days to request Governor review of an accreditation refusal, and the Governor has 120 days after giving an opportunity to make representations to accredit or confirm refusal
  • Participating entities requesting voluntary revocation must provide consumers with name and contact, planned request date, impact assessment, deletion notice and complaint resolution information
  • A participating entity has 30 days to request Governor review of a notice of intent to revoke accreditation, and the Governor has 60 days after giving an opportunity to make representations to revoke or withdraw the notice
  • Former participating entities must notify consumers of revocation date, reasons, impact, deletion request requirement and complaint process
  • Accredited third party service provider applications include legal information, activity description, participating entity relationships, Canadian place of business, independent security confirmation, technical standard evidence, contract and policy information and national security information
Implementation Applicants should build a complete accreditation evidence file before applying. That file should include corporate and governance documents, regulatory status, technical standard evidence, security confirmation, insurance or guarantee evidence, complaint process, designated officer details, integrity policy, national security information, contracts with participants where relevant and consumer impact notices for potential exit. RPAA registered PSPs should map which information can be reused from RPAA registration and which requirements are new under CDB.
Post-Consultation Watch
  • Whether final accreditation rules adopt the Privacy Commissioner’s recommendations for stronger evidence in selected pathways, including safeguards, complaints, authentication, dashboards, technical-standard compliance, insurance or guarantees and integrity checks
  • Whether the independent third party confirmation of security safeguards should have defined qualifications or assurance standards
  • Whether insurance or guarantee sufficiency needs guidance so applicants can price participation
  • Whether the dwelling house declaration could create unnecessary ambiguity for remote first firms
  • Whether refusal, revocation and review timelines are workable for firms planning launch and funding milestones
  • Whether ATPSP accreditation requirements are clear enough for infrastructure providers that will support multiple participating entities
NCFA Perspective Accreditation sets the practical threshold for market participation. If evidence requirements are too light, the framework risks weak trust. If they are too heavy, innovation may concentrate among large institutions and compliance funded platforms. The policy challenge is not choosing between safety and competition. It is designing entry rules that reward credible operators without making participation uneconomic for the firms most likely to create new consumer and SME products.

Authentication and Consent

Requirements The proposed rules connect data sharing to verification, consumer authentication and consent. A participant receiving a request must verify the requesting entity and confirm through the registry that it is an accredited participating entity and not suspended in a way that prevents receiving data. A participant requesting data must verify the provider and confirm through the registry that the provider is accredited and not suspended in a way that prevents providing data. Authentication requires confirmation of the consumer’s authentication information using multi factor authentication. The consumer must acknowledge the requesting participant’s name, the nature of the request and the accounts from which the requested data will be provided before the data is shared and the consumer is redirected.
  • Requester and provider verification against the registry before sharing
  • Confirmation that accreditation has not been suspended or restricted by Bank conditions
  • Multi factor authentication of the consumer’s authentication information
  • Consumer acknowledgement of the requesting entity, nature of the request and relevant accounts
  • Data sharing only after verification, authentication and acknowledgement requirements are met
  • Renewal may be required after circumstances where data sharing was not required or consent has not yet been renewed
  • Consent evidence must connect to records, deletion requests, liability, complaints and annual reporting
Implementation Participants need registry lookup, accreditation status checks, suspension condition logic, MFA, acknowledgement capture, consent evidence, renewal workflows, revocation and deletion links, exception handling and audit trails. Authentication and consent should not be built as a user interface layer only. They need to produce evidence that can support annual reporting, complaint resolution, breach response, liability allocation and supervisory review.
Post-Consultation Watch
  • Whether the registry verification workflow is operationally clear for real time data sharing
  • Whether MFA requirements align with existing bank and fintech authentication journeys
  • Whether consent and acknowledgement guidance makes the sharing scope sufficiently specific for consumers to understand what information is captured
  • Whether consent renewal triggers and failed renewal situations need clearer examples
  • Whether consumer dashboards, consent receipts and cross provider visibility should be addressed in guidance
  • Whether consent evidence is sufficient to resolve liability, complaint and deletion disputes
NCFA Perspective Consent is one of the highest trust points in the framework. The market will not fail because consent screens are hard to build. It will fail if consumers cannot understand them, if participants cannot prove what was authorized, or if revocation and deletion are too hard to execute. This is where compliance design and product design become the same problem.

Security

Requirements The regulations prescribe detailed security safeguards for participating entities. Safeguards include vulnerability identification and remediation, regular updates, secure default configuration, security software, robust authentication, access management policies, unique accounts, data encryption and backup, network security controls, external storage policy, bans on unauthorized devices and applications, network traffic monitoring, suspicious content controls, inventory of systems and devices, third party service provider contract protections, employee cyber threat training and an incident response plan with log auditing and periodic exercises based on extreme but plausible scenarios. Safeguards must be proportionate to data sensitivity and network segmentation is permitted. Federal and provincial financial institutions are presumed to have implemented safeguards unless OSFI or the relevant provincial authority has identified deficiencies and directed remediation.
  • Vulnerability management and regular updates
  • Secure configuration by default
  • Security software on relevant systems and devices
  • Robust authentication methods
  • Role based access management policies
  • Unique accounts and minimized shared accounts
  • Encryption and regular backup of stored data
  • Network security controls for data in transit
  • External storage policy
  • Prohibition on unauthorized devices and applications
  • Monitoring and control of network traffic
  • Suspicious content identification, quarantine or blocking
  • Inventory of systems and devices used for sharing and storing covered data
  • Contract terms requiring third party service provider protection of data
  • Employee cyber threat training and ongoing updates
  • Incident response plan with detection, response, recovery, log auditing and scenario exercises
  • Responsible officer or employee details must be provided to the Bank without delay after designation
  • Breach reports to the Bank must include circumstances, known cause, date or period, affected data, number of consumers, potential impacts, mitigation and contact information
Implementation Participants should treat security as an accreditation and operating evidence file. Required work includes asset inventory, vulnerability program, configuration standards, endpoint and system security, identity and access controls, encryption, backup, network monitoring, third party contract review, cloud and vendor risk, cyber training, incident response testing, breach reporting templates and escalation paths to the Bank. Security records should be aligned with annual reporting, complaint records and liability evidence.
Post-Consultation Watch
  • Whether final rules add the Privacy Commissioner’s recommended overarching requirement for safeguards appropriate to data sensitivity as technology and threats change
  • Whether independent third party confirmation should follow a defined assurance framework
  • Whether breach reporting timing, consumer notification thresholds and report updates need more prescriptive examples
  • Whether third party and cloud contract requirements should include subcontractor and data location obligations
  • Whether small entrants can meet the same security evidence burden without shared infrastructure
  • Whether fraud, identity, authentication and cyber controls should be addressed together in Bank guidance
NCFA Perspective Security is the trust anchor. Consumer driven banking exists partly to replace unsafe credential sharing with supervised data access. That only works if security is operationally real, not a paper control. The framework must be strong enough to protect consumers and flexible enough that security compliance does not become the reason only the largest organizations can participate.

Technical Standards

Requirements The technical standard provisions operate through the Act and the regulations. Applicants must provide evidence of compliance with the technical standard referred to in the Act. Participating entities must declare technical standard compliance in annual reports. Data sharing systems must meet response time expectations consistent with generally accepted international standards, maintain 99.5 percent monthly availability excluding planned outages, and use traffic management only for technical stability or security in a proportionate, non discriminatory way. The technical standards body must submit an annual report to the Bank within seven days after each anniversary of its designation order. That report must describe vulnerabilities in the technical standard or standards body that had or could have had an impact on the security of data sharing, non technical descriptions of changes to data fields, features, functionality or other security relevant aspects of the technical standard, rationale and decision process for those changes, and changes relevant to the body’s designation.
  • Applicants must provide technical standard compliance evidence
  • Participating entities must report annual technical standard compliance
  • API or electronic system response times must align with generally accepted international standards
  • Data sharing systems must meet 99.5 percent monthly availability, excluding planned outages
  • Rate limiting, throttling and preferencing are restricted to stability and security purposes
  • Traffic management must be proportionate, non discriminatory and must not degrade consumer outcomes
  • Technical standards body annual report is due within seven days after each designation anniversary
  • Technical standards body must report vulnerabilities, causes, impacts, mitigation and contact person
  • Technical standards body must describe changes to data fields, features, functionality or security relevant aspects, plus rationale and decision process
  • Technical standards body must describe changes relevant to its designation factors
Implementation Technical teams need API inventory, conformance evidence, performance monitoring, availability measurement, outage notification, traffic management governance, test environment planning, error handling, historical data readiness, change management and documentation that can support Bank supervision. Firms should prepare for technical standard versioning and for annual evidence that systems remained compliant through the reporting year.
Post-Consultation Watch
  • Whether the technical standards body should be identified or its governance clarified before final implementation planning
  • Whether conformance testing should be mandatory before production access
  • Whether response time expectations should be converted into measurable standards
  • Whether 99.5 percent availability is sufficient for higher value financial workflows
  • Whether public reporting of availability, outages and API performance would strengthen trust
  • Whether technical standard changes should have notice periods, backwards compatibility expectations and migration timelines
NCFA Perspective Technical standards are where the framework becomes real infrastructure. Canada’s competitive position will depend less on whether APIs exist and more on whether standards, testing, versioning and change management let participants build once and scale. Ambiguity here can turn regulatory permission into integration drag.

Liability

Requirements The liability provisions clarify consumer responsibility and the allocation of responsibility between participating entities. Every participating entity must inform consumers of the consequences of gross negligence or, in Quebec, gross fault in safeguarding authentication information. It must advise consumers of reasonable measures they can take to safeguard authentication information. It must not intentionally mislead consumers about the extent of their liability or adopt policies that presume consumer liability contrary to the Act. Where a consumer is not liable for a financial loss arising from loss, unauthorized access or unauthorized use of data shared under the Act, liability between participating entities is determined by where the loss, access or use occurred. The requester is liable to the extent it occurs in relation to the requester securely receiving or managing the data. The provider is liable to the extent it occurs in relation to provider authentication or secure provision of the data.
  • Consumers must be informed about gross negligence or gross fault consequences for authentication information
  • Consumers must be advised of reasonable safeguarding measures
  • Participants must not mislead consumers about liability
  • Participants must not adopt policies presuming consumer liability contrary to the Act
  • Requester liability follows failures connected to receiving or managing data
  • Provider liability follows failures connected to authenticating the consumer or securely providing data
  • Liability evidence depends on consent, authentication, registry checks, transmission logs, receipt records, complaint files and incident records
Implementation Participants should prepare consumer notices on authentication information, avoid default liability language, align customer support scripts with the Act, and preserve records that show where an event occurred. Liability operations require authentication logs, consent evidence, registry verification, data transmission records, receipt confirmations, access logs, incident investigations, complaint handling and remediation decisions.
Post-Consultation Watch
  • Whether gross negligence or gross fault communications will be understandable for consumers
  • Whether liability allocation is clear enough for multi party flows involving ATPSPs
  • Whether examples should clarify direct financial loss, unauthorized access, data loss and failed revocation
  • Whether consumer support and complaint processes need stronger alignment with liability rules
  • Whether records required to prove liability should be specified more explicitly
  • Whether fraud and scam scenarios are sufficiently covered by the liability architecture
NCFA Perspective Liability will be tested in edge cases, not in clean diagrams. The strategic issue is whether the framework can resolve consumer harm quickly without turning every incident into a multi party blame exercise. Clear evidence rules can build trust. Unclear responsibility can undermine adoption even if the technology works.

Reporting Requirements

Requirements The proposed regulations require change notices, annual reports and records sufficient to demonstrate compliance. Changes that must be reported include names or contact information, organizational structure, RPAA registration status for entities accredited under the RPAA pathway, Canadian regulatory oversight, foreign open banking registration or accreditation, designated officer contact, complaint contact, external complaints body membership, significant responsibility individuals and integrity status, insurance or guarantee sufficiency, technical standard compliance and national security information. Some changes must be reported within 30 days after they occur, some as soon as feasible after awareness, some at least 30 days before taking effect and some at least 60 days before taking effect. Annual reports must provide monthly metrics on non sharing events, express consents, consent renewals, withdrawals, deletion requests, system availability, data sharing counterparties, successful data provisions and average response time. They must also include changes, policy and procedure updates, breach summaries, planned and unplanned outages, technical standard declaration, financial metrics, supervisory deficiency declarations for financial institutions and security safeguard implementation descriptions for certain accredited entities. Records must be sufficient to demonstrate compliance, kept electronically in a format intelligible to the Bank, retained for five years after they cease to demonstrate current compliance unless otherwise specified, and protected against loss, destruction, falsification, inaccuracy and unauthorized access or use.
  • Notice of change categories cover identity, structure, registration, oversight, foreign accreditation, officers, complaints, EBC membership, significant responsibility individuals, insurance or guarantee, technical standard compliance and national security information
  • Notice timing includes 30 days after occurrence, as soon as feasible, at least 30 days before certain changes and at least 60 days before certain data storage or processing country changes
  • Annual report metrics include monthly non sharing counts and reasons
  • Annual report metrics include express consents, renewals, withdrawals and deletion requests
  • Annual report metrics include uptime, data sharing counterparties, delivery counts and average response time
  • Annual report must include changes, policy updates, breach summary, outages, technical compliance declaration and financial metrics
  • Records must demonstrate compliance with the Act and regulations
  • Records must be electronic and intelligible to the Bank
  • Records must generally be kept for five years after they cease to demonstrate current compliance
  • Records must be protected from loss, destruction, falsification, inaccuracies and unauthorized access or use
  • ATPSPs must keep compliance records, contracts with participants and policies or procedures relating to services they perform for participants, with the same electronic form and protection rules
  • Certain supervisory information, Bank directions, compliance agreements and supervisory correspondence are privileged for civil evidence purposes, with specified exceptions for use by the Minister, Governor, Bank, Attorney General of Canada, participants or ATPSPs in certain proceedings
Implementation Participants need a compliance data model that captures events as they happen. Manual annual reporting will be fragile. Systems should collect consent events, renewal events, withdrawal events, deletion requests, non sharing reasons, uptime, response time, outage data, breaches, policy changes, material changes, complaint records and financial metrics. Record retention and protection should be built into the architecture before production data flows begin.
Post-Consultation Watch
  • Whether the notice timing categories are clear enough for operational teams to apply consistently
  • Whether annual reporting should align with RPAA and other Bank of Canada reporting regimes where possible
  • Whether public transparency reporting on uptime, outages, complaints and non sharing events would strengthen trust
  • Whether smaller firms need proportional reporting without weakening supervisory visibility
  • Whether five year record retention is practical across all evidence categories
  • Whether privileged supervisory information rules strike the right balance between supervision, litigation risk and transparency
NCFA Perspective Reporting and records are the hidden operating system of regulated open banking. They may matter more than any single product feature because they determine whether trust can be audited, problems can be reconstructed and smaller firms can participate without building a bank sized compliance department.

Complaints

Requirements The regulations require complaint handling information at accreditation and connect complaints to revocation notices, consumer contact information, external complaints body membership and records. Other entity applicants must describe intended complaint procedures, the officers or employees to be designated for complaint responsibilities, and the contact information consumers will use. A participating entity requesting revocation or a former participating entity whose accreditation has been revoked must provide consumers with information about the process for resolving outstanding complaints. Annual reporting must describe changes to complaint related procedures. Record keeping must support compliance and complaint evidence. ATPSPs must keep contracts and related policies or procedures where they perform activities for participating entities.
  • Complaint contact information is required in accreditation applications
  • Other entity applications must describe complaint procedures and designated complaint roles
  • External complaints body membership status is required for certain applicants
  • Revocation and former participant notices must include complaint resolution information
  • Complaint processes connect to annual reporting and record keeping
  • Complaint evidence should align with consent, authentication, data sharing, security, breach and liability records
Implementation Participants should design complaint intake, triage, escalation, evidence review, consumer communication, external complaints body routing, remediation, root cause analysis and reporting. Complaint workflows should identify whether the issue relates to access, failed sharing, revoked consent, deletion, fraud, data quality, breach, liability or service availability.
Post-Consultation Watch
  • Whether complaint timelines and escalation expectations should be more explicit
  • Whether consumers will know whether to contact the provider, requester, ATPSP, bank or external complaints body
  • Whether SMEs need distinct complaint pathways for business account use cases
  • Whether complaint data should feed into supervisory or public transparency reporting
  • Whether complaints involving data quality, failed sharing, deletion or fraud require specific treatment
NCFA Perspective Complaint handling will be a public trust signal. Consumers rarely judge infrastructure by how it works on a perfect day. They judge it by what happens when something breaks, money is lost, access fails or nobody knows who is responsible.

National Security Review

Requirements The regulations prescribe extensive information for national security review and timelines for Ministerial decisions. Applicants must provide information about legal name, trade names, jurisdictions, addresses, contact information, business activities, financial services, affiliates, ownership and control, individuals or entities with significant voting or ownership interests, board members, highly compensated senior officers, major creditors, state owned enterprise ownership or appointment powers, categories of personal or financial information gathered or planned to be gathered, countries where the applicant or third party service providers store or process that information, and individuals or entities outside employees or agents that may receive access to that information. The Minister has 60 days after receiving the application copy to decide whether to review, with extensions in 60 day periods. If a review proceeds, the Minister has 180 days, with 180 day extensions. Applicants have 30 days to request review of a directive to refuse accreditation. Applicants must provide requested additional information within 30 days. For suspension and revocation, participants or ATPSPs have 30 days to request review of a notice of the Minister’s intent to direct revocation. Former participants and former ATPSPs must provide specified information to consumers or participating entities. Additional information requested by the Bank must be provided within 15 days.
  • Ownership, control, affiliates, significant influence and voting or ownership interest information
  • Countries of residence, citizenship, incorporation or formation for relevant individuals and entities
  • Board member and five most highly compensated senior officer information
  • Five largest creditors and credit agreement terms
  • State owned enterprise ownership, voting interest or appointment powers
  • Categories of personal and financial information gathered or planned, including identifying information, financial data, private communications and geolocation data
  • Countries where applicant or third party service providers store or process information
  • Non employee or non agent individuals or entities that may access the information
  • 60 day Ministerial decision window to review, extendable by 60 day periods
  • 180 day national security review period, extendable by 180 day periods
  • 30 day applicant review request period for refusal directive
  • 30 day period to provide additional requested information under subsection 54(2)
  • 30 day review request period for notice of intent to direct revocation
  • 15 day period to provide additional information requested by the Bank under subsection 71(2)
Implementation Applicants should prepare a national security file before applying, not after questions arrive. That file should include ownership charts, control analysis, citizenship and residency information, affiliates, creditors, SOE exposure, data categories, data storage and processing locations, cloud and vendor access, third party access, board and senior officer information, and change monitoring. Deal teams should assess how fundraising, acquisitions, data residency, vendor changes and cross border processing could affect review risk.
Post-Consultation Watch
  • Whether the national security information package is proportionate for lower risk applicants
  • Whether significant influence, creditor exposure and third party access require clearer guidance
  • Whether data residency and cross border processing expectations should be clarified before applications begin
  • Whether the 60 day and 180 day review timelines could materially affect investment, partnership and launch planning
  • Whether applicants should have a pre filing process or informal guidance pathway for complex ownership structures
  • Whether national security review should be harmonized with broader financial infrastructure, digital identity and cloud risk policy
NCFA Perspective This connects open banking to financial infrastructure security. It is not a side process. National security review can affect who enters the market, which investors participate, where data is processed, which vendors are acceptable and how exits are structured. If handled clearly, it can strengthen trust. If handled opaquely, it can slow capital and partnership formation.

Assessments and Fees

Requirements The regulations set an indexed accreditation fee and annual assessments. The accreditation fee is $2,500 in the year the section comes into force. In later years it is calculated as $2,500 multiplied by the ratio of the September all items CPI for Canada in the year before application to the September CPI in the year the section comes into force, rounded to the nearest $100, with no decrease from the previous year. Participating entity assessments are calculated as base assessment plus variable assessment minus interim assessments. Base assessments depend on total asset value. Entities with at least $1 trillion in assets pay a $150,000 base amount; $100 billion to under $1 trillion pay $100,000; $10 billion to under $100 billion pay $50,000; $1 billion to under $10 billion pay $20,000; and under $1 billion pay $10,000. Variable assessment shares allocate remaining Bank costs after deductions by asset tier using 0.4, 0.3, 0.2 and 0.1 factors for the larger asset tiers, while the under $1 billion category has no variable amount. Subsidiary assets are excluded where the subsidiary is itself a participating entity. ATPSPs are assessed $10,000 per year less interim assessments. The external complaints body is assessed $50,000 per year less interim assessments, reduced proportionally for a partial year. Information requested about assets must be provided by March 31 following the relevant calendar year when requested by December 31, or within 15 days for other requests. If asset information is not provided on time, the entity is treated as being in the highest asset category for assessment purposes.
  • $2,500 first year accreditation fee
  • CPI indexed accreditation fee after first year, rounded to nearest $100 and not allowed to decrease
  • Participating entity assessment equals base assessment plus variable assessment minus interim assessment
  • Base assessment tiers of $150,000, $100,000, $50,000, $20,000 and $10,000 based on total assets
  • Variable assessment shares of 0.4, 0.3, 0.2 and 0.1 for larger asset tiers
  • No variable assessment for entities with less than $1 billion in assets
  • ATPSP annual assessment of $10,000 less interim assessments
  • External complaints body annual assessment of $50,000 less interim assessments, prorated for partial year designation
  • Asset information deadline of March 31 in specified cases and 15 days in other cases
  • Failure to provide asset information can result in assessment as if the entity were in the highest asset category
Implementation Participants should model accreditation fees, annual assessment tier, possible variable assessment, interim assessments, ATPSP fees, external complaints body implications, insurance or guarantee costs, technical build, security assurance, reporting systems and compliance staffing. Smaller firms should assess whether direct participation, ATPSP services, partnership or staged entry creates a viable cost structure.
Post-Consultation Watch
  • Whether the base assessment tiers are proportionate for mid sized and smaller participants
  • Whether the zero variable assessment for under $1 billion firms is enough to support competition
  • Whether ATPSP fixed fees support shared infrastructure economics
  • Whether asset based assessment is the right proxy for supervisory cost or market impact
  • Whether fee predictability is sufficient for early entrants and investors
  • Whether the highest tier default for missing asset information is too punitive or necessary for compliance discipline
NCFA Perspective The fee schedule is only one part of participation cost. The strategic issue is total regulatory operating cost. If cost scales poorly, Canada could see a market where participation is open in law but concentrated in practice. Shared infrastructure, clear guidance and proportionate reporting may determine whether smaller innovators can enter.

Administrative Monetary Penalties

Requirements The regulations designate violations for contraventions of a long list of Act provisions, specified regulation provisions, non compliance with compliance agreements and non compliance with Bank directions. The designated Act provisions include obligations related to accreditation, suspension conditions, former entity notices, ATPSP activities, prescribed information, data sharing, use of registry, privacy, security, designated officer, breach reporting, authentication, consent, deletion, notices, liability, complaints, records, technical standards, reporting, Bank information requests and other framework duties. The designated regulation provisions include failure to notify another participating entity of non sharing reasons, data sharing service standards, responsible officer information, specified reporting and notice provisions, record keeping provisions and ATPSP record keeping provisions. The Act provides maximum penalties of up to $1 million for individuals and up to $10 million for participating entities or ATPSPs.
  • Contraventions of numerous Act provisions are designated as violations
  • Contraventions of selected regulation provisions are designated as violations
  • Non compliance with compliance agreements is designated as a violation
  • Non compliance with specified Bank directions is designated as a violation
  • Regulation violations include non sharing notice failures, service standard failures, officer reporting failures, notice failures, annual reporting failures and record keeping failures
  • Maximum penalty of $1 million for individuals
  • Maximum penalty of $10 million for participating entities or ATPSPs
  • Penalty exposure connects to accreditation, data sharing, registry use, privacy, security, breach reporting, authentication, consent, deletion, liability, complaints, technical standards, reporting, records and Bank information requests
  • Coming into force is staged by Act sections, with most regulations coming into force when section 44 of the Act comes into force, data sharing and many operational obligations when section 76 comes into force, and assessment provisions when section 140 comes into force
Implementation Participants should map every designated violation to an internal control, evidence record and accountable owner. Enforcement readiness should cover consent, registry checks, non sharing notices, uptime, breach reporting, annual reporting, records, complaints, officer information, Bank information requests, compliance agreements and directions. Boards and senior leaders should understand which failures create individual or organizational exposure.
Post-Consultation Watch
  • Whether violation categories are clear enough for participants to map controls before launch
  • Whether penalty exposure is proportionate across firms of different size and role
  • Whether remediation and self reporting should affect penalty treatment
  • Whether public enforcement disclosure will be used to strengthen market discipline
  • Whether staged coming into force gives firms enough time to build controls before penalties apply
  • Whether individual exposure could affect senior officer recruitment and governance design
NCFA Perspective Penalty risk is less about the headline maximum and more about whether an organization can prove it had controls, records and remediation processes in place before something went wrong. Enforcement should strengthen trust without chilling responsible innovation. That balance will matter as Canada tries to turn regulatory credibility into market adoption.

Related NCFA Intelligence

Open Banking in Canada Opportunity BriefCommercial opportunity layer connected to this regulatory guide Open the brief
Financial Innovation MapWhere consumer driven banking fits in the broader fintech innovation ecosystem View the map
Research LibrarySupporting reports, market evidence and policy research Research library
Fraud regulatory perspectiveTrust, fraud controls and consumer protection context for Canada’s open banking strategy Read the fraud perspective

From Regulation to Opportunity

Canada’s proposed Consumer Driven Banking Regulations create readiness questions across accreditation, consent, data scope, APIs, cybersecurity, reporting, liability, supervision, national security review and enforcement. NCFA tracks commercial opportunities separately in the Open Banking in Canada Opportunity Brief, where regulatory evidence connects to product opportunities, investment themes, implementation gaps and emerging market signals.

Open the Opportunity Brief


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights

NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Conexus Backs JUDI.AI For Credit Union SME Lending

June 29, 2026 | NCFA Fintech Market Activity | Capital Markets And Funding, SME Finance And Business Banking, Artificial Intelligence And Data, Fintech And Innovation
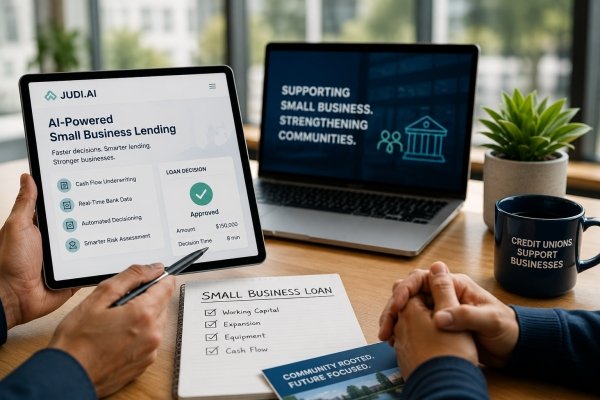
AI Image – Conexus Backs JUDI.AI For Credit Union SME Lending

Credit Union Capital Backs AI Small Business Lending

On June 29, 2026, Conexus Venture Capital invests in JUDI.AI, a Vancouver fintech whose AI cash flow underwriting platform helps credit unions and community banks make faster small business lending decisions. Existing investor Unitus Community Credit Union also participated.

The round size wasn't disclosed, but its a strong transaction. A credit union backed venture fund is financing AI lending infrastructure that already serves credit unions and community banks across Canada and the U.S.

JUDI.AI says its platform has processed more than $2 billion in small business loan applications, supports more than 50 clients, and can reduce the loan application and decisioning process from more than seven days to under ten minutes without collecting financial statements. The platform uses permissioned bank transaction data, a domain specific credit model, and a real time view of cash flow to assess small business borrowers.

Conexus Backs Faster Credit Union Lending

Small business lending has always fit the credit union model in theory. Credit unions know local communities, relationship banking, and member service. The problem is operating cost.

A small business loan can still require bank statements, financial statements, manual review, back and forth questions, policy checks, risk scoring, and approval work. If the process takes too long, borrowers look elsewhere. If the process costs too much, lenders struggle to serve smaller tickets profitably.

JUDI.AI is targeting that gap. The platform combines cash flow analysis, automated underwriting, loan portfolio reporting, and analytics for credit unions and community banks. Instead of relying only on older financial statements or conventional lending metrics, it helps lenders assess live business activity through permissioned transaction data.

That gives credit unions a way to compete on speed without abandoning lending discipline.

Conexus Invests After Using JUDI.AI

Conexus was already familiar with the platform before the venture investment. The announcement says small business members in Saskatchewan previously used JUDI.AI for years to access loans faster, while Conexus reduced the time required to process applications.

That makes the investment more than a financial bet. Conexus is backing a tool it's used inside its own lending workflow, where speed, borrower experience, staff capacity, and credit discipline all matter.

Gord Baizley, CEO of JUDI.AI, framed the business around lending practice:

"At JUDI, we're not just selling a platform. We're championing a methodology. We've learned that success in small business lending is more than just technology, but a holistic approach that blends people, process, technology and intentional growth."

Better SME credit infrastructure is not only about faster models. It also depends on workflow design, risk controls, lender adoption, borrower experience, and portfolio monitoring.

Cash Flow Data For SME Credit

JUDI.AI's model fits a larger fintech pattern. SME finance is increasingly built around current business activity rather than static documents.

That connects directly to Canada's open banking opportunity and NCFA's Open Finance SME Capital Access opportunity work. Read access can support income verification, affordability checks, cash flow insight, fraud signals, onboarding, and SME credit.

For small businesses, the commercial value comes when permissioned financial data helps lenders understand revenue, expense patterns, repayment capacity, seasonality, and account behaviour without weeks of manual collection.

The AI model needs good data, the lender needs clear controls, and the borrower needs a simpler application path. If those pieces work together, small business credit can become faster and more accessible without turning into loose lending.

JUDI.AI's decade of performance data also gives the platform a stronger adoption story than a new AI wrapper. Credit unions are buying a tested underwriting process designed for their borrower base.

Canadian SME Finance Is Getting More Operational

Float's $85 million Series C shows Canadian business finance platforms expanding across payments, cash management, credit, and AI finance workflows.

EQ Bank's Business Card launch adds spending, cashback, interest, and cash flow tools to its SME banking stack.

Better banking options for Canadian SMEs remain a live competition issue as business owners seek lower friction, better credit access, and more useful digital financial tools.

NCFA's Financial Innovation Map tracks SME finance, open finance, AI underwriting, business banking, and financial data infrastructure opportunities.

Can Credit Unions Scale AI Lending Locally?

The Conexus investment shows how credit unions can use venture capital as more than a financial return tool. They can back fintech infrastructure that improves member service, strengthens local business lending, and gives community based institutions a better way to compete with digital lenders.

For JUDI.AI, the next step is continued growth. The platform already supports credit unions and community banks across Canada and the U.S., and the new capital supports North American growth and product development. The strongest path is helping lenders approve strong small business borrowers faster, manage risk with better cash flow data, and keep local credit relationships inside the credit union system.

The competitive question is whether credit unions can adopt fast enough? Fintech lenders, banks, embedded finance platforms, and business finance software firms are all trying to own more of the SME finance relationship. Credit unions have trust and local presence. They now need digital credit infrastructure that matches borrower expectations.

Talking Point

If credit unions can combine local member trust with AI cash flow underwriting, can they become the strongest distribution channel for small business lending in Canada?


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: [www.ncfacanada.org](http://www.ncfacanada.org)

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


How To Optimize Logistics Costs Using Automated Invoice Processing Tools

Jun 29, 2026

AI Image – Automated invoice processing dashboard on a laptop showing invoice validation, payment approval workflow, and logistics cost analytics, with shipping containers and a freight truck in the background.

Despite its importance, billing precision often falters under manual handling. Errors emerge without warning when human input governs invoicing tasks. Financial forecasts shift unpredictably due to late or incorrect payments. Coordination among carriers, brokers, and shippers grows harder with each added layer of complexity. Instead of relying on outdated routines, some firms now allow software to handle incoming documents. Approval timelines shorten once digital systems take over verification steps. Expense tracking improves when data flows continuously through connected platforms.

Financial decisions gain clarity when data comes together, tied directly to shipping operations. With current logistics platforms, automated processes reveal hidden expenses through precise tracking instead of guesswork. Unnecessary payments shrink while oversight grows stronger across spending areas. Invoice handling shifts into alignment with broader efforts to manage costs where margins matter most.

Automated Invoice Processing In Logistics

With the proper use of Invoice handling in logistics shifts when automation takes over. From carrier bills to vendor statements, manual checks become unnecessary. Data pulls automatically, cross-checked with delivery logs for accuracy. Validation happens without human input, cutting down mistakes significantly. Payments go through only when services are confirmed and terms met. Agreement fulfillment decides whether a charge is processed.

It’s important to know and understand that payment cycles shrink when automation takes over, far beyond just cutting errors. Because invoices move faster, carrier relations tend to stay stable. Penalties fade into the background where timing used to fail. With tighter control over outgoing funds, businesses handling large shipping loads find breathing room - even on narrow profit paths.

Cost Factors Touched by Automation

Among key factors shaping expenses in freight operations, mismatches in invoicing stand out - often tied to wrong pricing, repeated charges, or absent shipping details. When digital tools compare submitted bills with agreed terms and proof of delivery, problems surface sooner. Payments stay accurate because checks happen before funds move. Consistency in accounting data improves when all units refer to the same verified outcomes.

Administrative effort contributes significantly to overall expense. Handling invoices by hand takes hours from both accounting and logistics personnel, raising daily operating costs. With delivery management software, the burden lessens so employees can shift attention toward activities like reviewing supplier terms or assessing efficiency trends. Integrated with tools managing deliveries, companies achieve clearer visibility into shipments - this clarity streamlines how invoices are verified.

Connecting To Shipping Networks

When we look at links towards wider logistics networks, automated invoicing gains capability. Through integration with transport management setups, firms match charge records to current delivery movements. A cohesive picture of supply chain actions emerges - precision strengthens alongside fiscal clarity.

Because route optimization software connects to billing records, firms gain clearer insight into transport spending. Where delivery timing meets invoice data, hidden waste often appears. Fuel reports that match up with dispatch logs reveal gaps in efficiency. Through consistent system links, pricing forecasts grow more reliable. Unexpected charges drop when navigation choices reflect financial tracking.

Conclusion

To lower logistics expenses, focus must shift beyond rate negotiations alone. Through precise financial oversight, operational waste declines notably. Visibility into transport expenditures, when immediate, supports informed choices. With automation handling invoices, errors decrease while efficiency rises. Manual tasks shrink as systems enforce tighter budget adherence. Stronger controls emerge across logistical operations naturally. Cost management improves without added complexity.

With growth in logistics networks comes greater reliance on data, making automation essential to cost control. Where firms implement unified platforms alongside wider technological tools, improvements emerge across accuracy and sustained output. Financial discipline follows when processes evolve beyond manual handling into coordinated digital workflows.


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Canada’s Open Banking Strategy Starts With Trust

June 29, 2026 | NCFA Feature | Open Banking And Open Finance, Digital Identity And Trust, Cybersecurity And Fraud, Risk Compliance And Regtech, Fintech And Innovation

AI Image – Canada’s Consumer Driven Banking framework showing a secure digital trust layer

Fraud, Consent And Liability Before Open Finance Scale

On June 26, 2026, the Government of Canada published Consumer Driven Banking regulations together with new fraud prevention regulations, the most significant progress in Canada's open banking implementation since legislation received Royal Assent earlier this year.

At first glance, the two regulatory packages appear separate. One establishes the operating rules for consumer driven banking. The other requires federally regulated banks to strengthen fraud prevention for electronic funds transfers.

Together, however, they reveal something much bigger.

Canada isn't simply launching open banking. It's building the trust infrastructure needed before open finance can scale.

The problem is that millions of Canadians already share their financial information through screen scraping, a practice tracked as a core open banking risk in Bank Of Canada Signals Open Banking Timing Risk. Finance Canada estimates roughly nine million Canadians currently use screen scraping despite the security, liability, and consumer protection concerns it creates. The new framework is designed to replace that model with accredited participants, standardized APIs, consumer controlled consent, and clear accountability.

The Regulations Explain Canada's Strategy

Much of the early discussion around open banking has focused on data portability. The regulations suggest Finance Canada sees the challenge differently.

Data sharing is only one part of the system.

  • Consumers must know who can access their information
  • Financial institutions must know who they are sharing data with
  • Accredited participants must meet common operational and security requirements
  • Liability must be clear when something goes wrong
  • Fraud must be monitored
  • Technical standards must allow systems to communicate securely
  • Consumers need complaint mechanisms and regulatory oversight

Only after these pieces exist does secure data sharing become practical.

The Regulatory Impact Analysis estimates the framework will generate approximately $13.2 billion in net benefits over ten years, compared with implementation costs of about $457.7 million, largely through greater competition, improved consumer choice, reduced friction, and innovation.

Those numbers reinforce that Consumer Driven Banking is being treated as national financial infrastructure rather than another fintech initiative.

Why Fraud Rules Arrived At The Same Time

Some viewed the fraud regulations as a separate announcement, but the timing suggests otherwise.

As consumers gain greater control over financial data and eventually broader payment functionality, fraud risks also change. Criminals increasingly exploit social engineering, account takeover, impersonation, and authorized push payment scams rather than technical weaknesses alone.

Finance Canada's fraud framework responds by requiring federally regulated banks to establish policies and procedures to detect, prevent, and mitigate consumer targeted fraud involving electronic funds transfers.

The regulations also introduce stronger expectations around consumer controls, including the ability to manage transaction capabilities and limits, express consent before enabling electronic funds transfer functionality, and fraud reporting to the Financial Consumer Agency of Canada.

Greater consumer control must be matched by stronger consumer protection.  The inherent message is that the federal government wants to make fraud prevention part of the architecture rather than an afterthought.

Canada Is Turning Trust Into Rules

Reading the regulations together shows that trust is no longer treated as a policy objective. It's becoming operational and the framework combines:

  • consumer controlled consent
  • accreditation of participating organizations
  • secure API based data exchange
  • authentication requirements
  • defined liability arrangements
  • technical standards
  • record keeping obligations
  • ongoing supervision
  • consumer complaint processes
  • fraud monitoring and reporting

None of those capabilities creates value on its own, but collectively they create an environment where consumers, banks, fintechs, and regulators can exchange financial information with greater confidence than today's screen scraping model.

The regulations therefore answer an important implementation question that has existed since Canada's open banking discussions began several years ago.

Trust is not assumed. It's engineered.

Every Regulatory Requirement Creates A Product Opportunity

The regulations also strengthen several areas already appearing across NCFA's Financial Innovation Map.

Consumer consent requirements create opportunities for consent orchestration platforms that help consumers understand, grant, renew, and withdraw permissions across multiple financial relationships.

Accreditation requirements create opportunities for compliance operations platforms that help fintech companies prepare for accreditation, maintain operational controls, manage evidence, and demonstrate ongoing compliance.

Fraud obligations strengthen demand for behavioural fraud analytics, scam detection, mule account monitoring, transaction risk scoring, and real time payment controls.

Authentication requirements reinforce opportunities for digital identity, credential management, and secure customer authentication.

Technical standards create demand for API testing, interoperability tools, certification services, and developer infrastructure.

Liability and complaint provisions strengthen opportunities for workflow automation covering dispute management, evidence collection, case handling, and regulatory reporting.

None of these businesses exists because regulators explicitly created them, but they will emerge because every operational requirement creates work that financial institutions and technology providers must perform efficiently.  And that's often where durable fintech companies are built.

Canada Is Building Beyond Read Only Banking

The initial Consumer Driven Banking framework focuses on secure consumer permissioned data sharing. It's an intentional starting point.

Once accreditation, liability, consent management, authentication, and technical standards mature, the same infrastructure can support broader open finance capabilities, including additional financial products and, potentially, future write access.

The regulations therefore describe more than the first phase of open banking. They establish the operating foundation for future financial data ecosystems.

The opportunity is not limited to data sharing. It extends into the systems that make data sharing safe, usable, auditable, and commercially scalable.

That includes trust infrastructure, fraud infrastructure, consent systems, API reliability, compliance operations, data governance, and consumer protection workflows.

See: Canada Open Banking Commercialization Roadmap

The next phase of Canada's open banking market will depend on whether these operating layers mature quickly enough for banks, fintechs, consumers, and businesses to use the framework with confidence.

That makes today's implementation decisions highly important because many of tomorrow's fintech products will inherit the rules established now.

For Canada's fintech ecosystem, this strengthens the opportunity case outlined in NCFA's Open Banking Opportunity Brief.  The next iteration of value will come from tools that make consent, risk, identity, fraud controls, interoperability, and compliance easier to operate at scale.

Talking Point

If trust, consent, fraud controls, liability, and interoperability become core infrastructure for open banking, which product category will create the greatest competitive advantage for Canadian fintech companies over the next five years?


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Financial Planning After Major Life Changes: A Complete Guide

Jun 29, 2026

Major life events can reshape your financial future in unexpected ways. Whether you get married, change careers, welcome a child, or navigate a divorce, each milestone brings new financial responsibilities.

Financial planning after major life changes helps you adapt with confidence, protect your assets, and maintain long-term stability. By reviewing your finances and adjusting your strategy as your circumstances evolve, you can make informed decisions that support both your current needs and future goals. Continue reading to learn more.

Build a Strong Financial Foundation

Every financial transition begins with a clear understanding of your current financial situation. Review your monthly income, expenses, savings, and outstanding debts before making any major decisions. If your income changes, update your budget immediately instead of relying on outdated spending habits. A realistic budget helps you manage daily expenses while staying focused on long-term objectives.

An emergency fund also plays a critical role during periods of change. Aim to save enough to cover several months of essential living expenses, giving yourself a financial cushion if unexpected costs arise. You should also review your insurance coverage, retirement contributions, and investment portfolio to ensure they continue to match your financial goals and risk tolerance.

Adjust Your Finances After Family Changes

Family milestones often require significant financial adjustments. If you get married, discuss budgeting, debt, savings goals, and financial responsibilities before combining accounts. Open communication helps couples avoid misunderstandings and establish shared financial priorities from the beginning.

Parenthood introduces additional expenses, making it important to increase emergency savings, review life insurance, and start planning for future education costs. Divorce, on the other hand, requires careful financial planning to protect your long-term stability.

Separate joint bank accounts, update beneficiary designations, create a realistic post-divorce budget, and review how retirement accounts or shared assets will be divided. A divorce lawyer can help manage all of this. Taking these steps early can reduce financial stress and make the transition more manageable.

Prepare for Career and Income Changes

A new job, promotion, career change, or business venture can strengthen your financial future when you plan wisely. Whenever your employment changes, review your salary, workplace benefits, retirement plans, and tax obligations. Understanding these changes helps you maximize your income while avoiding costly financial mistakes.

Although higher earnings create new opportunities, resist the urge to increase your spending immediately. Instead, use additional income to build savings, invest for retirement, or pay down high-interest debt. If you experience a temporary loss of income, focus on essential expenses, reduce discretionary spending, and rely on your emergency fund while developing a plan to regain financial stability.

Review Your Financial Plan Regularly

Financial planning should evolve alongside your life. Schedule regular reviews to ensure your financial strategy still reflects your goals, responsibilities, and changing circumstances. Update your will, insurance policies, beneficiary designations, and estate planning documents after every major life event. Monitoring your credit report and evaluating your investment performance can also help you identify problems before they become significant setbacks.

See:  Why You Should Never Invest Your Emergency Fund

Annual financial reviews give you the opportunity to adjust your budget, strengthen your savings strategy, and prepare for future milestones. Small adjustments made consistently often have a greater long-term impact than major changes made only during financial emergencies.

Endnote

Financial planning after major life changes allows you to approach life's biggest transitions with greater confidence. Whether you experience marriage, divorce, career changes, parenthood, or retirement, thoughtful financial decisions can reduce uncertainty and protect your long-term well-being. By reviewing your budget, updating important documents, and adjusting your financial strategy regularly, you create a flexible plan that grows with you and supports lasting financial security through every stage of life.


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter