Category Archives: Tech, Tools, Productivity

Navigating Major Traffic Allegations: Defending Against Careless Driving Charges

July 1, 2026

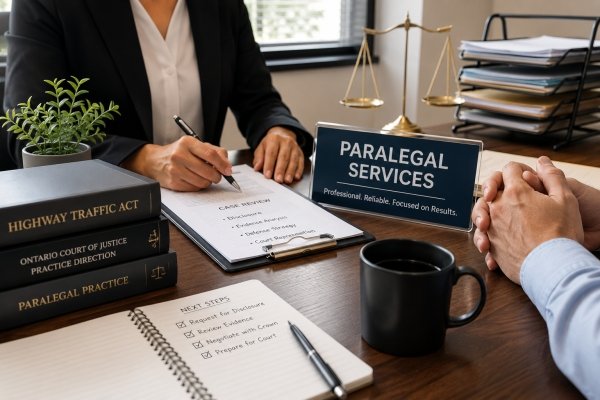
AI Image – Paralegal services, carless driving charges

Under the Ontario Highway Traffic Act, a charge of careless driving is one of the most serious non-criminal offences a driver can face. Law enforcement officers often issue this ticket following motor vehicle accidents, alleging that a motorist drove without proper care and attention or without reasonable consideration for others on the road. Because this charge is broad and relies heavily on the officer's personal opinion, it carries severe penalties, including six demerit points, a six-month license suspension, massive financial fines, and even potential jail time. Defending against this allegation requires an aggressive and precise legal strategy.

The Serious Impact of a Careless Driving Conviction

A conviction for careless driving goes far beyond a simple traffic ticket; it is treated as a major offence by insurance companies, similar to a criminal impaired driving conviction.

Upon a formal conviction, the Ministry of Transportation immediately applies six demerit points to your driving record, which triggers a mandatory interview for fully licensed drivers and can lead to an automatic suspension for novice drivers. Furthermore, the court can issue discretionary fines ranging from hundreds to thousands of dollars and suspend your driving privileges for up to two years. For many everyday drivers, the sudden jump in insurance costs or a total policy cancellation makes keeping a vehicle impossible, threatening their employment and daily lives.

Building a Strong Legal Defence

To secure a conviction, the prosecution must prove that your driving fell well below the standard of a reasonably prudent driver. Simply being involved in an accident is not legal proof of careless driving.

The defence team at Traffic Paralegal Services carefully analyses every element of the crown's case. They review accident reconstruction data, interview independent witnesses, and check road conditions, weather data, and mechanical factors. A successful defence often centres on proving that the incident was a simple error in judgment or an unavoidable accident caused by sudden environmental changes, rather than a reckless disregard for public safety.

Protecting Your Future with Professional Advocacy

The stakes are incredibly high in careless driving cases, meaning you should never enter a courtroom without experienced legal representation. Prosecutors often push for severe penalties, making professional guidance essential for a fair trial.

The court specialists at Traffic Paralegal Services bring extensive experience to these complex cases. They handle all discussions with the crown prosecutor, looking for opportunities to get the charges completely dropped due to insufficient evidence or technical errors. If a full withdrawal is not possible, they work to reduce the charge to a minor, low-point infraction like "follow too closely," saving you from a high-risk insurance status and protecting your freedom to drive.

Conclusion

Defending against a major traffic allegation requires immediate legal action, an independent investigation, and skilled courtroom advocacy. By actively fighting careless driving tickets in ontario, you protect your freedom, avoid severe financial penalties, and keep your insurance affordable. Accepting a careless driving conviction without a fight can negatively impact your life and career for years to come. Invest in your future by placing your case in the hands of proven traffic law experts. Partnering with a trusted, experienced firm like Traffic Paralegal Services ensures your defence is built correctly, giving you the best opportunity to secure a successful outcome in court.

“In 2026, trust has become the deciding factor for people fighting traffic charges in Ontario - especially as we hear more clients describe being let down by representatives who operate without structure or accountability. Too often, the story is the same: a meeting arranged at a coffee shop, a quick promise that the matter is “handled,” and then silence - missed updates, unanswered calls, and no meaningful steps taken toward resolution. That experience does more than waste time; it increases stress and can put a client’s case at risk.

See:  The Reasons to Choose Ukrainian Credit Union in Toronto

At Traffic Paralegal Services, we build trust through a formal intake process, clear written next steps, consistent communication, and file management that does not depend on one-off meetings or vague assurances. Clients know where their matter stands, what is happening next, and who is responsible at every stage - from request for disclosure to negotiations and court attendance. Reliability is not a marketing line; it is the foundation of how we serve our clients.”

Volodymyr Menok, President, Traffic Paralegal Services

Director, Traffic Paralegal Services


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


UK Cryptoasset Regulation Guide And Resources

June 29, 2026 | NCFA Resource | Digital Assets Blockchain And Tokenization, Regulation And Policy

UK cryptoasset regulation guide covering FCA authorisation, stablecoins, custody, market abuse and compliance

UK Cryptoasset Regulation Guide And Resources

NCFA has published a practical guide to the UK cryptoasset regulations and FCA final rules. It helps firms, platforms, issuers, custodians, compliance teams, investors and policymakers understand how the UK framework applies across regulated digital asset activities.

The primary Regulatory Intelligence guide organizes the rule package by authorisation, scope, stablecoin issuance, custody, trading platforms, disclosures, market abuse, prudential requirements, Consumer Duty, governance, operational resilience, financial crime, reporting and implementation readiness.

What The Guide Covers

The resource gives readers a structured entry point into the UK cryptoasset regime without treating the rulebook as one long regulatory document. It directs readers to the detailed Regulatory Intelligence explorer, where each rule area separates requirements, implementation work, consultation outcomes and NCFA analysis.

That distinction is important because firms need to prepare for more than registration. They may need to assess permissions, governance, safeguarding, disclosures, capital, operational controls, market integrity, customer communications, reporting and senior management accountability.

The framework also gives Canadian and global readers a useful comparison point as tokenized financial infrastructure, stablecoins and regulated digital asset markets develop. The central question is which firms can meet regulated market standards while continuing to build useful products and services.

Who Should Use It

This resource is designed for crypto trading platforms, custodians, stablecoin issuers, digital asset infrastructure firms, fintech founders, compliance teams, securities lawyers, investors, policymakers and market participants comparing global crypto regulatory models.

It is especially relevant for organizations assessing FCA authorisation, custody controls, stablecoin infrastructure, consumer disclosures, market abuse controls, governance, prudential requirements and operational readiness.

Why It Is Useful

The strength of the resource is its practical structure. It turns a large regulatory package into a clear intelligence layer that readers can use to identify obligations, implementation dependencies and areas requiring specialist legal, compliance, technology or operational work.

It also supports jurisdictional comparison. Canadian and global market participants can use the UK rules to compare approaches to crypto authorisation, custody, stablecoins, disclosures, platform conduct, market integrity and consumer protection.

The guide is not a substitute for legal advice. Regulatory treatment depends on the facts, firm structure, permissions, product design and activities performed in or into the UK. Readers should use it for ecosystem intelligence and planning, then review the FCA primary materials and consult qualified advisers.

Key Resources

UK Cryptoasset Regulations And FCA Final Rules
Primary NCFA Regulatory Intelligence guide with the full rule explorer, implementation analysis, timeline and source links.

Tokenization Starts Looking Like Financial Infrastructure
Market infrastructure context for tokenized cash, custody, settlement and regulated digital asset rails.

Deloitte And Stablecorp Bring QCAD To Banks
Canadian stablecoin infrastructure context for banks and regulated financial institutions.

FCA Final Crypto Rules Announcement
Official FCA source announcing the final UK cryptoasset rule package.


NCFA Canada

The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer to peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


UK Cryptoasset Regulations And FCA Final Rules

NCFA Regulatory Intelligence - UK FCA Final Cryptoasset Rules
NCFA Canada | Regulatory Intelligence | Digital Assets, Cryptoassets and Blockchain | Last updated July 19, 2026 | Status final FCA rules
NCFA Regulatory Intelligence
This guide explains UK cryptoasset regulations and the FCA final rules for authorisation, market access, implementation, compliance and opportunity analysis. Sources include FCA policy statements PS26/9 to PS26/13, finalised guidance FG26/5 to FG26/7 and the aggregate cost benefit analysis.
FCA Cryptoasset Regime Final rules for UK regulated cryptoasset activities

UK Cryptoasset Regulations And FCA Final Rules

The FCA published its final cryptoasset rules and guidance on 30 June 2026. The application period runs from 30 September 2026 to 28 February 2027, and the new regime starts on 25 October 2027. Use this guide to understand what the final rules require, what firms need to build, how the consultation outcome changed the design and where regulation creates market opportunities. Coverage includes admissions, disclosures, market abuse, stablecoin issuance, trading platforms, intermediaries, lending, borrowing, staking, safeguarding and custody, prudential requirements, Consumer Duty, governance, operational resilience, financial crime, reporting, redress, international firms and DeFi.

What Are The UK Cryptoasset Regulations?

The UK cryptoasset regulations bring specified cryptoasset activities into Financial Conduct Authority supervision under the Financial Services and Markets Act. The FCA final rules cover authorisation, trading platforms, intermediaries, stablecoin issuance, custody, lending, staking, disclosures, market abuse, prudential requirements, Consumer Duty, governance and operational resilience. The regime starts on 25 October 2027.

Final Rules Published30 June 2026
Applications Open30 September 2026
Application Deadline28 February 2027
Regime Starts25 October 2027
RegulatorFinancial Conduct Authority
Existing RegistrationMLR registration does not automatically convert to FSMA authorisation

UK Cryptoasset Regulation Journey

The UK has completed perimeter design, consultation and final FCA rulemaking. Firms now have an implementation period to prepare authorisation, governance, capital, custody, trading, stablecoin, market abuse and conduct systems before the regime starts.
Policy and consultation
Final rules and buildout
Implementation and supervision
Perimeter2023 to 2024 Cryptoasset activities brought into scope
Consultations2025 to 2026 CP25 and CP26 industry feedback
Final Rules30 June 2026 PS26/9 to PS26/13
Applications And Buildout30 Sep 2026 to 28 Feb 2027 Authorisation and systems preparation
Regime Starts25 October 2027 Handbook instruments commence
Supervision2027 onward Market conduct and resilience

Impact Analysis

Selected figures from the FCA aggregate cost benefit analysis and policy statements.
8%UK adults with cryptoasset holdings in 2025
£2,250Estimated average UK consumer crypto holding
£1.315BEstimated quantified firm costs over 10 years
£735MEstimated value of improved regulatory protections
£25MExample trading platform 10 year PV costs
£10MExample FSMA custodian entering crypto custody
£8MExample stablecoin issuer 10 year PV costs
£285MEstimated prudential requirement PV costs

What Firms Should Do Now

Firms that carry out or plan to carry out regulated cryptoasset activities should prepare their authorisation and implementation evidence before the application deadline.

  1. Map every UK activity against the regulated activity perimeter and identify any exclusions or special treatment.
  2. Determine whether the firm needs a new FCA authorisation or a variation of permission.
  3. Prepare a complete application for the period from 30 September 2026 to 28 February 2027 and apply as early as practical.
  4. Assign accountable owners across CRYPTO, CASS, CRYPTOPRU, Consumer Duty, SYSC, SM&CR, financial crime and reporting.
  5. Build evidence for governance, financial resources, custody, resilience, outsourcing, consumer outcomes and operational controls.
  6. Test systems and remediation plans before the regime starts on 25 October 2027.

Regulatory Intelligence Explorer

Navigate the FCA final cryptoasset regime by rule area. Each section separates requirements, implementation work, consultation outcome and NCFA’s strategic perspective.

Overview

Requirements The FCA package creates a full UK cryptoasset regime rather than a single rule. It combines designated activity rules for admissions and market abuse, regulated activity rules for trading platforms, intermediaries, lending, borrowing, staking and safeguarding, stablecoin issuance rules, prudential requirements and cross cutting FCA Handbook standards. The Handbook instruments commence on 25 October 2027.
  • The regime covers UK qualifying cryptoasset trading platforms, cryptoasset intermediaries, qualifying stablecoin issuers, custodians, lending and borrowing services, staking services and firms carrying on regulated cryptoasset activities in or into the UK
  • The final package includes CRYPTO sourcebook rules, CASS 16 for stablecoin backing assets, CASS 17 for safeguarding qualifying cryptoassets, CRYPTOPRU and COREPRU prudential rules, Consumer Duty, COBS, SYSC, SM&CR, DISP, FOS access, reporting and operational resilience requirements
  • The commencement sequence includes stablecoins, admissions, market abuse, intermediaries, trading platforms, lending, borrowing and staking, safeguarding, client asset consequentials, conduct and firm standards, and prudential instruments
  • The FCA kept the broad policy architecture but made targeted changes for proportionality, including stablecoin backing asset simplification, best execution clarification, removal of principal dealers from pre trade transparency, and operational resilience guidance
Implementation Firms should build a regime map by activity, not by document title. A single firm may need authorisation, admissions controls, disclosures, surveillance, custody arrangements, CASS controls, prudential calculations, Consumer Duty evidence, financial crime controls, operational resilience testing and regulatory reporting. The implementation plan should assign accountable owners for each CRYPTO, CASS, SYSC, COBS, SM&CR, DISP and CRYPTOPRU dependency.
Consultation Outcome
  • The FCA moved from consultation to final rules while preserving the regime design
  • Respondents generally supported a comprehensive regime, but pushed for proportionality, international competitiveness and operational clarity
  • The FCA responded with targeted refinements rather than a lighter perimeter
  • Remaining open items include further guidance on DeFi decentralisation and separate DLT operational resilience guidance
NCFA Perspective This is a regulatory market structure event. The UK is setting a supervised operating model for crypto as financial infrastructure. The strategic question is which firms can turn authorisation, custody, stablecoin operations, market surveillance, prudential analytics and conduct evidence into repeatable operating capability before the regime goes live.

Scope and Authorisation

Requirements The regime applies to regulated cryptoasset activities brought into scope by the Financial Services and Markets Act 2000 (Cryptoassets) Regulations 2026 and implemented through FCA Handbook instruments. Activities include operating a qualifying cryptoasset trading platform, dealing, arranging, qualifying cryptoasset lending and borrowing, staking, safeguarding and qualifying stablecoin issuance. Firms conducting those activities will need FCA authorisation unless an exclusion or specific treatment applies.
  • UK QCATP operators require authorisation where they operate in the UK or serve UK consumers from overseas
  • International firms are assessed against threshold conditions including location of offices, effective supervision, appropriate resources, suitability and business model
  • Dual regulated firms may operate in the UK through a branch where the PRA is satisfied threshold conditions and ongoing requirements are met
  • The FCA expects an authorisation gateway before the regime goes live, with firms preparing systems, controls and evidence in advance
  • Existing cryptoasset MLR registration does not replace FSMA authorisation for regulated cryptoasset activities
Implementation Firms should map every UK facing activity to the regulated activity perimeter and authorisation pathway. The implementation file should include corporate structure, UK presence, branch or subsidiary analysis, overseas service model, governance, financial resources, systems and controls, operational resilience, outsourcing, financial crime and Consumer Duty evidence.
Consultation Outcome
  • The FCA clarified its approach to international firms and branches following feedback
  • The final approach remains cautious about cross border firms serving UK consumers without clear UK accountability
  • The FCA did not create a broad equivalence shortcut in the final package
  • The authorisation runway becomes a key commercial dependency for firms seeking UK market access
NCFA Perspective Scope is the competitive gate. The UK is giving global crypto firms a route into a regulated market, but the route depends on authorisation evidence, supervision, governance and operational substance. That is different from simply allowing offshore activity to reach UK users.

Admissions and Disclosures

Requirements The admissions and disclosure framework governs admission of qualifying cryptoassets to trading on UK QCATPs and offers to the public of qualifying cryptoassets admitted to trading. It uses qualifying cryptoasset disclosure documents, admission criteria, due diligence, responsibility allocation and disclosure obligations to create a baseline for market entry.
  • UK QCATP operators must establish admission criteria and assess whether a qualifying cryptoasset should be admitted to trading
  • Offerors and relevant issuers must produce qualifying cryptoasset disclosure documents where required
  • Disclosure documents must support informed decisions and include material information about the cryptoasset, rights, risks, technology, governance and project context
  • Trading platforms need procedures for disclosure review, admission decisions, record keeping and ongoing monitoring
  • Relevant issuers and offerors face responsibility for statements and omissions in disclosure documents
  • Protected forward looking statements have specific treatment under the regime
  • Firms must manage the link between admissions, disclosures, market abuse controls and post admission monitoring
Implementation Implementation requires an admissions committee or equivalent control function, written admission criteria, due diligence checklists, disclosure templates, issuer and offeror attestations, legal review, technology risk review, conflict checks, decision records and post admission triggers. Platforms should prepare a repository for disclosure documents, versions, approvals, rejection reasons and ongoing updates.
Consultation Outcome
  • The FCA retained the admissions and disclosure framework after consultation
  • The final rules are designed to support market integrity without importing traditional securities listing rules wholesale
  • Firms will need to show how disclosures are complete, fair and understandable for the relevant market
  • The burden falls heavily on platforms because admission decisions become a regulated control point
NCFA Perspective Admissions are where market access becomes a regulated quality filter. The practical opportunity is not only listing more tokens. It is building repeatable disclosure, due diligence, legal review and issuer data infrastructure that can support credible cryptoasset markets.

Market Abuse

Requirements The market abuse regime addresses insider dealing, unlawful disclosure of inside information and market manipulation in qualifying cryptoassets and related instruments. The FCA rules and guidance set out concepts, prohibited behaviours and systems requirements for UK QCATP operators and cryptoasset intermediaries.
  • CRYPTO 4 provides guidance on inside information, insider dealing, unlawful disclosure and market manipulation
  • UK QCATP operators and cryptoasset intermediaries must prevent, detect and disrupt cryptoasset market abuse
  • Operators need systems and procedures for monitoring orders, transactions, communications, suspicious behaviour and abusive patterns
  • Firms must receive and store notifications securely with completeness, integrity and confidentiality
  • Market abuse arrangements must address crypto specific risks such as cross venue trading, on chain activity, token issuance events, concentrated holdings and information asymmetry
  • Outsourcing or delegation does not remove responsibility for compliance
  • Firms need records that can support investigation, escalation and regulator engagement
Implementation Firms should build surveillance scenarios for insider dealing, pump and dump activity, spoofing, wash trading, manipulation around token admissions, misuse of issuer information, coordinated social activity and suspicious on chain transfers. Platforms should integrate order book data, trade data, wallet data where available, issuer announcements, disclosure documents and escalation logs.
Consultation Outcome
  • The final package applies a market abuse model tailored to cryptoasset markets while drawing on familiar FCA concepts
  • The FCA expects trading venues and intermediaries to operate proactive controls rather than relying only on post event enforcement
  • Secure notification and evidence handling are explicit operational requirements
  • The regime creates a compliance technology need across surveillance, data integrity and case management
NCFA Perspective Market abuse is the credibility test for regulated crypto trading. The UK framework will only support institutional adoption if market surveillance, disclosure timing and manipulation controls are strong enough to distinguish regulated markets from speculative venues.

Stablecoin Issuance

Requirements PS26/10 sets final rules for non systemic UK issued qualifying stablecoins, covering issuance, backing assets, redemption, safeguarding and disclosures. CASS 16 governs management and safeguarding of backing asset pools. The FCA’s approach treats stablecoins as money like instruments where trust depends on backing, segregation, redemption, reconciliation and clear disclosures.
  • Issuers must maintain a backing asset pool for each qualifying stablecoin product and segregate it from the firm’s own assets and from other backing pools
  • Backing pools must be held in backing funds accounts or backing assets accounts meeting CASS conditions
  • Issuers using expanded backing assets must calculate the backing asset composition requirement every redemption day
  • The core backing asset requirement is the higher of 5% and the highest redemption percentage over the previous 180 redemption days or shorter operating history
  • Issuers must promptly notify the FCA if they cease to comply with specified backing asset requirements, with a limited exception for rebalancing after a daily calculation
  • Backing assets are held on statutory trust for holders of the qualifying stablecoin
  • Backing asset pools for different stablecoin products must be separate, distinct, independently managed and held in different accounts
  • Stablecoin funds must be promptly paid into a backing funds account or invested in assets held in a backing assets account
  • Issuers must conduct internal and external safeguarding reconciliations, identify and resolve discrepancies and maintain records
  • Redemption requirements include T+1 expectations, with KYC checks completed before the redemption period begins
  • Issuers must provide disclosures and make holders aware of withdrawal rights
  • The FCA allows limited intragroup custody subject to safeguards and allows a 5% excess in the backing asset pool
Implementation Stablecoin issuers need a dedicated operating model for backing assets, liquidity, reconciliation, redemption, disclosures, trust accounting, custodian oversight and holder communications. Implementation should include product level backing pool ledgers, daily BACR calculations where expanded assets are used, reconciliation workflows, FCA notification triggers, redemption queue logic, KYC timing controls, disclosure history and governance over tokenized versions of backing assets.
Consultation Outcome
  • The FCA simplified the backing asset composition requirement after feedback that forward looking redemption estimates were complex and burdensome
  • The FCA kept the range of permissible backing assets and rejected broader LVNAV and non UK UCITS MMF expansion because of stability concerns
  • Tokenized versions of permissible backing assets are not prohibited if they comply with CASS 16 and custody requirements
  • Redemption timelines were adjusted so KYC checks are completed before the redemption period begins
  • The FCA confirmed statutory trust arrangements and made refinements to third party and intragroup custody treatment
NCFA Perspective Stablecoin issuance is where compliance becomes product architecture. The winners will not be the firms that simply issue tokens. They will be the firms that can evidence backing, redemption, liquidity, disclosure and custody controls well enough for consumers, institutions and regulators to treat stablecoins as usable financial infrastructure.

Trading Platforms

Requirements PS26/11 sets rules for UK qualifying cryptoasset trading platforms. The framework covers location and authorisation, platform access, operating rules, conflicts, settlement arrangements, transparency, record keeping and reporting. The FCA expects platforms serving UK consumers to operate through an authorised UK model or an acceptable international firm structure.
  • UK QCATP operators require FCA authorisation if operating in the UK or serving UK consumers from overseas
  • Platforms must have operating rules, admission processes, access standards and controls for orderly trading
  • Retail customer focused requirements apply where platforms serve retail clients
  • Platforms must manage conflicts of interest, including risks around affiliated activities, proprietary activity, token admissions and market data
  • Settlement arrangements must be clear, reliable and consistent with safeguarding and operational resilience requirements
  • Transparency, record keeping and reporting obligations apply to orders, transactions and platform operation
  • Best execution expectations interact with authorised execution venues and periodic post trade analysis
  • Principal dealers were removed from pre trade transparency requirements in the final approach
  • Platforms need market abuse prevention, detection and disruption arrangements under PS26/9
Implementation Platform implementation should include authorisation planning, operating rulebook, access policy, admission governance, conflicts register, surveillance tooling, settlement design, order and trade records, client reporting, market data controls, resilience mapping and incident response. Firms should evidence why venue access, matching, settlement, custody and conflict controls protect consumers and market integrity.
Consultation Outcome
  • The FCA clarified location, incorporation and international firm expectations after feedback
  • Principal dealers were removed from pre trade transparency requirements
  • Best execution was clarified so firms should check prices from at least three reliable UK authorised execution venues where possible but do not need mechanical transaction by transaction checks or execution on those venues
  • The FCA retained the broader platform framework and added guidance rather than reducing the venue perimeter
NCFA Perspective Trading platforms are the centre of the regulated market. The commercial question is whether UK authorised venues can offer credible liquidity, transparent execution and institutional controls without losing users to offshore platforms that do not meet the same standard.

Intermediaries

Requirements The intermediary rules cover firms dealing in qualifying cryptoassets as principal, arranging deals and providing related intermediation services. They connect execution quality, client communication, conflicts, payments for order flow, authorised venue interaction, conduct obligations and prudential requirements.
  • Intermediaries must understand which regulated activity they perform and whether they deal, arrange, route, introduce or support client execution
  • Execution arrangements must be effective and supported by periodic post trade analysis
  • Firms should check prices from at least three reliable UK authorised execution venues where possible
  • The FCA clarified that firms are not required to execute on those venues or perform mechanical transaction by transaction checks if effective arrangements are in place
  • Conflicts, remuneration, inducements and payments for order flow require controls
  • Client communications and conduct obligations apply through COBS and Consumer Duty where relevant
  • Intermediaries may be subject to prudential requirements, financial crime controls, operational resilience and reporting
Implementation Intermediaries should build an execution policy, venue assessment framework, periodic price review, conflicts assessment, client disclosure process, order routing records, remuneration review and evidence that client outcomes are monitored. Firms with global routing models need controls showing how UK clients receive fair treatment under the UK regime.
Consultation Outcome
  • The FCA responded to feedback by clarifying best execution rather than imposing venue execution mandates
  • The final rules seek to balance execution quality with the reality of fragmented global crypto liquidity
  • Concerns about the arranging perimeter and international firms were addressed through guidance and refinements
  • Intermediaries remain a high implementation burden because conduct, execution, financial crime and prudential requirements overlap
NCFA Perspective Intermediation is where user experience meets regulatory discipline. Firms that can route orders well, evidence execution quality and manage conflicts may turn compliance into trust. Firms that treat execution as a black box will struggle under the new model.

Lending and Borrowing

Requirements The lending and borrowing chapter applies to authorised cryptoasset firms providing qualifying cryptoasset lending or borrowing services to retail clients who are not overseas retail clients, with certain requirements also applying to clients who are not overseas clients. Firms remain responsible where they comply through third parties such as custodians or service providers.
  • Firms must provide retail clients with information about the firm and the qualifying cryptoasset lending or borrowing service before the client is bound or before service provision
  • Information must be provided in a durable medium or through a qualifying website, mobile application or digital medium
  • Where clients give express prior consent for yield to be used in further lending, firms may not need to repeat the information requirement for that yield use
  • Retail protections apply to lending and borrowing service design, client information and risk communication
  • Firms remain responsible for compliance when using third party custodians or service providers
  • Rules and controls must address collateral, yield, client reporting, service risk, counterparty risk and return of assets
  • Lending and borrowing firms will also need prudential, safeguarding, operational resilience, financial crime and Consumer Duty evidence
Implementation Implementation should include client information templates, durable medium controls, express consent capture, yield treatment logic, collateral policy, counterparty due diligence, risk disclosures, client reporting, third party contracts, custody links, withdrawal and return processes, and complaint handling. Firms should stress test whether clients understand rehypothecation, loss, yield, liquidity and counterparty risk.
Consultation Outcome
  • The FCA confirmed retail protections for lending and borrowing as part of the final PS26/11 package
  • The rules preserve firm accountability even where service delivery uses third parties
  • Final refinements address collateral and service design issues but keep lending and borrowing inside a regulated conduct baseline
  • This is one of the areas where Consumer Duty evidence will matter because product risk can be hard for retail clients to understand
NCFA Perspective Crypto lending is no longer being treated as a purely private yield product. The UK regime pushes it toward regulated product governance, clear client information and controlled service design. That could reduce high risk models but may also create room for safer institutional and collateral services.

Staking

Requirements The staking framework in PS26/11 confirms retail protections and targeted refinements to staking rules, including treatment of auto staking. Staking services create operational, validator, custody, disclosure and client outcome risks that connect to safeguarding, operational resilience and Consumer Duty.
  • Firms providing staking services must identify whether the service is within the regulated perimeter and which client protections apply
  • Client information should explain staking arrangements, validator risk, lockups, slashing, rewards, fees, liquidity, tax or reporting context where relevant and operational dependencies
  • Auto staking treatment was refined in the final rules
  • Where staking uses validators, node operators, custodians or other service providers, the authorised firm remains accountable for regulated obligations
  • Operational resilience guidance identifies validator risk and validator outages as crypto specific risks
  • Firms need records showing staking instructions, rewards, fees, losses, slashing events, service disruptions and client communications
Implementation Implementation should include validator due diligence, staking policy, client consent flows, reward calculation controls, fee disclosure, slashing incident workflow, exit queue process, asset segregation, outsourcing or third party arrangements and resilience testing for validator outages. Firms should connect staking risk to Consumer Duty outcomes and complaint handling.
Consultation Outcome
  • The FCA retained staking inside the final activity framework while making targeted refinements
  • Operational resilience guidance specifically highlights validator risks and outages
  • The final approach does not remove staking risk but requires firms to evidence controls and client understanding
  • Further market practice will likely shape supervisory expectations after go live
NCFA Perspective Staking is a good example of regulation translating crypto native activity into financial services controls. The opportunity is not simply offering yield. It is making staking understandable, monitored, resilient and institutionally acceptable.

Safeguarding and Custody

Requirements The FCA applies safeguarding requirements through CASS 17 for qualifying cryptoassets and related CASS amendments. Custody and safeguarding are central to the regime because many cryptoasset failures come from weak asset control, poor segregation, private key compromise, unclear client ownership or inadequate third party oversight.
  • Firms safeguarding qualifying cryptoassets must comply with CASS 17 requirements tailored to cryptoasset custody
  • Safeguarding requirements interact with CASS 16 where tokenized stablecoin backing assets or qualifying stablecoin custody is involved
  • Firms need arrangements for holding, recording, reconciling and protecting client cryptoassets
  • Private key management, wallet infrastructure, access controls, signing authority and recovery procedures are core operational controls
  • Third party custody or infrastructure arrangements require due diligence, contractual protections and ongoing oversight
  • Client reporting must ensure clients can access information, including where information is available on chain
  • Custody controls link to operational resilience, financial crime, Consumer Duty, dispute resolution, complaints and prudential requirements
Implementation Custodians and firms using custodians should document wallet architecture, key ceremony, MPC or HSM controls, cold and warm wallet policies, access roles, transaction approval, reconciliation, incident response, third party oversight, bankruptcy analysis, client asset records, insurance or financial resources and client reporting. Firms should test private key loss, unauthorized signing, chain outage, custodian failure and reconciliation breaks.
Consultation Outcome
  • The FCA confirmed application of safeguarding requirements under CASS 17 with cryptoasset specific adjustments
  • The FCA did not create a separate SM&CR prescribed responsibility for digital asset custody because existing custody PRs cover custody of a broad range of assets
  • Limited intragroup custody is permitted for stablecoin backing arrangements subject to safeguards
  • The final regime gives custody a central role in institutional trust and consumer protection
NCFA Perspective Custody is likely to be the most important infrastructure layer in the regime. Regulated crypto markets cannot scale without credible asset control, private key governance, reconciliation and failure recovery. This is where specialist infrastructure providers may gain durable advantage.

Prudential Requirements

Requirements PS26/12 creates a prudential framework for regulated cryptoasset firms covering capital, own funds, concentration risk, liquid assets, overall risk assessment and public disclosure. It uses CRYPTOPRU and COREPRU amendments to establish a baseline that reflects cryptoasset risks without simply importing bank prudential rules.
  • Firms must meet own funds definition and composition requirements
  • Own funds requirements include fixed overhead and K factor based components where applicable
  • The operational risk K factor for stablecoin issuance was reduced from 2% to 1% in the final rules
  • The revised market risk framework applies a single 40% net cryptoasset position requirement for K NCP where assets can be prudently valued and are admitted to a UK QCATP
  • Cryptoassets that do not meet the conditions are deducted from regulatory capital and subject to a 100% volatility adjustment for K CCD
  • Concentration risk and liquid asset requirements apply to support resilience
  • Firms must conduct overall risk assessments and maintain adequate financial resources
  • Public disclosure obligations are included with proportionality refinements
  • Prudential obligations apply alongside activity specific conduct, custody, stablecoin and Handbook requirements
Implementation Firms should build prudential models by activity and balance sheet exposure. Required work includes own funds classification, K factor calculation, stablecoin issuance exposure, custody and platform activity mapping, cryptoasset valuation policy, capital deduction logic, liquid asset monitoring, concentration risk limits, stress testing, management information, public disclosure process and board sign off.
Consultation Outcome
  • The FCA largely maintained the prudential architecture but recalibrated key areas for proportionality
  • Stablecoin operational risk capital was reduced from 2% to 1%
  • The market risk framework was simplified to a 40% treatment for qualifying prudently valued assets admitted to a UK QCATP and deduction or 100% volatility adjustment for others
  • The public disclosure regime was made more proportionate
  • Respondents supported prudential clarity but raised concerns about calibration, competitiveness and operational burden
NCFA Perspective Prudential rules turn crypto firms into regulated financial businesses with capital and liquidity discipline. The effect may be fewer casual entrants, but stronger survivors. The commercial opportunity is prudential analytics, treasury management, disclosure tooling and capital efficient operating models.

Consumer Duty and Conduct

Requirements PS26/13 applies key FCA Handbook standards to regulated cryptoasset activities, including Consumer Duty, COBS, conduct rules, dispute resolution, compensation treatment and reporting. Most firms carrying on regulated cryptoasset activities will be subject to these cross cutting obligations, with specific exceptions for certain professional client platform activity and platform member transactions.
  • Consumer Duty applies to relevant cryptoasset activity subject to defined scope and exclusions
  • Principles 6 and 9 and Consumer Duty do not apply when operating a qualifying CATP for professional clients
  • Certain Principles and Consumer Duty do not apply to transactions concluded between members or participants under the rules of a qualifying cryptoasset trading platform
  • The FCA clarified Consumer Duty guidance on territorial scope, fair value, consumer support, consumer understanding and manufacturer or distributor roles
  • COBS standards apply to relevant cryptoasset conduct and communications
  • Firms need evidence that products, services, support and communications deliver appropriate outcomes
  • DISP and Financial Ombudsman Service access apply to relevant complaints
  • Compensation and redress rules are part of the broader Handbook application
Implementation Implementation should include Consumer Duty outcome mapping by activity, customer journey review, product governance, fair value assessment, communication testing, support standards, vulnerability considerations, complaints data, MI dashboards and board reporting. Crypto firms should prove that customers understand custody, stablecoin, staking, lending, execution and volatility risks before and after purchase.
Consultation Outcome
  • The FCA made clarifications rather than retreating from applying Consumer Duty and conduct standards
  • UK issued qualifying stablecoins were excluded from the definition of restricted mass market investments
  • Consumer Duty guidance was clarified across fair value, support, understanding and supply chain roles
  • The final approach signals that crypto conduct standards should converge with regulated financial services expectations
NCFA Perspective This is one of the strongest differences between regulated crypto and offshore crypto. The UK model requires firms to evidence consumer outcomes, not only publish risk warnings. Firms that can make complex products understandable may have a material trust advantage.

Governance and SM&CR

Requirements The FCA applies Senior Management Arrangements, Systems and Controls and the Senior Managers and Certification Regime to cryptoasset firms. Governance requirements cover risk management, controls, accountability, prescribed responsibilities, operational resilience, financial crime, custody and board oversight.
  • SYSC 4 to SYSC 10 apply to qualifying cryptoasset firms according to firm type and common platform status
  • SM&CR applies to relevant cryptoasset firms with proportionality and threshold treatment
  • The enhanced SM&CR threshold for qualifying UK stablecoin issuers is set at £20 billion, intended to capture the most significant stablecoins over time
  • Smaller and medium sized stablecoin issuers are not expected to fall into enhanced SM&CR at commencement
  • Existing prescribed responsibilities are used for custody rather than creating separate digital asset custody PRs
  • Senior management responsibilities include financial crime, operational resilience, compliance, safeguarding, prudential risk and conduct outcomes where relevant
  • Governance must support FCA supervision, authorisation evidence and ongoing compliance
Implementation Firms should build a management responsibilities map, committee structure, board reporting pack, policy owner register, control owners, prescribed responsibility allocation, SMF evidence, certification population, conduct training, breach escalation and decision records. Stablecoin issuers should monitor whether scale could bring enhanced SM&CR into scope over time.
Consultation Outcome
  • The FCA adjusted the enhanced threshold for qualifying UK stablecoin issuers in light of Bank of England proposals
  • The FCA expects the £20 billion threshold to capture 1% or less of the firm population and likely no firms at commencement
  • The FCA declined to create separate prescribed responsibilities for cryptoasset custody
  • Governance requirements were largely maintained with targeted proportionality refinements
NCFA Perspective Governance is where regulatory permission becomes accountable execution. The UK is not just authorising products. It is assigning responsibility to named leaders, boards and control functions. That will shape who can credibly scale.

Operational Resilience

Requirements The FCA extends SYSC 15A operational resilience to cryptoasset firms and provides FG26/6 to explain cryptoasset specific risks. Firms must identify important business services, set impact tolerances, map dependencies and conduct scenario testing. SYSC 4, SYSC 7 and SYSC 8 complement the framework through risk management, controls and outsourcing requirements.
  • Firms must have sound, effective and comprehensive strategies, processes and systems proportionate to their nature, scale and complexity
  • Important business services must be identified and mapped across people, processes, technology, facilities and information
  • Impact tolerances must be set and tested through severe but plausible scenarios
  • Crypto specific risks include smart contract vulnerabilities, private key security risks, validator risks, service disruptions, cyber risks, DLT dependencies and emerging technologies such as AI and quantum computing
  • FG26/6 highlights cyber and technology resilience, cryptographic key and infrastructure safeguarding, continuity and disruption planning
  • Outsourcing expectations cover custody infrastructure, MPC and HSM providers, validator services, cloud providers and security critical transaction signing infrastructure
  • Permissionless DLT use should not be treated as outsourcing under SYSC 8.1.1R, but firms remain responsible for operational resilience controls
  • Firms should conduct targeted vulnerability scans, penetration tests and maintain monitoring and logging evidence
Implementation Implementation should produce a live resilience map for every important business service. Firms need dependency mapping, wallet and key infrastructure controls, validator due diligence, smart contract testing, cyber controls, incident playbooks, impact tolerance testing, penetration testing, cloud and third party oversight, logging, operational dashboards and board reporting. Scenario tests should include private key compromise, smart contract failure, validator outage, chain disruption, trading outage, stablecoin reconciliation failure and custodian failure.
Consultation Outcome
  • 91% of respondents supported extending SYSC 15A to cryptoasset firms and 88% supported the guidance approach
  • 98% supported the view that permissionless DLTs should not be treated as outsourcing
  • The FCA kept the extension of operational resilience while adding crypto specific guidance
  • Further non Handbook guidance on DLT operational resilience is expected later
NCFA Perspective Operational resilience is where the FCA regime becomes more than conduct regulation. Crypto firms are technology firms with financial risk. The UK framework makes uptime, key security, third party dependency and recovery capability part of the regulatory value proposition.

Financial Crime

Requirements PS26/13 applies the financial crime elements of SYSC 6, the Financial Crime Guide and Financial Crime Thematic Reviews to firms conducting regulated cryptoasset activities. These obligations sit alongside the Money Laundering Regulations and Travel Rule obligations already applicable to UK cryptoasset exchange providers and custodian wallet providers.
  • Cryptoasset firms conducting regulated activities must follow the same financial crime framework as other FSMA authorised firms where applicable
  • Relevant Handbook references include SYSC 6.1.1R adequate policies and procedures, SYSC 6.3.1R systems and controls, SYSC 6.3.3R financial crime risk assessments, SYSC 6.3.8R senior manager responsibility and SYSC 6.3.9R MLRO
  • Firms must comply with MLRs and the Travel Rule alongside FSMA obligations
  • Policies and procedures must be comprehensive and proportionate to the nature, scale and complexity of activities
  • Controls should identify, assess, monitor and manage money laundering, sanctions, fraud, terrorist financing, bribery, corruption and market abuse related risk
  • Financial crime evidence must connect to onboarding, transaction monitoring, wallet screening, custody, stablecoin issuance, trading, lending and staking
Implementation Implementation should include risk assessment, customer due diligence, wallet and blockchain analytics, sanctions screening, Travel Rule workflow, suspicious activity reporting, transaction monitoring, fraud controls, stablecoin redemption screening, market abuse escalation, MLRO governance, senior manager accountability, periodic control testing and audit trails.
Consultation Outcome
  • The FCA retained the proposal to apply financial crime rules and guidance to cryptoasset firms
  • The FCA views the same financial crime baseline as proportionate for cryptoasset firms despite sector specific risks
  • The regime operates alongside MLR registration and Travel Rule obligations, so firms face overlapping compliance layers
  • Financial crime controls become part of authorisation readiness and ongoing supervision
NCFA Perspective Financial crime is central to regulatory legitimacy. The UK regime will reward firms that can combine on chain analytics with traditional financial crime governance. This is also a clear opportunity for regtech, wallet intelligence and compliance automation.

Reporting and Redress

Requirements PS26/13 applies reporting, dispute resolution and redress architecture to regulated cryptoasset activities. Firms need to report to the FCA, maintain records, handle complaints, provide access to the Financial Ombudsman Service where relevant and preserve evidence across product, custody, execution, conduct and prudential areas.
  • Regulatory reporting applies to cryptoasset firms under the Handbook application package
  • Firms need data on activities, clients, complaints, prudential position, operational resilience, financial crime controls and other supervisory metrics
  • DISP and access to the Financial Ombudsman Service apply where relevant
  • Complaint handling must connect to Consumer Duty, client reporting, custody, execution, lending, staking and stablecoin redemption issues
  • Record keeping requirements apply across admissions, market abuse, client orders, transactions, lending, borrowing, staking, safeguarding and reporting
  • Public disclosure obligations apply in the prudential regime with proportionality refinements
  • Firms need evidence retention policies that allow supervisory reconstruction of decisions and client outcomes
Implementation Firms should build a reporting data model before go live. Required work includes regulatory returns ownership, data lineage, complaints taxonomy, FOS workflow, prudential reporting data, custody records, client statements, execution data, surveillance cases, operational incidents, financial crime alerts and board MI. Manual reporting will be risky given the breadth of the regime.
Consultation Outcome
  • The FCA made focused amendments to reporting requirements in PS26/13
  • The prudential disclosure regime was made more proportionate
  • The overall approach keeps crypto inside existing FCA supervisory and redress architecture
  • Reporting and redress obligations will expose weak data governance quickly after authorisation
NCFA Perspective Reporting is the regime’s memory. Firms that cannot reconstruct decisions, client outcomes, custody records or prudential positions will struggle to defend their operating model. Good reporting infrastructure becomes a strategic asset, not only a compliance cost.

International Firms

Requirements The FCA’s approach to international cryptoasset firms sets expectations for firms seeking UK authorisation while serving UK consumers. It focuses on threshold conditions, location of offices, effective supervision, appropriate resources, suitability and business model. The final guidance clarifies branch treatment for dual regulated firms where PRA conditions are satisfied.
  • International firms requiring FCA authorisation must meet minimum standards at application and on an ongoing basis
  • The FCA considers location of offices, effective supervision, appropriate resources, suitability and business model
  • The FCA identifies higher consumer and market harm risk where international firms serve UK customers through branches rather than UK legal entities
  • Dual regulated firms may operate through a UK branch where the PRA is satisfied threshold conditions and ongoing requirements are met
  • International models must demonstrate accountability, supervision, client protection, operational resilience and financial crime controls
  • Cross border liquidity access may be relevant, but does not remove UK authorisation and governance expectations
Implementation International firms should prepare a UK market access file covering branch or subsidiary choice, governance, UK senior managers, service model, outsourcing, group support, capital, liquidity, client disclosures, data location, custody, financial crime, operational resilience and how UK customers are protected if overseas operations fail.
Consultation Outcome
  • The FCA clarified the international firm approach after feedback in CP26/4
  • The final guidance acknowledges branches for dual regulated firms where PRA expectations are met
  • The FCA did not make overseas access easy simply because liquidity is global
  • The approach tries to balance global liquidity with UK accountability and effective supervision
NCFA Perspective This is where the UK tries to attract global crypto firms without importing offshore risk. The strongest firms will treat UK authorisation as a credible market badge, not a light touch registration.

DeFi

Requirements The FCA’s current approach to decentralised finance is to apply rules where there is an identifiable controlling entity, with separate guidance to follow on how decentralisation will be assessed in practice. DeFi is treated as a range of financial services marketed with a high degree of automation rather than as a blanket exemption from regulation.
  • Rules apply where there is an identifiable controlling entity
  • Separate guidance is expected on how decentralisation will be assessed
  • DeFi interfaces, arrangements and controlling entities may fall within regulated activity analysis
  • Automation does not by itself remove regulatory obligations
  • Firms must assess governance, control, user interface, protocol dependency, custody, financial promotion, market abuse, lending, staking and consumer risk
  • DeFi related activity may also raise operational resilience, financial crime, Consumer Duty and international firm issues
Implementation Firms should document who controls the interface, protocol parameters, governance keys, admin rights, fee flows, custody, upgrade authority, user onboarding, compliance controls and consumer communications. A DeFi implementation file should show whether the business is genuinely decentralised or whether an identifiable entity directs regulated activity.
Consultation Outcome
  • The FCA retained the principle that identifiable controlling entities bring DeFi activity within regulatory reach
  • The FCA acknowledged the need for separate guidance on decentralisation assessment
  • The final approach avoids treating DeFi labels as determinative
  • This remains a watch area because future guidance will likely affect interface operators, protocol sponsors and infrastructure providers
NCFA Perspective DeFi is the frontier test for the regime. The key issue is control. If a business can control access, fees, governance, listings or user experience, regulators are unlikely to treat it as outside the market structure simply because the protocol uses smart contracts.

UK Cryptoasset Regulations FAQ

When do the UK cryptoasset regulations start?

The new FCA cryptoasset regime starts on 25 October 2027.

When can firms apply for FCA cryptoasset authorisation?

The scheduled application period runs from 30 September 2026 to 28 February 2027. Firms seeking to rely on saving and transitional provisions should apply within that period.

Does an existing MLR registration become FCA authorisation?

No. Existing registrations and permissions do not automatically convert. A firm carrying on an in scope regulated cryptoasset activity will need the relevant FSMA permission.

Which cryptoasset activities are covered?

The regime covers activities including operating qualifying cryptoasset trading platforms, dealing, arranging, stablecoin issuance, custody, lending, borrowing and staking. Admissions, disclosures and market abuse rules also apply.

Which FCA rulebooks apply to cryptoasset firms?

The package includes the CRYPTO sourcebook, CASS 16 and CASS 17, CRYPTOPRU and COREPRU, plus relevant Consumer Duty, COBS, SYSC, SM&CR, DISP, reporting and operational resilience requirements.

What should firms prioritise before applying?

Firms should confirm scope, prepare governance and financial resource evidence, document custody and resilience controls, assess Consumer Duty outcomes and build a complete authorisation file for their business model.

Continue Exploring

How Tokenization Became a Business Investors Can MeasureConnects the FCA regime to the shift from crypto speculation toward measurable, investable tokenized infrastructureRead the story
How Is Crypto Custody Regulation Changing?Useful for custody, safeguarding, CASS 17, institutional trust and operational control questionsRead the question
UK FCA Plans Full Crypto Licensing Regime by 2026Background on the UK path from policy design and consultation toward a full cryptoasset regimeReview the buildout
FCA Chair on Crypto, Stablecoins and Digital Asset RegulationPolicy signal connecting crypto regulation, stablecoins, consumer risk, scams and the FCA's long running supervisory directionRead the speech context
Stablecoin Data Shows Payments Reality GapMarket evidence on why stablecoin payments need trust, liquidity, distribution and operating infrastructureRead the analysis
Tokenized Infrastructure Is Changing How Markets OperateMarket infrastructure context for tokenized cash, settlement, collateral, custody and regulated railsRead the insight

From Regulation to Opportunity

The FCA regime creates demand for regulated infrastructure across stablecoins, custody, market surveillance, disclosure, trading systems, prudential analytics, operational resilience, Consumer Duty evidence, reporting and compliance automation. The closest NCFA opportunity layer is the Programmable Stablecoin Payments brief, which examines where compliant stablecoin infrastructure can create practical payment and settlement use cases.

Open the Stablecoin Payments Opportunity Brief


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights

NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


How Tokenization Became A Business Investors Can Measure

June 30, 2026 | NCFA Story Intelligence | Digital Assets Blockchain And Tokenization, Capital Markets And Market Infrastructure
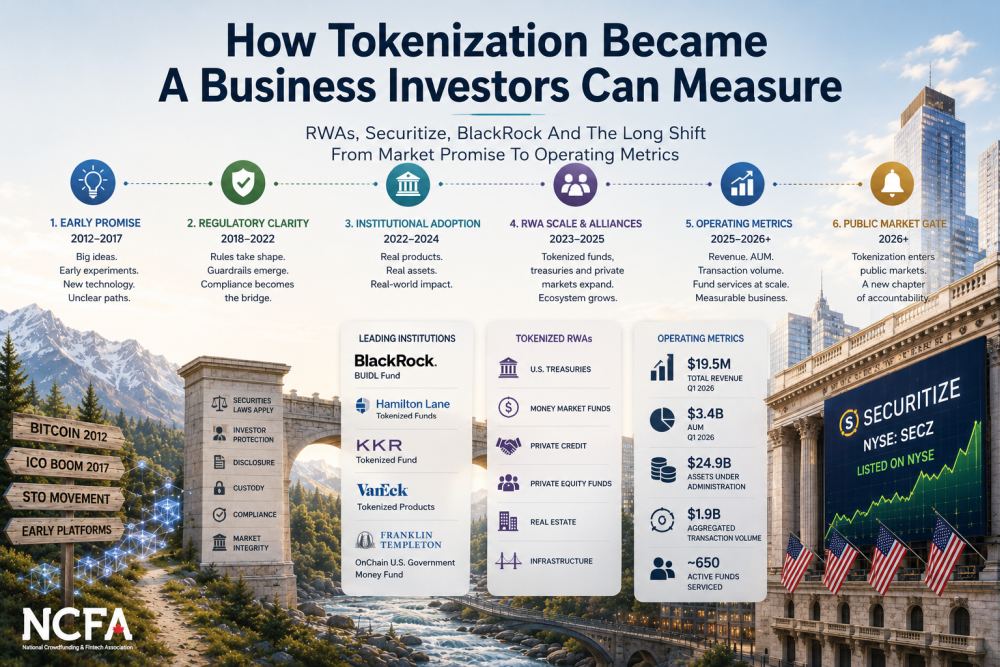
NCFA Story – How Tokenization Became A Business Investors Can Measure

How Tokenization Became A Business Investors Can Measure

Tokenization promised to change capital markets for more than a decade.

The promise is still attractive. Put ownership on chain. Reduce paperwork. Automate compliance. Improve access. Speed up settlement. Make private assets easier to distribute, manage, and transfer.

But markets don’t run on promises. They run on operating models, regulation, distribution, controls, liquidity, and trust.

That’s why Securitize’s expected NYSE listing is the trigger. The listing isn’t the whole story. It’s the latest chapter in a longer path from tokenization as a market idea to tokenization as a business investors can measure.

The first wave sold a powerful idea. Security tokens, STOs, fractional assets, real estate tokens, private shares, and blockchain based markets promised to bring traditional securities into programmable digital form. The early security token field was framed as a more regulated answer to the ICO boom.

The market didn’t overhaul itself. Early security token projects ran into the same walls: unclear regulation, thin liquidity, limited distribution, custody questions, fragmented platforms, investor eligibility rules, and the simple reality that a tokenized security still has to behave like a security.

The First Wave Overpromised 2017 to 2021

Tokenization didn’t fail because the idea was weak. It stalled because the operating system around the idea was incomplete. A digital wrapper couldn’t replace compliance, custody, onboarding, transfer restrictions, reporting, market access, and investor trust.

The hard work was never only technical. A tokenized fund still needs investor onboarding, KYC, AML, transfer rules, custody, servicing, reporting, distributions, tax records, corporate actions, and permissioned secondary transfers. Those aren’t marketing features. They’re the boring parts that make markets work.

Regulators kept reminding the market that labels don’t change obligations. Hester Peirce’s point that tokenized securities still have to follow securities laws captured the practical boundary. Faster settlement and automation don’t remove investor protection, disclosure, and market integrity requirements.

The Wall Was Operational 2021 to 2024

Tokenization had to grow up by becoming less exciting. The breakthrough wasn’t a new slogan. It was transfer agency, broker dealer access, fund administration, compliance workflows, custody, settlement, investor records, and regulated distribution working together.

Regulators Drew The Lines 2023 to 2026

Tokenization matured when regulators stopped treating the technology as the story and started defining how tokenized securities, funds, intermediaries, custody, settlement, and investor protection would work inside regulated markets. Singapore tested tokenised funds and fixed income through Project Guardian. Hong Kong issued tokenisation guidance for securities and investment products. The UK built a fund tokenisation blueprint with HM Treasury and the FCA. In the US, the message became clearer: tokenized securities are still securities. The breakthrough wasn’t escaping regulation. It was learning how to operate through it.

Real world assets changed the packaging. The market stopped asking whether everything should become tokenized and started asking which assets actually benefit. Treasuries, money market funds, private credit, private equity funds, and alternative assets became more practical test cases than vague claims about digitizing every market.

Private markets gave tokenization a clearer job. Citi, Wellington Management, and WisdomTree tested private market tokenization in 2024, showing how smart contracts could support operating efficiency in traditionally manual private market processes.

RWAs Made The Story More Practical 2023 to 2026

Real world assets gave tokenization a narrower, more useful frame. The question became less “can blockchain transform markets?” and more “which assets benefit from digital ownership records, embedded rules, faster settlement, easier distribution, and better administration?”

Hamilton Lane used tokenization to lower access friction. In 2022, Hamilton Lane and Securitize said qualified US investors would gain access to tokenized feeder funds tied to direct equity, private credit, and secondary transaction strategies.1 Securitize later said one Hamilton Lane fund reduced the minimum investment from about $5 million to $20,000.2

KKR showed that major alternatives managers would test the model. Securitize launched a tokenized fund offering exposure to KKR’s Health Care Strategic Growth Fund II in 2022, framing the product around broader access to alternative investments through digital ownership.3

Institutions Entered Through Real Products 2022 to 2024

The institutional story didn’t begin with a mass migration. It began with specific products solving specific problems: access to alternatives, investor onboarding, fund administration, distribution, compliance, and asset servicing. That was the path from tokenization as a pitch to tokenization as a product design choice.

BlackRock changed the market’s confidence level. BlackRock launched BUIDL, its first tokenized fund, on Ethereum in March 2024. The fund was backed by cash, US Treasury bills, and repurchase agreements, with BNY Mellon enabling interoperability between digital and traditional markets.4

BUIDL became a measurable adoption signal. In March 2025, Securitize said BUIDL surpassed $1 billion in AUM and identified itself as the tokenization provider for the fund.5 BlackRock’s BUIDL launch became one of the clearest institutional signals that tokenization was entering regulated asset management.

BlackRock Made The Signal Harder To Ignore 2024 to 2025

BlackRock didn’t make tokenization real by itself. It made the question harder to dismiss. Once the world’s largest asset manager put a regulated tokenized fund into market with named service providers and real AUM, tokenization stopped looking only like a crypto sector claim.

Securitize turned the thesis into operating data. In Q1 2026, Securitize reported $19.5 million in total revenue, up 39% year over year, $3.4 billion in AUM at quarter end, $24.9 billion in assets under administration, $1.9 billion in aggregated transaction volume, and roughly 650 active funds serviced through Securitize Fund Services.6

Those numbers change the conversation. Investors can ask normal operating questions: revenue mix, servicing fees, client concentration, transaction volume, fund growth, margins, profitability, operating leverage, customer retention, regulatory execution, and how much tokenization demand converts into durable revenue.

The Scoreboard Appeared 2026

This is the biggest change. Tokenization no longer has to be judged only by white papers, pilots, or executive quotes. Public investors can measure platform economics, adoption, volume, servicing activity, losses, revenue growth, and execution. That is what makes the story different from earlier cycles.

The listing is the trigger. Securitize and Cantor Equity Partners II said the business combination was expected to raise approximately $400 million in gross proceeds, close after shareholder approval and customary conditions, and list on the NYSE under ticker SECZ.7

The listing doesn’t settle the thesis. It exposes the thesis to market discipline. A listed tokenization company has to explain growth, losses, expenses, institutional demand, regulatory risk, competitive pressure, and whether tokenized fund adoption can become a durable public company business.

Onslaught Or Trickle? The Next Test

Tokenization has promised market overhaul before. The stronger evidence now is operating evidence: institutional products, regulated service providers, AUM, assets under administration, transaction volume, and public market accountability. The open question is whether those signals mark a breakout or another careful phase of controlled adoption.

Canada has a practical watchlist. The opportunity isn’t to copy a US listing. Canadian firms can look across the tokenization value chain: custody, transfer services, fund administration, compliance, exempt market distribution, private market platforms, digital identity, investor onboarding, reporting, and secondary trading.

Regulated product design may decide the next chapter. The OSC’s long term asset fund project pointed to possible retail exposure to traditionally inaccessible assets and raised the opportunity for tokenized long term funds with embedded compliance, transparent records, fractional access, and guardrails.

Canada Should Watch The Operating Layer Canada Lens

Canada hasn’t led the global tokenization rulebook, but it does have useful pieces: digital asset custody, exempt market distribution, fund administration, wealth platforms, private market access, compliance technology, investor onboarding, and emerging long term asset fund policy work. The opportunity isn’t just token issuance. It’s building the trusted services that let regulated tokenized markets function.

Tokenization didn’t become measurable overnight. It moved through years of big claims, stalled experiments, regulatory pushback, operating layer buildout, institutional product design, and real world asset packaging before public markets had a company they could evaluate with ordinary business questions.

That may be the clearest test. The first tokenization wave asked investors to believe in a technology. The next wave will ask investors to evaluate execution. Revenue. Margins. Assets. Transactions. Clients. Losses. Retention. Market share. Operating leverage. That is a much harder test, and a much more useful one.

For Canada, the lesson is practical. The next winners may not be the firms issuing the tokens. They may be the firms solving everything around them: custody, compliance, investor onboarding, fund administration, reporting, liquidity, and regulated distribution. That’s where durable businesses are often built, and where Canada’s capital markets innovation map can help identify opportunities that are still taking shape.

What Happens Next?

  • Will Securitize’s public market performance strengthen or weaken the institutional tokenization thesis?
  • Will public investors reward tokenized AUM growth, or focus more heavily on margins, losses, and client concentration?
  • Will RWAs expand from Treasuries and tokenized funds into broader private market access?
  • Will secondary liquidity improve enough to change how investors use tokenized assets?
  • Will Canadian firms build around custody, compliance, fund administration, distribution, and reporting instead of chasing token issuance alone?
  • Is tokenization approaching a tipping point, or still moving through a controlled institutional trickle?

What Did You Think?

What operating metric would convince you that tokenized markets have moved beyond promise?

Share this story → Explore related intelligence → Subscribe


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


DuckDice Canada Crypto Casino Exciting Features

Jun 30, 2026

AI Image – Gaming and crypto in a modern workspace

DuckDice Crypto Casino Overview for Canadian Players and Gamers

For those exploring a fresh online entertainment experience, this platform offers an impressive array of functionalities that cater to diverse preferences. Take advantage of the enticing welcome bonuses designed to give newcomers a robust start, enhancing their initial experience significantly.

The interactive environment features a user-friendly interface that simplifies navigation, making gameplay intuitive for both novices and seasoned players. Real-time statistics and analytics allow participants to track their performances and adjust their strategies accordingly, leading to tailored gaming sessions.

Additionally, engagement opportunities abound through community-driven events and tournaments that encourage friendly competition. Loyalty programs reward consistent players with perks and incentives, fostering a welcoming atmosphere. All these elements contribute to a dynamic and enjoyable online experience that is hard to resist.

Innovative Game Selection and Formats

An extensive array of gaming options caters to various preferences, ensuring that players can find something that suits their style. Unique titles often feature inventive gameplay mechanics, elevating the overall experience. Look out for offerings that combine traditional casino elements with modern twists, such as skill-based components or story-driven adventures, especially when exploring platforms in the crypto casino Canada segment.

Live-action games have transformed the entertainment landscape, allowing players to engage with real dealers in real-time. This format delivers an immersive atmosphere that mimics the ambiance of a physical venue, fostering social interaction. Consider trying out themed live shows, which blend popular culture elements into classic formats for an added layer of enjoyment.

Add-on features like progressive jackpots or customizable game settings enhance user engagement and provide opportunities for increased rewards. These options encourage diverse play styles, appealing to both casual gamers and high rollers. Regularly updated libraries help maintain interest, as new titles are introduced frequently, offering fresh and exciting challenges to explore.

Exclusive Promotions and Loyalty Programs

To enhance the gaming experience, consider engaging with various limited-time offers and promotional events. Often, these promotions come in the form of deposit bonuses, where additional funds are credited to your account upon making a qualifying deposit. Pay attention to the details, as each promotion may have specific requirements.

Another attractive option is the referral program. By inviting friends to join, players can earn bonuses or free credits for each successful signup. This not only provides rewards but also creates a sense of community among users, fostering interaction and competition.

Loyalty schemes are designed to recognize and reward consistent participation. Players accumulate points based on their activities, which can later be exchanged for bonuses, gifts, or even exclusive experiences. Regularly check the loyalty program tiers to maximize benefits as you advance through levels.

Seasonal promotions often bring additional excitement, aligning offers with holidays or significant events. Participating during these times can lead to substantial bonuses and unique prizes. Ensure to monitor announcements for these opportunities, as they can significantly boost the gaming experience.

Lastly, subscribing to newsletters or notifications is a practical way to stay informed about the latest campaigns. This ensures that players never miss an opportunity to take advantage of exclusive offers, enhancing both engagement and rewards in the long run.

User-Friendly Interface and Experience

To enhance your engagement, the platform offers an intuitive layout designed for seamless interaction. Clear navigation bars and organized menus ensure that all available activities are easily accessible, minimizing time spent searching for options.

The color scheme is soothing, with a modern aesthetic that enhances visibility. Users can quickly identify sections such as betting options, account management, and help resources. This thoughtful design allows users to focus on their gaming experience without distractions.

  • Responsive Design: The site is optimized for both desktop and mobile use, maintaining functionality across devices.
  • Quick Load Times: Pages load rapidly, ensuring that users can jump from one activity to another without delays.
  • Clear Call-to-Action Buttons: Important features like "Join," "Withdraw," and "Deposit" are highlighted, which helps in smooth transactions.

Customer support is easily accessible, with a dedicated help center and live chat functionality. This feature enables users to receive assistance quickly, contributing to a positive overall experience.

Regular updates and user feedback integration demonstrate commitment to enhancing the interface. Continuous monitoring and tweaks based on popular user requests foster a community-focused environment, where player satisfaction is prioritized.

Secure Transactions and Cryptocurrency Options

A wide range of multi-currency wallets is recommended for seamless and secure financial transfers. Look for options that support popular coins including Bitcoin, Ethereum, and various altcoins, enabling users to deposit, withdraw, and place bets with their preferred digital assets.

Security measures play a critical role in the reliability of online transactions. Implementing two-factor authentication (2FA) adds an extra layer of protection for users. Always ensure that the platform utilizes encryption protocols (like SSL) to keep personal and financial data secure from unauthorized access.

Consider utilizing platforms that offer blockchain technology for transparency. Each transaction is recorded on a public ledger, making it easier to verify and trace payments. This not only enhances privacy but also builds trust between users and the service provider.

For enhanced convenience, many users prefer platforms that enable direct cryptocurrency payments without the need for currency conversion. This can mitigate the risk associated with volatile exchange rates and hidden fees during conversions.

Cryptocurrency Transaction Speed Typical Transaction Fees
Bitcoin 10 minutes $1-10
Ethereum 15 seconds $0.50-5
Litecoin 2.5 minutes $0.01-0.05
Ripple 3-5 seconds Minimal

Evaluate the transaction limits imposed by the service. Understanding the minimum and maximum deposit and withdrawal thresholds can help manage your gameplay or betting strategy. This information is often available in the FAQ section or customer support.

Ep27-Mar 1: Blockchain Gaming and Esports with Shidan Gouran

Regularly monitor the platform’s policy on transaction discrepancies. A responsive customer support team is beneficial in resolving any issues swiftly, ensuring a hassle-free gaming experience. Always choose platforms that offer clear communication channels for such concerns.


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Canada’s Open Banking Regulatory Intelligence Guide

Jun 29, 2026 | NCFA Resource | Open Banking Open Finance, Regulation And Policy

Last updated: September 11, 2026

Canada open banking and Consumer Driven Banking regulatory intelligence guide

Canada Open Banking Rules For Readiness And Consultation

NCFA has published a new Regulatory Intelligence guide to Canada Open Banking and Consumer Driven Banking Rules. The interactive resource organizes the proposed regulations, implementation requirements, consultation questions and strategic issues shaping Canada’s regulated open banking framework.

For a broader view of Open Banking and Consumer-Driven Finance, including the Canadian market map, 146 learning modules, company intelligence, global benchmarks and interactive discussions, explore NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence.

The guide tracks accreditation, data scope, consent, authentication, security, technical standards, liability, reporting, complaints, national security review, fees and administrative monetary penalties. It also explains why consumer trust, fraud prevention and clear accountability are central to implementation. For further analysis, see Canada's Open Banking Strategy Starts With Trust.

What It Does In Practice

The resource gives readers a structured way to understand what the proposed Consumer Driven Banking Regulations would require before final rules are published.

Instead of treating the regulations as one long legal document, the guide breaks them into operating topics. Each section separates regulatory requirements, implementation work, consultation considerations and NCFA’s strategic perspective.

Canada’s open banking framework is progressing from policy design into regulatory implementation. Firms need to understand more than API access. They need to prepare evidence for accreditation, consumer consent flows, registry checks, authentication records, security safeguards, breach response, complaint procedures, service standards, reporting obligations and board level accountability.

The 60-day Canada Gazette consultation closed on August 26, 2026. The proposed regulations remain subject to finalization, while firms continue preparing for accreditation, supervision, data-sharing, consent, security and operational requirements.

Who Gets Value

This resource is useful for fintech founders, open banking platforms, financial institutions, credit unions, payment service providers, data aggregators, regtech providers, compliance teams, investors, policymakers and industry associations.

It is especially useful for organizations assessing accreditation, product design, consent architecture, data sharing duties, technical standards, cybersecurity, consumer protection and implementation costs.

Strengths And Limits

The strength of this resource is its focus on regulatory readiness. It converts the proposed Consumer Driven Banking Regulations into a practical intelligence layer that can support planning, consultation, product design and ecosystem coordination.

The guide connects the proposed regulations to Canada’s policy objectives, including stronger consumer protection, fraud mitigation, secure financial data sharing, competition and confidence in the open banking framework.

It also connects regulation to commercial opportunity. The guide identifies where read access, data portability, identity and income verification, cash flow analysis, embedded workflows, write access and open finance may create future product and infrastructure demand.

The regulations remain proposed and may change following consultation. Readers should use the guide for ecosystem intelligence and planning, not as legal, financial, investment, compliance or professional advice.

Key Resources

Canada Open Banking and Consumer Driven Banking Rules (primary NCFA Regulatory Intelligence guide)

NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence (market map, 146 learning modules, company intelligence, discussions and global benchmarks)

Canada's Open Banking Strategy Starts With Trust (consumer protection and fraud readiness)

Open Banking In Canada Opportunity Brief (commercial opportunity layer)

NCFA Financial Innovation Map (ecosystem context)

Proposed Consumer-Driven Banking Regulations (official Canada Gazette source)


National Crowdfunding and Fintech Association of CanadaThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights
NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter


Canada Open Banking and Consumer Driven Banking Rules

NCFA Regulatory Intelligence - Canada Open Banking And Consumer Driven Banking Rules
NCFA Canada | Regulatory Intelligence | Open Banking and Consumer Driven Banking | Last updated September 11, 2026 | Status proposed regulations, consultation closed
NCFA Regulatory Intelligence
This guide explains Canada’s open banking framework through the proposed Consumer Driven Banking Regulations, including accreditation, consent, data sharing, security, liability, supervision and implementation. Sources include the Canada Gazette, the Regulatory Impact Analysis Statement, the Consumer Driven Banking Act, Finance Canada, Bank of Canada materials and the Office of the Privacy Commissioner of Canada’s August 26 submission.
Canada Open Banking

Proposed Consumer Driven Banking Regulations

Canada Open Banking and Consumer Driven Banking Rules

Canada’s proposed Consumer Driven Banking Regulations establish the operating framework for open banking. They address accreditation, consumer consent, data sharing, security, technical standards, liability, complaints, reporting, national security review and enforcement.

Use this guide to understand the proposed requirements, the implementation work they create and the post-consultation issues that may affect banks, credit unions, payment service providers, fintechs, consumers and small businesses.

The 60-day consultation closed August 26, 2026. The regulations remain proposed while Finance Canada considers feedback and prepares the next regulatory steps. Firms can use the published draft for planning, but final requirements and implementation timing may still change.

For a broader view of Open Banking and Consumer-Driven Finance beyond the regulatory framework, explore NCFA Open Banking & Consumer-Driven Finance Interactive Intelligence, including the Canadian Market Map, 146 learning modules, company intelligence, discussions, innovation themes and global benchmarks.

Canada’s Open Banking and Consumer Driven Banking Journey

Canada has advanced from open banking policy development into proposed Consumer Driven Banking Regulations under Bank of Canada oversight. The consultation closed on August 26, 2026. The current stage is regulatory finalization and supervisory preparation.
Launch read access and data mobility
Next write access
Consultation2018 to 2022 open banking policy review
Framework2023 to 2024 Consumer Driven Banking design
2026 Currentconsultation closed, final rules pending Bank of Canada supervision framework and implementation preparation
Read Accesslaunch phase secure data sharing and data mobility
Data Productsnear term verification, cash flow and embedded workflows
Write Accessnext phase payment initiation and account actions
Open Financelonger term broader financial product scope

Impact Analysis

Key figures from the Regulatory Impact Analysis Statement and proposed regulations.
$13.2BEstimated 10 year benefits
$457.7MEstimated 10 year costs
9MCanadians using data sharing services
680Affected businesses in central scenario
578Small businesses affected
$89,133Average annualized small business cost estimate
99.5%Monthly endpoint availability
$10MMaximum entity or ATPSP penalty

Regulatory Intelligence Explorer

Navigate the proposed regulations by topic. Each section separates requirements, implementation work, post-consultation issues to watch and NCFA’s strategic perspective.

Overview

Requirements The proposed regulations support implementation of the Consumer Driven Banking Act and create the operating layer for Canada’s open banking framework. They prescribe the data covered by the Act, accreditation information and requirements, accreditation fees, review timelines, revocation notices, accredited third party service provider requirements, national security information requirements, Ministerial review timelines, data sharing duties, exceptions to sharing, service standards, security safeguards, breach reports, responsible officer information, authentication steps, consumer signs, change notices, annual reporting, record keeping, liability related consumer notices, complaint procedures, technical standards body reporting, evidentiary privilege, assessments, administrative monetary penalties and coming into force rules.
  • Definition of Act and prescribed covered data
  • Accreditation applications for federal or provincial financial institutions, RPAA registered payment service providers, other entities and accredited third party service providers
  • Bank of Canada electronic application system, accreditation fee, refusal review and revocation processes
  • National security information package, Ministerial decision period, review period, extensions and review rights
  • Registry based verification before sharing data and exceptions where sharing can be withheld
  • Service standards for response times, endpoint availability, planned outages and traffic management
  • Security safeguards, breach reporting and responsible officer reporting
  • Authentication, acknowledgement and consent connected to secure data sharing
  • Notices, annual reporting, record keeping, liability, complaints, technical standards body reporting, assessments and violations
Implementation Organizations should build a regulatory inventory that maps each requirement to a system, policy owner, evidence file and supervisory reporting obligation. The Bank of Canada says its supervisory framework will cover participating entities, governance, risk management, operational resilience and monitoring of trends and issues. The first implementation work is not only API build. It includes accreditation evidence, national security information, data classification, registry checks, consent design, authentication records, breach playbooks, service monitoring, complaint intake, record retention, change notices, fee modelling, ATPSP contracts and board level accountability.
Post-Consultation Watch
  • Whether the framework gives enough implementation runway between final regulations, Bank of Canada guidance and coming into force
  • Whether proportionality is strong enough for small firms and RPAA registered payment service providers without reducing consumer trust
  • Whether guidance should clarify connections between fraud, consent, complaints, liability, security events and record keeping
  • Whether the technical standards body, conformance testing and service performance rules should be clearer before launch
  • Whether the cost and reporting model supports competition or favours organizations with existing compliance infrastructure
  • Whether consumers and SMEs will be able to understand which entities are accredited, which data is covered and how complaints or deletion requests work
August 26 Privacy Commissioner Submission The Office of the Privacy Commissioner of Canada supports the aims of consumer-driven banking and several privacy protections in the proposed regulations, but recommends changes before finalization.
  • Specify the individual data elements covered by the framework more clearly so consumers can understand what may be shared
  • Strengthen accreditation evidence in several pathways, including safeguards, complaints, authentication, dashboards, technical-standard evidence and selected insurance or integrity requirements
  • Narrow the consent exception for publicly available data so it does not capture information where a consumer has a reasonable expectation of privacy
  • Add an overarching requirement for safeguards appropriate to the sensitivity of the data as technology and threats change
  • Clarify coordination between the Privacy Commissioner and the Bank of Canada where privacy and supervisory responsibilities intersect
NCFA Perspective This is a trust and market structure test. Canada is defining the participation standard for a regulated financial data market. The strongest framework will not be the one with the most rules. It will be the one that makes safe participation practical, keeps consumer control understandable and lets credible new entrants compete without pushing the ecosystem into a narrow, incumbent led implementation path.

Application and Data

Requirements The regulations define the Act and prescribe the data to which the consumer driven banking framework applies. Covered data includes data relating to consumers of the covered products or services, account and product identifiers, the terms under which products and services are provided, balances or amounts owing, completed, pending and pre authorized transactions, and information about products or services available or offered to consumers. The data scope is tied to the products and services referred to in the Act and must be shared only through the regulated framework once the relevant duties apply.
  • Identity related data for consumers of covered products or services
  • Account numbers, branch numbers, transit numbers and other product or service identifiers
  • Product and service terms, including fees, interest rates and authorizations
  • Current and past balances or amounts owing
  • Completed, pending and pre authorized transaction data
  • Information about products or services available or offered to consumers, including terms
  • Historical limits apply in the data sharing rules for balances, transactions and available or offered products and services older than 24 months
  • Covered data must be tied to a valid data sharing request, participant verification, consumer authentication and consent
Implementation Participants need a data inventory that maps each covered category to source systems, product owners, API fields, consent screens, retention rules, deletion workflows, complaints, liability records and service monitoring. Data providers should identify where product terms, balances, transaction history and account identifiers are stored, how far history is available, what data is excluded, and how data quality issues will be handled when another participant relies on the information.
Post-Consultation Watch
  • Whether Finance Canada adopts the Privacy Commissioner’s recommendation to specify the individual data elements within each covered category more clearly
  • Whether the treatment of derived, inferred or enriched data needs clearer boundaries
  • Whether the 24 month historical limit is sufficient for SME finance, lending, accounting and cash flow use cases
  • Whether business accounts, joint accounts, delegated authority and multi user permissions need more detailed guidance
  • Whether future open finance expansion should be signalled earlier to reduce later redesign
  • Whether data quality, correction and dispute processes need a clearer connection to complaints and liability
NCFA Perspective Data scope is the first market boundary. A narrow read access model can still support verification, underwriting, cash flow analysis, switching, accounting and embedded workflows. The larger Canadian opportunity depends on whether this foundation can expand cleanly into write access, payment initiation and broader open finance without rebuilding the trust layer from scratch.

Accreditation

Requirements The accreditation rules prescribe different application pathways for federal or provincial financial institutions, RPAA registered payment service providers, other entities and accredited third party service providers. Applications must be submitted through the Bank of Canada electronic system. Common information includes legal and trade names, formation details, civic and mailing addresses, contact information, website, application contact, organizational and governance structure, regulatory or supervisory oversight, foreign open banking registration or accreditation status, designated officer or employee details, consumer complaint contact information, technical standard evidence and national security information. RPAA registered PSPs and other entities must also provide Canadian place of business declarations, whether they operate from a dwelling house, independent third party confirmation of security safeguards, insurance or guarantee evidence, and integrity and good character policies for individuals with significant responsibility. Other entities must additionally describe how they will meet specified Act requirements, complaint procedures, external complaints body membership status and estimated consumer numbers.
  • Federal or provincial financial institution applications include security compliance declaration, designated officer details, complaint contact, technical standard evidence and national security information
  • RPAA registered PSP applications include Canadian place of business, dwelling house declaration, independent security confirmation, technical standard evidence, insurance or guarantee and integrity policy or good character information
  • Other entity applications include similar information plus descriptions of how they will meet specified duties, complaint procedures, external complaints body membership and estimated consumer numbers
  • RPAA registered PSPs and other entities must maintain place of business, insurance or guarantee and integrity or good character requirements after accreditation
  • The accreditation fee is $2,500 in the first year and then indexed to September CPI, rounded to the nearest $100, with no decrease from the previous year
  • An applicant has 30 days to request Governor review of an accreditation refusal, and the Governor has 120 days after giving an opportunity to make representations to accredit or confirm refusal
  • Participating entities requesting voluntary revocation must provide consumers with name and contact, planned request date, impact assessment, deletion notice and complaint resolution information
  • A participating entity has 30 days to request Governor review of a notice of intent to revoke accreditation, and the Governor has 60 days after giving an opportunity to make representations to revoke or withdraw the notice
  • Former participating entities must notify consumers of revocation date, reasons, impact, deletion request requirement and complaint process
  • Accredited third party service provider applications include legal information, activity description, participating entity relationships, Canadian place of business, independent security confirmation, technical standard evidence, contract and policy information and national security information
Implementation Applicants should build a complete accreditation evidence file before applying. That file should include corporate and governance documents, regulatory status, technical standard evidence, security confirmation, insurance or guarantee evidence, complaint process, designated officer details, integrity policy, national security information, contracts with participants where relevant and consumer impact notices for potential exit. RPAA registered PSPs should map which information can be reused from RPAA registration and which requirements are new under CDB.
Post-Consultation Watch
  • Whether final accreditation rules adopt the Privacy Commissioner’s recommendations for stronger evidence in selected pathways, including safeguards, complaints, authentication, dashboards, technical-standard compliance, insurance or guarantees and integrity checks
  • Whether the independent third party confirmation of security safeguards should have defined qualifications or assurance standards
  • Whether insurance or guarantee sufficiency needs guidance so applicants can price participation
  • Whether the dwelling house declaration could create unnecessary ambiguity for remote first firms
  • Whether refusal, revocation and review timelines are workable for firms planning launch and funding milestones
  • Whether ATPSP accreditation requirements are clear enough for infrastructure providers that will support multiple participating entities
NCFA Perspective Accreditation sets the practical threshold for market participation. If evidence requirements are too light, the framework risks weak trust. If they are too heavy, innovation may concentrate among large institutions and compliance funded platforms. The policy challenge is not choosing between safety and competition. It is designing entry rules that reward credible operators without making participation uneconomic for the firms most likely to create new consumer and SME products.

Authentication and Consent

Requirements The proposed rules connect data sharing to verification, consumer authentication and consent. A participant receiving a request must verify the requesting entity and confirm through the registry that it is an accredited participating entity and not suspended in a way that prevents receiving data. A participant requesting data must verify the provider and confirm through the registry that the provider is accredited and not suspended in a way that prevents providing data. Authentication requires confirmation of the consumer’s authentication information using multi factor authentication. The consumer must acknowledge the requesting participant’s name, the nature of the request and the accounts from which the requested data will be provided before the data is shared and the consumer is redirected.
  • Requester and provider verification against the registry before sharing
  • Confirmation that accreditation has not been suspended or restricted by Bank conditions
  • Multi factor authentication of the consumer’s authentication information
  • Consumer acknowledgement of the requesting entity, nature of the request and relevant accounts
  • Data sharing only after verification, authentication and acknowledgement requirements are met
  • Renewal may be required after circumstances where data sharing was not required or consent has not yet been renewed
  • Consent evidence must connect to records, deletion requests, liability, complaints and annual reporting
Implementation Participants need registry lookup, accreditation status checks, suspension condition logic, MFA, acknowledgement capture, consent evidence, renewal workflows, revocation and deletion links, exception handling and audit trails. Authentication and consent should not be built as a user interface layer only. They need to produce evidence that can support annual reporting, complaint resolution, breach response, liability allocation and supervisory review.
Post-Consultation Watch
  • Whether the registry verification workflow is operationally clear for real time data sharing
  • Whether MFA requirements align with existing bank and fintech authentication journeys
  • Whether consent and acknowledgement guidance makes the sharing scope sufficiently specific for consumers to understand what information is captured
  • Whether consent renewal triggers and failed renewal situations need clearer examples
  • Whether consumer dashboards, consent receipts and cross provider visibility should be addressed in guidance
  • Whether consent evidence is sufficient to resolve liability, complaint and deletion disputes
NCFA Perspective Consent is one of the highest trust points in the framework. The market will not fail because consent screens are hard to build. It will fail if consumers cannot understand them, if participants cannot prove what was authorized, or if revocation and deletion are too hard to execute. This is where compliance design and product design become the same problem.

Security

Requirements The regulations prescribe detailed security safeguards for participating entities. Safeguards include vulnerability identification and remediation, regular updates, secure default configuration, security software, robust authentication, access management policies, unique accounts, data encryption and backup, network security controls, external storage policy, bans on unauthorized devices and applications, network traffic monitoring, suspicious content controls, inventory of systems and devices, third party service provider contract protections, employee cyber threat training and an incident response plan with log auditing and periodic exercises based on extreme but plausible scenarios. Safeguards must be proportionate to data sensitivity and network segmentation is permitted. Federal and provincial financial institutions are presumed to have implemented safeguards unless OSFI or the relevant provincial authority has identified deficiencies and directed remediation.
  • Vulnerability management and regular updates
  • Secure configuration by default
  • Security software on relevant systems and devices
  • Robust authentication methods
  • Role based access management policies
  • Unique accounts and minimized shared accounts
  • Encryption and regular backup of stored data
  • Network security controls for data in transit
  • External storage policy
  • Prohibition on unauthorized devices and applications
  • Monitoring and control of network traffic
  • Suspicious content identification, quarantine or blocking
  • Inventory of systems and devices used for sharing and storing covered data
  • Contract terms requiring third party service provider protection of data
  • Employee cyber threat training and ongoing updates
  • Incident response plan with detection, response, recovery, log auditing and scenario exercises
  • Responsible officer or employee details must be provided to the Bank without delay after designation
  • Breach reports to the Bank must include circumstances, known cause, date or period, affected data, number of consumers, potential impacts, mitigation and contact information
Implementation Participants should treat security as an accreditation and operating evidence file. Required work includes asset inventory, vulnerability program, configuration standards, endpoint and system security, identity and access controls, encryption, backup, network monitoring, third party contract review, cloud and vendor risk, cyber training, incident response testing, breach reporting templates and escalation paths to the Bank. Security records should be aligned with annual reporting, complaint records and liability evidence.
Post-Consultation Watch
  • Whether final rules add the Privacy Commissioner’s recommended overarching requirement for safeguards appropriate to data sensitivity as technology and threats change
  • Whether independent third party confirmation should follow a defined assurance framework
  • Whether breach reporting timing, consumer notification thresholds and report updates need more prescriptive examples
  • Whether third party and cloud contract requirements should include subcontractor and data location obligations
  • Whether small entrants can meet the same security evidence burden without shared infrastructure
  • Whether fraud, identity, authentication and cyber controls should be addressed together in Bank guidance
NCFA Perspective Security is the trust anchor. Consumer driven banking exists partly to replace unsafe credential sharing with supervised data access. That only works if security is operationally real, not a paper control. The framework must be strong enough to protect consumers and flexible enough that security compliance does not become the reason only the largest organizations can participate.

Technical Standards

Requirements The technical standard provisions operate through the Act and the regulations. Applicants must provide evidence of compliance with the technical standard referred to in the Act. Participating entities must declare technical standard compliance in annual reports. Data sharing systems must meet response time expectations consistent with generally accepted international standards, maintain 99.5 percent monthly availability excluding planned outages, and use traffic management only for technical stability or security in a proportionate, non discriminatory way. The technical standards body must submit an annual report to the Bank within seven days after each anniversary of its designation order. That report must describe vulnerabilities in the technical standard or standards body that had or could have had an impact on the security of data sharing, non technical descriptions of changes to data fields, features, functionality or other security relevant aspects of the technical standard, rationale and decision process for those changes, and changes relevant to the body’s designation.
  • Applicants must provide technical standard compliance evidence
  • Participating entities must report annual technical standard compliance
  • API or electronic system response times must align with generally accepted international standards
  • Data sharing systems must meet 99.5 percent monthly availability, excluding planned outages
  • Rate limiting, throttling and preferencing are restricted to stability and security purposes
  • Traffic management must be proportionate, non discriminatory and must not degrade consumer outcomes
  • Technical standards body annual report is due within seven days after each designation anniversary
  • Technical standards body must report vulnerabilities, causes, impacts, mitigation and contact person
  • Technical standards body must describe changes to data fields, features, functionality or security relevant aspects, plus rationale and decision process
  • Technical standards body must describe changes relevant to its designation factors
Implementation Technical teams need API inventory, conformance evidence, performance monitoring, availability measurement, outage notification, traffic management governance, test environment planning, error handling, historical data readiness, change management and documentation that can support Bank supervision. Firms should prepare for technical standard versioning and for annual evidence that systems remained compliant through the reporting year.
Post-Consultation Watch
  • Whether the technical standards body should be identified or its governance clarified before final implementation planning
  • Whether conformance testing should be mandatory before production access
  • Whether response time expectations should be converted into measurable standards
  • Whether 99.5 percent availability is sufficient for higher value financial workflows
  • Whether public reporting of availability, outages and API performance would strengthen trust
  • Whether technical standard changes should have notice periods, backwards compatibility expectations and migration timelines
NCFA Perspective Technical standards are where the framework becomes real infrastructure. Canada’s competitive position will depend less on whether APIs exist and more on whether standards, testing, versioning and change management let participants build once and scale. Ambiguity here can turn regulatory permission into integration drag.

Liability

Requirements The liability provisions clarify consumer responsibility and the allocation of responsibility between participating entities. Every participating entity must inform consumers of the consequences of gross negligence or, in Quebec, gross fault in safeguarding authentication information. It must advise consumers of reasonable measures they can take to safeguard authentication information. It must not intentionally mislead consumers about the extent of their liability or adopt policies that presume consumer liability contrary to the Act. Where a consumer is not liable for a financial loss arising from loss, unauthorized access or unauthorized use of data shared under the Act, liability between participating entities is determined by where the loss, access or use occurred. The requester is liable to the extent it occurs in relation to the requester securely receiving or managing the data. The provider is liable to the extent it occurs in relation to provider authentication or secure provision of the data.
  • Consumers must be informed about gross negligence or gross fault consequences for authentication information
  • Consumers must be advised of reasonable safeguarding measures
  • Participants must not mislead consumers about liability
  • Participants must not adopt policies presuming consumer liability contrary to the Act
  • Requester liability follows failures connected to receiving or managing data
  • Provider liability follows failures connected to authenticating the consumer or securely providing data
  • Liability evidence depends on consent, authentication, registry checks, transmission logs, receipt records, complaint files and incident records
Implementation Participants should prepare consumer notices on authentication information, avoid default liability language, align customer support scripts with the Act, and preserve records that show where an event occurred. Liability operations require authentication logs, consent evidence, registry verification, data transmission records, receipt confirmations, access logs, incident investigations, complaint handling and remediation decisions.
Post-Consultation Watch
  • Whether gross negligence or gross fault communications will be understandable for consumers
  • Whether liability allocation is clear enough for multi party flows involving ATPSPs
  • Whether examples should clarify direct financial loss, unauthorized access, data loss and failed revocation
  • Whether consumer support and complaint processes need stronger alignment with liability rules
  • Whether records required to prove liability should be specified more explicitly
  • Whether fraud and scam scenarios are sufficiently covered by the liability architecture
NCFA Perspective Liability will be tested in edge cases, not in clean diagrams. The strategic issue is whether the framework can resolve consumer harm quickly without turning every incident into a multi party blame exercise. Clear evidence rules can build trust. Unclear responsibility can undermine adoption even if the technology works.

Reporting Requirements

Requirements The proposed regulations require change notices, annual reports and records sufficient to demonstrate compliance. Changes that must be reported include names or contact information, organizational structure, RPAA registration status for entities accredited under the RPAA pathway, Canadian regulatory oversight, foreign open banking registration or accreditation, designated officer contact, complaint contact, external complaints body membership, significant responsibility individuals and integrity status, insurance or guarantee sufficiency, technical standard compliance and national security information. Some changes must be reported within 30 days after they occur, some as soon as feasible after awareness, some at least 30 days before taking effect and some at least 60 days before taking effect. Annual reports must provide monthly metrics on non sharing events, express consents, consent renewals, withdrawals, deletion requests, system availability, data sharing counterparties, successful data provisions and average response time. They must also include changes, policy and procedure updates, breach summaries, planned and unplanned outages, technical standard declaration, financial metrics, supervisory deficiency declarations for financial institutions and security safeguard implementation descriptions for certain accredited entities. Records must be sufficient to demonstrate compliance, kept electronically in a format intelligible to the Bank, retained for five years after they cease to demonstrate current compliance unless otherwise specified, and protected against loss, destruction, falsification, inaccuracy and unauthorized access or use.
  • Notice of change categories cover identity, structure, registration, oversight, foreign accreditation, officers, complaints, EBC membership, significant responsibility individuals, insurance or guarantee, technical standard compliance and national security information
  • Notice timing includes 30 days after occurrence, as soon as feasible, at least 30 days before certain changes and at least 60 days before certain data storage or processing country changes
  • Annual report metrics include monthly non sharing counts and reasons
  • Annual report metrics include express consents, renewals, withdrawals and deletion requests
  • Annual report metrics include uptime, data sharing counterparties, delivery counts and average response time
  • Annual report must include changes, policy updates, breach summary, outages, technical compliance declaration and financial metrics
  • Records must demonstrate compliance with the Act and regulations
  • Records must be electronic and intelligible to the Bank
  • Records must generally be kept for five years after they cease to demonstrate current compliance
  • Records must be protected from loss, destruction, falsification, inaccuracies and unauthorized access or use
  • ATPSPs must keep compliance records, contracts with participants and policies or procedures relating to services they perform for participants, with the same electronic form and protection rules
  • Certain supervisory information, Bank directions, compliance agreements and supervisory correspondence are privileged for civil evidence purposes, with specified exceptions for use by the Minister, Governor, Bank, Attorney General of Canada, participants or ATPSPs in certain proceedings
Implementation Participants need a compliance data model that captures events as they happen. Manual annual reporting will be fragile. Systems should collect consent events, renewal events, withdrawal events, deletion requests, non sharing reasons, uptime, response time, outage data, breaches, policy changes, material changes, complaint records and financial metrics. Record retention and protection should be built into the architecture before production data flows begin.
Post-Consultation Watch
  • Whether the notice timing categories are clear enough for operational teams to apply consistently
  • Whether annual reporting should align with RPAA and other Bank of Canada reporting regimes where possible
  • Whether public transparency reporting on uptime, outages, complaints and non sharing events would strengthen trust
  • Whether smaller firms need proportional reporting without weakening supervisory visibility
  • Whether five year record retention is practical across all evidence categories
  • Whether privileged supervisory information rules strike the right balance between supervision, litigation risk and transparency
NCFA Perspective Reporting and records are the hidden operating system of regulated open banking. They may matter more than any single product feature because they determine whether trust can be audited, problems can be reconstructed and smaller firms can participate without building a bank sized compliance department.

Complaints

Requirements The regulations require complaint handling information at accreditation and connect complaints to revocation notices, consumer contact information, external complaints body membership and records. Other entity applicants must describe intended complaint procedures, the officers or employees to be designated for complaint responsibilities, and the contact information consumers will use. A participating entity requesting revocation or a former participating entity whose accreditation has been revoked must provide consumers with information about the process for resolving outstanding complaints. Annual reporting must describe changes to complaint related procedures. Record keeping must support compliance and complaint evidence. ATPSPs must keep contracts and related policies or procedures where they perform activities for participating entities.
  • Complaint contact information is required in accreditation applications
  • Other entity applications must describe complaint procedures and designated complaint roles
  • External complaints body membership status is required for certain applicants
  • Revocation and former participant notices must include complaint resolution information
  • Complaint processes connect to annual reporting and record keeping
  • Complaint evidence should align with consent, authentication, data sharing, security, breach and liability records
Implementation Participants should design complaint intake, triage, escalation, evidence review, consumer communication, external complaints body routing, remediation, root cause analysis and reporting. Complaint workflows should identify whether the issue relates to access, failed sharing, revoked consent, deletion, fraud, data quality, breach, liability or service availability.
Post-Consultation Watch
  • Whether complaint timelines and escalation expectations should be more explicit
  • Whether consumers will know whether to contact the provider, requester, ATPSP, bank or external complaints body
  • Whether SMEs need distinct complaint pathways for business account use cases
  • Whether complaint data should feed into supervisory or public transparency reporting
  • Whether complaints involving data quality, failed sharing, deletion or fraud require specific treatment
NCFA Perspective Complaint handling will be a public trust signal. Consumers rarely judge infrastructure by how it works on a perfect day. They judge it by what happens when something breaks, money is lost, access fails or nobody knows who is responsible.

National Security Review

Requirements The regulations prescribe extensive information for national security review and timelines for Ministerial decisions. Applicants must provide information about legal name, trade names, jurisdictions, addresses, contact information, business activities, financial services, affiliates, ownership and control, individuals or entities with significant voting or ownership interests, board members, highly compensated senior officers, major creditors, state owned enterprise ownership or appointment powers, categories of personal or financial information gathered or planned to be gathered, countries where the applicant or third party service providers store or process that information, and individuals or entities outside employees or agents that may receive access to that information. The Minister has 60 days after receiving the application copy to decide whether to review, with extensions in 60 day periods. If a review proceeds, the Minister has 180 days, with 180 day extensions. Applicants have 30 days to request review of a directive to refuse accreditation. Applicants must provide requested additional information within 30 days. For suspension and revocation, participants or ATPSPs have 30 days to request review of a notice of the Minister’s intent to direct revocation. Former participants and former ATPSPs must provide specified information to consumers or participating entities. Additional information requested by the Bank must be provided within 15 days.
  • Ownership, control, affiliates, significant influence and voting or ownership interest information
  • Countries of residence, citizenship, incorporation or formation for relevant individuals and entities
  • Board member and five most highly compensated senior officer information
  • Five largest creditors and credit agreement terms
  • State owned enterprise ownership, voting interest or appointment powers
  • Categories of personal and financial information gathered or planned, including identifying information, financial data, private communications and geolocation data
  • Countries where applicant or third party service providers store or process information
  • Non employee or non agent individuals or entities that may access the information
  • 60 day Ministerial decision window to review, extendable by 60 day periods
  • 180 day national security review period, extendable by 180 day periods
  • 30 day applicant review request period for refusal directive
  • 30 day period to provide additional requested information under subsection 54(2)
  • 30 day review request period for notice of intent to direct revocation
  • 15 day period to provide additional information requested by the Bank under subsection 71(2)
Implementation Applicants should prepare a national security file before applying, not after questions arrive. That file should include ownership charts, control analysis, citizenship and residency information, affiliates, creditors, SOE exposure, data categories, data storage and processing locations, cloud and vendor access, third party access, board and senior officer information, and change monitoring. Deal teams should assess how fundraising, acquisitions, data residency, vendor changes and cross border processing could affect review risk.
Post-Consultation Watch
  • Whether the national security information package is proportionate for lower risk applicants
  • Whether significant influence, creditor exposure and third party access require clearer guidance
  • Whether data residency and cross border processing expectations should be clarified before applications begin
  • Whether the 60 day and 180 day review timelines could materially affect investment, partnership and launch planning
  • Whether applicants should have a pre filing process or informal guidance pathway for complex ownership structures
  • Whether national security review should be harmonized with broader financial infrastructure, digital identity and cloud risk policy
NCFA Perspective This connects open banking to financial infrastructure security. It is not a side process. National security review can affect who enters the market, which investors participate, where data is processed, which vendors are acceptable and how exits are structured. If handled clearly, it can strengthen trust. If handled opaquely, it can slow capital and partnership formation.

Assessments and Fees

Requirements The regulations set an indexed accreditation fee and annual assessments. The accreditation fee is $2,500 in the year the section comes into force. In later years it is calculated as $2,500 multiplied by the ratio of the September all items CPI for Canada in the year before application to the September CPI in the year the section comes into force, rounded to the nearest $100, with no decrease from the previous year. Participating entity assessments are calculated as base assessment plus variable assessment minus interim assessments. Base assessments depend on total asset value. Entities with at least $1 trillion in assets pay a $150,000 base amount; $100 billion to under $1 trillion pay $100,000; $10 billion to under $100 billion pay $50,000; $1 billion to under $10 billion pay $20,000; and under $1 billion pay $10,000. Variable assessment shares allocate remaining Bank costs after deductions by asset tier using 0.4, 0.3, 0.2 and 0.1 factors for the larger asset tiers, while the under $1 billion category has no variable amount. Subsidiary assets are excluded where the subsidiary is itself a participating entity. ATPSPs are assessed $10,000 per year less interim assessments. The external complaints body is assessed $50,000 per year less interim assessments, reduced proportionally for a partial year. Information requested about assets must be provided by March 31 following the relevant calendar year when requested by December 31, or within 15 days for other requests. If asset information is not provided on time, the entity is treated as being in the highest asset category for assessment purposes.
  • $2,500 first year accreditation fee
  • CPI indexed accreditation fee after first year, rounded to nearest $100 and not allowed to decrease
  • Participating entity assessment equals base assessment plus variable assessment minus interim assessment
  • Base assessment tiers of $150,000, $100,000, $50,000, $20,000 and $10,000 based on total assets
  • Variable assessment shares of 0.4, 0.3, 0.2 and 0.1 for larger asset tiers
  • No variable assessment for entities with less than $1 billion in assets
  • ATPSP annual assessment of $10,000 less interim assessments
  • External complaints body annual assessment of $50,000 less interim assessments, prorated for partial year designation
  • Asset information deadline of March 31 in specified cases and 15 days in other cases
  • Failure to provide asset information can result in assessment as if the entity were in the highest asset category
Implementation Participants should model accreditation fees, annual assessment tier, possible variable assessment, interim assessments, ATPSP fees, external complaints body implications, insurance or guarantee costs, technical build, security assurance, reporting systems and compliance staffing. Smaller firms should assess whether direct participation, ATPSP services, partnership or staged entry creates a viable cost structure.
Post-Consultation Watch
  • Whether the base assessment tiers are proportionate for mid sized and smaller participants
  • Whether the zero variable assessment for under $1 billion firms is enough to support competition
  • Whether ATPSP fixed fees support shared infrastructure economics
  • Whether asset based assessment is the right proxy for supervisory cost or market impact
  • Whether fee predictability is sufficient for early entrants and investors
  • Whether the highest tier default for missing asset information is too punitive or necessary for compliance discipline
NCFA Perspective The fee schedule is only one part of participation cost. The strategic issue is total regulatory operating cost. If cost scales poorly, Canada could see a market where participation is open in law but concentrated in practice. Shared infrastructure, clear guidance and proportionate reporting may determine whether smaller innovators can enter.

Administrative Monetary Penalties

Requirements The regulations designate violations for contraventions of a long list of Act provisions, specified regulation provisions, non compliance with compliance agreements and non compliance with Bank directions. The designated Act provisions include obligations related to accreditation, suspension conditions, former entity notices, ATPSP activities, prescribed information, data sharing, use of registry, privacy, security, designated officer, breach reporting, authentication, consent, deletion, notices, liability, complaints, records, technical standards, reporting, Bank information requests and other framework duties. The designated regulation provisions include failure to notify another participating entity of non sharing reasons, data sharing service standards, responsible officer information, specified reporting and notice provisions, record keeping provisions and ATPSP record keeping provisions. The Act provides maximum penalties of up to $1 million for individuals and up to $10 million for participating entities or ATPSPs.
  • Contraventions of numerous Act provisions are designated as violations
  • Contraventions of selected regulation provisions are designated as violations
  • Non compliance with compliance agreements is designated as a violation
  • Non compliance with specified Bank directions is designated as a violation
  • Regulation violations include non sharing notice failures, service standard failures, officer reporting failures, notice failures, annual reporting failures and record keeping failures
  • Maximum penalty of $1 million for individuals
  • Maximum penalty of $10 million for participating entities or ATPSPs
  • Penalty exposure connects to accreditation, data sharing, registry use, privacy, security, breach reporting, authentication, consent, deletion, liability, complaints, technical standards, reporting, records and Bank information requests
  • Coming into force is staged by Act sections, with most regulations coming into force when section 44 of the Act comes into force, data sharing and many operational obligations when section 76 comes into force, and assessment provisions when section 140 comes into force
Implementation Participants should map every designated violation to an internal control, evidence record and accountable owner. Enforcement readiness should cover consent, registry checks, non sharing notices, uptime, breach reporting, annual reporting, records, complaints, officer information, Bank information requests, compliance agreements and directions. Boards and senior leaders should understand which failures create individual or organizational exposure.
Post-Consultation Watch
  • Whether violation categories are clear enough for participants to map controls before launch
  • Whether penalty exposure is proportionate across firms of different size and role
  • Whether remediation and self reporting should affect penalty treatment
  • Whether public enforcement disclosure will be used to strengthen market discipline
  • Whether staged coming into force gives firms enough time to build controls before penalties apply
  • Whether individual exposure could affect senior officer recruitment and governance design
NCFA Perspective Penalty risk is less about the headline maximum and more about whether an organization can prove it had controls, records and remediation processes in place before something went wrong. Enforcement should strengthen trust without chilling responsible innovation. That balance will matter as Canada tries to turn regulatory credibility into market adoption.

Related NCFA Intelligence

Open Banking in Canada Opportunity BriefCommercial opportunity layer connected to this regulatory guide Open the brief
Financial Innovation MapWhere consumer driven banking fits in the broader fintech innovation ecosystem View the map
Research LibrarySupporting reports, market evidence and policy research Research library
Fraud regulatory perspectiveTrust, fraud controls and consumer protection context for Canada’s open banking strategy Read the fraud perspective

From Regulation to Opportunity

Canada’s proposed Consumer Driven Banking Regulations create readiness questions across accreditation, consent, data scope, APIs, cybersecurity, reporting, liability, supervision, national security review and enforcement. NCFA tracks commercial opportunities separately in the Open Banking in Canada Opportunity Brief, where regulatory evidence connects to product opportunities, investment themes, implementation gaps and emerging market signals.

Open the Opportunity Brief


NCFA Jan 2018 resizeThe National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org

NCFA Financial Innovation MapNCFA Innovation Opportunity BriefsNCFA Fintech Insights

NCFA Fintech WhispererNCFA Fintech Fridays PodcastNCFA Weekly Newsletter