





Karsten Wenzlaff, Advisor
August 26th, 2025
Karsten Wenzlaff is a Crowdfunding and Fintech Expert from Germany. He is Secretary-General of Digit[...]


September 7, 2026 | NCFA Insight | Digital Identity Privacy KYC AML ATF, Regtech Compliance Governance, Legal Issues Regulation Consultation
On September 4, 2026, reporting by CBC and the Centre for Information Resilience linked Maple Digital Financial Solutions to the sanctioned TGR network through corporate, personnel and digital connections. Maple is a Vancouver based money services business registered with FINTRAC and offers international payments, foreign exchange and virtual currency services. There is no finding that Maple itself laundered money.
The reporting points to overlapping directors, shared contact information, archived websites and other digital traces connecting Maple and The OneGate with TGR related entities. Former Maple director Andrejs Carenoks (also known as Andrejs Bradens) was sanctioned by the United States in 2024 for his alleged role in TGR. Maple director Janis Zvigulis has also served as a director of The OneGate and TGR Wealth Solutions in the United Kingdom. Zvigulis has not been identified as personally sanctioned.
“FINTRAC registration confirms that an MSB operates within Canada’s anti money laundering regime. It does not mean the business is licensed, endorsed or free of risk.”
FINTRAC says this plainly in its Money Services Business Registry. Registration means a business has satisfied the legal requirement to register. FINTRAC does not license or endorse the firms listed there.
Registration still comes with real obligations. MSBs must verify clients, keep records, report certain transactions and maintain a compliance program. FINTRAC can examine firms, impose penalties and revoke registrations when legal requirements are not met.
As of March 31, 2025, FINTRAC listed 2,778 registered MSBs. During 2024 to 2025, 509 new MSBs registered, 351 renewed, 198 ceased their registrations and 12 registrations were revoked.
The CIR investigation into The OneGate found an international payments network spanning at least seven jurisdictions and reported strong open source evidence connecting it to TGR. The OneGate's U.S. company was registered to the same Vancouver address as Maple Digital Financial Solutions.
The U.S. Treasury sanctioned Carenoks in December 2024 and identified TGR Partners and TGR Wealth Solutions among entities connected to the network. Treasury described TGR as an international illicit finance network used for sanctions evasion and money laundering involving digital assets.
Those links do not establish that Maple committed money laundering. They do explain why checking a FINTRAC number alone is not enough for a bank, payment company, fintech or corporate customer deciding whether to enter or continue a financial relationship.
Canada's 2025 National Risk Assessment identifies professional money launderers, transnational criminal networks, crypto assets and some types of MSBs among the areas with high money laundering exposure. The report says Canada's MSB sector includes nearly 3,000 businesses with very different products, customers and risk profiles.
For a fintech or bank, an active registration should be one check among several. Directors, owners, related companies, sanctions exposure, jurisdictions, payment partners and the firm's operating history can tell a very different story from the registry entry alone. Those checks also need to continue after onboarding because ownership, counterparties and sanctions status can change.
Canada has recently made it easier for reporting entities to compare what they are seeing. FINTRAC information sharing rules introduced in June allow eligible firms to exchange designated information for detecting money laundering, terrorist financing and sanctions evasion, subject to privacy requirements. That gives banks, payment firms and fintechs another way to spot connections that may be difficult to see inside a single customer file.
FINTRAC itself tells consumers to research an MSB before using it and says it cannot provide information about a firm beyond what appears in the public registry. That leaves customers and commercial counterparties with their own decision to make. Registration confirms legal status inside the AML regime, while trust still depends on who controls the business, who it deals with and what those relationships reveal.
How much should an active FINTRAC registration influence whether you trust an MSB?
 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
 |  |  |
|---|---|---|
 |  |  |
September 4, 2026 | NCFA Insight | Digital Identity And Trust, Digital Assets Blockchain And Tokenization, Regulation And Policy
On August 10, 2026, ICANN opened a consultation on alternative naming systems that could affect how blockchain based and other naming systems work alongside the global Domain Name System. Comments are open until September 21, 2026 at 23:59 UTC.
ICANN is the nonprofit organization that coordinates the global Domain Name System, including the rules for top level domains such as .com, .org and newer gTLDs. The consultation matters most to domain registries, Web3 naming providers, digital identity firms, wallet and payment companies, cybersecurity specialists and brands that could be affected if the same name appears across multiple naming systems.
ICANN is dealing with a problem that did not exist when the DNS was designed. Alternative naming systems can create names outside the global DNS, while registry operators and potential applicants in the 2026 New gTLD Program are now interested in using some of the same top level strings in both systems. If that happens, users need confidence that the same name is controlled by the same party wherever they encounter it.
ICANN has not approved a general integration model. Its Technical Study Group is testing whether the same gTLD string can operate in both the DNS and an alternative naming system without creating unacceptable security or stability problems. The current consultation asks whether the proposed technical requirements are strong enough.
The report focuses on what ICANN calls string+controller integration. In plain language, if the same name appears in both systems, the same party should control it in both. That relationship also has to remain intact when names are registered, transferred, suspended, expire or change hands.
That becomes especially important when a name is used for identity, wallets, payments or other digital services. A human readable name only helps if users can trust who is behind it. If control changes in one system but not the other, the same looking name could point to different parties.
For fintech and digital asset firms, the risk is less about domain mechanics and more about mistaken identity. A wallet name, payment identifier or digital identity and authorization system can become easier to use, but also easier to misunderstand if two systems recognize the same string without keeping ownership aligned.
Several registry operators and potential 2026 round applicants have already asked ICANN about this kind of integration. Reviewing similar technical questions one application at a time could become expensive and slow, particularly when requests are referred for additional technical review.
The Technical Study Group was created to develop common requirements that future applicants could work from. That would not guarantee approval, but it could make the process more predictable for registries deciding whether to build services that connect conventional domains with alternative naming systems.
The consultation also comes before another policy step. ICANN says proposed registry agreement language related to these services will be published for a separate public consultation. Comments submitted now can still affect the technical work before those contractual terms are finalized.
For domain registries, Web3 naming providers, digital identity firms, cybersecurity specialists, wallet providers and affected brands, the practical questions are already clear.
Should the same party always control both versions of a name? What happens if ownership changes in only one system? And what safeguards are needed so users can tell who they are actually dealing with?
Comments close September 21, 2026 at 23:59 UTC. Affected stakeholders can submit input directly to ICANN before the deadline.
Can the same name work across two systems without creating confusion over who controls it?
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Sep 3, 2026
Anyone who has onboarded a client at a fintech startup knows the bottleneck. The product works, the API integration is done, and then someone emails a photo of a passport taken at an angle in bad light, with half the machine-readable zone cut off. Multiply that by fifty applicants a week and your compliance queue turns into a photo-editing job.
Small lenders, brokerages and crypto exchanges all hit the same wall. Identity verification and record-keeping are document-heavy by law, and the documents arrive in whatever format the customer's phone produced.
That is the gap a mobile scanner fills. OKEN, listed on the Play Store under the longer name OKEN - camscanner, pdf scanner and published under the name CAMBYTE Pte. Ltd., is a Productivity app that turns a phone camera into a document scanner with edge detection, OCR text recognition, and export to PDF, JPG, Word or TXT. It also reads QR codes, which matters more than it sounds in a payments context.
The core loop is straightforward. Point the camera at a page, let the app find the borders, and it flattens the perspective into something that looks like it came off a flatbed scanner rather than a kitchen table.
OCR is where the finance use case gets interesting. A scanned invoice or ID page that carries a searchable text layer can be indexed, queried and pulled up during an audit without anyone flipping through image files. A scan without OCR is just a picture of information.
The format range is the practical part for anyone assembling a client file:
The store listing pitches it at students and small business people, accountants, realtors and managers. That is a fair description of who benefits most: teams too small to own scanning hardware but still accountable for the same paper trail as the big institutions.
Phone scanning is fine for capture. It stops being fine at the point where you have thirty scanned pages sitting on a handset and a Windows machine holding your CRM, your case management system, and the shared drive your auditor actually looks at.
That handoff moment is usually why people start looking at OKEN scanner for PC rather than sticking with the phone alone. On a desktop, the app runs inside an Android emulator, and the exported PDFs land somewhere your other software can reach.
Most emulator advice is generic. For a scanner app, only a couple of things really change the experience.
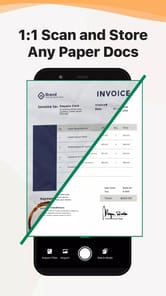
Batch OCR is noticeably more comfortable on a large monitor. Correcting a misread account number in a recognized text layer is tedious on a 6-inch screen and fast with a keyboard.
Treat the app as capture and formatting, not as verification. OKEN produces a clean, readable, searchable document. It does not authenticate an identity document, check it against a sanctions list, or satisfy any regulator on its own.
For internal paperwork, supplier invoices, signed agreements and expense records, that distinction barely matters. For customer identity files it matters a great deal, and the scanner should sit in front of a proper verification provider rather than in place of one.
One caveat worth carrying away: scanned identity documents are among the most sensitive files a small firm will ever hold. If you run the app on a shared office desktop through an emulator, the exported PDFs live in a Windows folder that anyone with access to that machine can open. Decide who that is before the first scan, not after.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Aug 31, 2026
Anyone who moves money online eventually thinks about the network they are moving it over. Public Wi-Fi at a co-working space, a hotel connection during a conference, a café network shared with fifty strangers: all of these sit between your device and whatever platform holds your funds. Lets VPN, listed on app stores as "Lets VPN - The VPN that Always Connects" and published under the name LetsGo Network, is one of the tools people reach for in those moments.
It is a Tools-category app with a narrow job. It routes your traffic through a server you pick, encrypts it in transit, and does so without asking who you are.
The pitch from the developers is short. Unlimited data on every monthly plan, no registration and no personal information required, a free download, and a list of servers you choose from yourself rather than being auto-assigned to whatever the app thinks is closest.
That second point matters more than it looks in a fintech context. Most VPN services want an account, which means an email address, sometimes a phone number, and a billing record that ties your identity to your connection history. Lets VPN's stated approach skips the registration step entirely, which shrinks the amount of data any single party holds about you.
The manual server picker deserves a second look too. If you are connecting to a banking portal or an exchange that flags logins from unexpected regions, being able to pick a consistent server yourself avoids the whack-a-mole of geographic fraud alerts.
The obvious audience is the traveller. Founders on the road, contractors billing across borders, anyone checking a payments dashboard from an airport lounge.
Then there is the small business owner running operations from a laptop and a phone with no IT department behind them. A one-person consultancy handling client invoices does not have a corporate VPN concentrator to dial into. A consumer-grade tool that connects reliably and does not require ongoing administration fills that gap reasonably well.
Crypto and web3 users form a third group, often for reasons that have less to do with secrecy than with network hygiene. Wallet interfaces, node dashboards and DeFi front-ends are frequent phishing targets, and reducing exposure on untrusted networks is basic practice.
A caveat before going further: a VPN encrypts transport. It does not authenticate you, it does not protect a compromised device, and it will not save you from approving a malicious transaction. Treat it as one layer, not a security posture.
Financial work happens on big screens. Spreadsheets, treasury dashboards, tax software, three browser tabs of reconciliation. If your VPN only runs on a phone, your protected session and your actual work session are on different devices.
There is also a workflow problem. Toggling a connection on a phone while reading a compliance document on a monitor is friction, and friction is why people skip the security step. Having the connection control in the same place as the work makes it more likely to be used.
Lets VPN is distributed as an Android app, so running it on Windows means running Android on Windows.
An Android emulator creates a virtual Android environment on your PC, and Lets VPN behaves inside it much as it would on a handset. BlueStacks is the usual starting point for people who have never done this before. Users who want something lighter on system resources sometimes prefer LDPlayer instead.
Two things specific to this app are worth getting right.
First, the VPN tunnel inside an emulator generally protects traffic from apps running inside that emulator, not your host Windows browser. If your goal is protecting your everyday desktop browsing, verify what is being routed before you assume you are covered. Some emulator configurations share the host network stack in ways that make this behave differently than you expect.
Second, when the app asks for VPN permission on first launch, that dialog comes from Android's own permission layer, not from the app. Granting it inside the emulator is required for the tunnel to establish at all, and denying it by reflex is the most common reason people report the connection failing on desktop.
That is largely why people look up Lets VPN download for PC instead of just running the phone version: checking two or three servers for latency before committing is a task that takes five minutes on a monitor with a speed test tab open, and considerably longer squinting at a phone screen.
Multitasking is the real difference. Switching servers mid-session on mobile means leaving whatever you were doing; on desktop it is a window you alt-tab to.
For a business, personal VPN tools sit in an awkward spot. They are useful and they are also invisible to whoever is responsible for security oversight.
If your team handles customer financial data, a consumer app installed on individual laptops through an emulator is not an audit-friendly answer. It works for a solo operator or a founder in transit. It does not substitute for a managed solution with logging, device policy and revocation when someone leaves.
Ask yourself which of those two situations you are in before standardising on anything.
Free tiers and paid plans on VPN apps change, and the store description's mention of unlimited data applies to monthly plans specifically, so check current terms rather than assuming.
The more durable caveat is trust. Routing traffic through a VPN moves your visibility from your internet provider to the VPN operator, and a no-registration policy tells you about data collected at signup, not about what happens at the server. That trade is often worth making on hotel Wi-Fi. It is a different calculation for something you leave running all day on a machine that touches client money.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
August 28, 2026 | NCFA Insight | Open Banking Open Finance And Data Sharing, Digital Identity And Trust, Risk Compliance And Regtech, Cybersecurity And Fraud
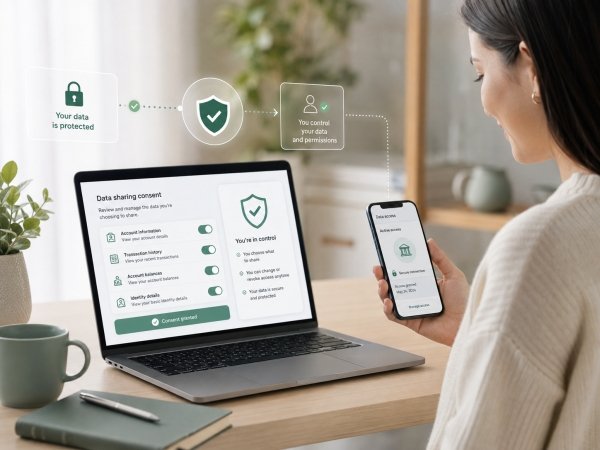
On August 26, 2026, Canada’s Office of the Privacy Commissioner (OPC) called for five changes to Canada’s proposed Consumer-Driven Banking Regulations including what financial data can be shared, what firms must prove before accreditation, when public data can be reused without consent, how security keeps pace with new threats, and how the Bank of Canada and Privacy Commissioner coordinate oversight.
The submission arrived on the last day of the government's 60-day consultation, which closed August 26. Finance Canada now has to decide which recommendations make it into the final regulations before Canada's open banking system starts moving from rulemaking into accreditation and implementation.
The Commissioner supports consumer-directed data sharing, multi-factor authentication and mandatory breach reporting to the Bank of Canada. The five requested changes go further and could affect compliance costs, product design, consumer trust and which fintechs can afford to participate.
The proposed regulations cover identity information, account identifiers, fees and terms, balances, transactions and information about financial products. The OPC says those categories aren't detailed enough for consumers to know exactly what information they are agreeing to share and points to Australia’s Consumer Data Right as a more precise model.
It's important when someone is looking at a consent screen. "Identity data" doesn't tell a customer whether a provider will receive a name, address, email, phone number or other information.
The issue becomes more important as firms combine bank data with other sources and use it for credit, fraud, pricing or financial recommendations. Open banking decision intelligence becomes more valuable as firms infer more from permissioned financial data, which makes precision about what was actually shared even more important.
If Canada wants meaningful consent, people need to know what is leaving their bank before they approve it.
The proposed rules offer four accreditation routes under Bank of Canada oversight, including streamlined treatment for payment service providers already registered under the Retail Payment Activities Act. The OPC wants stronger proof from some applicants, including evidence that security controls are working, technical standards are being met and authentication and complaint processes are ready.
It also wants certain financial institutions to show that people responsible for consumer-driven banking have been assessed for good character and integrity, and that insurance or other guarantees are available to manage data-related risks.
That raises the accreditation bar for good reason. Accredited firms may receive account identifiers, balances, transaction histories and other highly sensitive information. The commercial question now is how much proof Canada requires and what it costs credible firms to provide it.
Finance Canada estimates the proposed regulations will generate C$13.2 billion in benefits over ten years while adding about C$457.7 million in regulatory costs. Under the government's central scenario, roughly 680 businesses participate initially, including 578 small businesses, with an estimated average annualized regulatory cost of C$89,133 for each small business.
Large financial institutions can spread fixed security, legal and reporting costs across millions of customers. Smaller fintechs can't. Canada needs to keep poorly prepared firms away from consumer financial data without making the cost of proving readiness another advantage for incumbents.
The OPC also wants Finance Canada to narrow an exception that allows some publicly available information to be used without consent. Its recommendation is that public data should not include information where a consumer still has a reasonable expectation of privacy.
Information can technically be public without someone expecting it to be collected, combined with financial records and reused inside a commercial service. Open banking makes those combinations easier and potentially more valuable.
The final rules therefore need to protect against a consent loophole where one piece of public information becomes a reason to use financial information in ways the customer didn't reasonably expect.
The proposed regulations already require vulnerability management, authentication, encryption, network protection, employee training and tested incident-response plans, with those controls applied in proportion to the sensitivity of the data. The OPC wants an additional obligation requiring firms to keep those safeguards appropriate as technology and cyber risks evolve.
That's certainly more demanding than completing a checklist once. After a breach, a firm could still have to show that its security was appropriate for the data it held and the risks it should reasonably have been managing.
For banks and fintechs, security readiness therefore becomes an ongoing operating requirement. Canada's proposed open banking requirements already span accreditation, authentication, security, technical standards, liability, complaints and Bank of Canada supervision. Companies preparing to participate need proof that those controls actually work, not just policies saying they exist.
The Bank of Canada will supervise consumer-driven banking participants while the Privacy Commissioner continues to oversee federal private-sector privacy obligations. A serious data breach can involve both, so the OPC wants explicit authority for the regulators to coordinate their work and share information where necessary.
Without that, companies can face overlapping requests and investigations while an important issue still falls between mandates. When customer data is exposed, management needs to know who must be notified, what each regulator expects and how the two authorities will divide the work.
Clear coordination is especially important because Canada is trying to replace a system millions of people already use. Finance Canada estimates roughly nine million Canadians currently rely on financial-data services using credential-based screen scraping. Regulated API access should reduce important security and liability risks, but only if supervision works cleanly when something goes wrong.
The OPC is asking Finance Canada to be more precise about what data moves, who can receive it and what firms must prove before they get access. Those protections however cost money. Independent security work, technical compliance, authentication, insurance, reporting and complaint processes all consume capital that a younger company could otherwise spend on product development, hiring or customer acquisition.
The answer isn't weaker safeguards. Financial transaction data is too sensitive for that. The challenge is to determine whether each requirement addresses a real risk and whether the cost is proportionate to the firm, activity and data involved.
Canada's C$13.2 billion benefit estimate assumes firms enter the market and build services people want to use. Open banking opportunities in Canada already span verification, cash-flow tools, SME services, financial management and future payment initiation, but APIs alone won't create competition.
Consumers need providers they trust, and credible challengers need a realistic way to qualify. The final rules will help decide both.
How high can Canada raise the privacy and security bar for open banking before the cost of clearing it starts protecting incumbents from the competition the system is supposed to create?
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
The Privacy Commissioner wants clearer rules in five areas: exactly what financial data can be shared, what firms must prove before accreditation, when publicly available data can be used without consent, how security safeguards should keep pace with changing threats, and how the Bank of Canada and Privacy Commissioner coordinate oversight.
No. The 60-day consultation on the proposed Consumer-Driven Banking Regulations closed on August 26, 2026. Finance Canada now has to decide what changes to make before the regulations are finalized.
Yes. Stronger accreditation, security, insurance and compliance requirements can improve consumer trust and keep poorly prepared firms out, but they also raise the cost of participation. The challenge is setting a high enough bar to protect financial data without making open banking too expensive for credible smaller fintechs to enter.
| | |
|---|---|---|
| | |
August 25, 2026 | NCFA Insight | Digital Identity And Trust, Cybersecurity Fraud And Financial Crime, Risk Compliance And Regtech
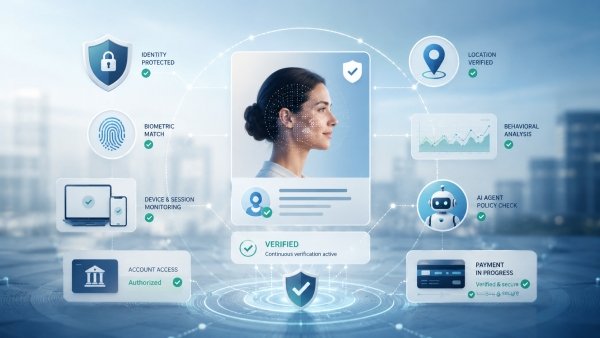
On August 25, 2026, Vancouver based Fobi AI launched Fobi AltID 3.0, expanding its digital identity technology beyond credential verification. Fobi says the new platform can continuously authenticate a verified person, confirm authorization and use satellite positioning to add location and time to the decision. Financial services and customer identity checks are among its intended uses.
The existing Fobi digital identity wallet focuses on proving identity or age while limiting how much personal information needs to be shared. The new proposition goes further. Once someone has been verified, Fobi wants the credential to keep helping organizations decide whether the right person is still present and allowed to complete an action.
That addresses a real financial control problem. Verifying someone when an account is opened does not prove that the same person still controls a session months later, approved a particular payment or gave software permission to act for them. The gap gets wider as financial services automate more activity.
The launch names financial services as a target market but doesn't identify a bank, credit union, payment company or financial pilot. It also doesn't explain how an AI agent would be given, restricted or stripped of authority. Those are important boundaries between the product Fobi has launched and the larger trust infrastructure it wants to build.
This approach already has support in established digital identity practice. NIST continuous authentication guidance allows organizations to monitor characteristics such as behaviour, device information, location, timing and network activity after a user has logged in. Suspicious changes can trigger another identity check or end the session.
For financial firms, that can add protection without repeatedly asking customers to upload identity documents. An account can remain usable while the service watches for changes that make the current activity look less like the person who was originally authenticated.
Fobi adds location to that decision. The company says satellite positioning can connect a verified person with where and when an interaction occurs. Location can strengthen a risk decision, but Fobi has not disclosed the positioning technology, accuracy or protections against false location data. NIST also treats geolocation as one piece of a wider risk assessment rather than proof of identity on its own.
More monitoring also creates more privacy responsibility. Behaviour, devices and location can all reveal sensitive information. NIST requires those uses to be included in privacy risk assessments. Fobi says the personal information used for the original verification can be removed from the ongoing process, but further disclosure is needed to show what the platform continues to observe and retain.
Canada is dealing with the same combination of identity, consent and security as financial data becomes easier to share. The proposed Canada Open Banking and Consumer Driven Banking Rules bring authentication, consumer permission, security and evidence of authorization into the same operating framework. Persistent digital identity becomes more useful when those controls have to work after onboarding rather than only at the beginning of the relationship.
AI agents make the distinction between identity and authority easier to see. A bank may know who owns an account and still need to know whether software has permission to spend $500, change an instruction or continue acting tomorrow. AI agents with wallet access increases the urgency of defining what software can do, for how long and on whose authority.
Payment networks are already building controls around that problem. The Visa Trusted Agent Protocol lets merchants verify that an AI agent is legitimate and has permission to act for a customer. Visa's specifications also allow merchants to limit an agent to a specific purpose, such as browsing or making a payment.
Mastercard Verifiable Intent, developed with Google, records what a person authorized before an AI agent acts. Mastercard is designing it to work across wallets, platforms, payment networks and different agent systems.
The same convergence appears in the FCA Emerging Technology Horizon Scan 2026, where digital identity, AI agents, consumer control and programmable finance intersect. For fintechs, the opportunity goes beyond proving who somebody is toward proving what a person or piece of software is allowed to do.
Open digital credentials could make those permissions easier to carry between services. The W3C digital credential standard provides a common way to issue and verify secure, privacy respecting credentials. Fobi has not disclosed whether its new platform supports that standard or another open identity framework. Interoperability is necessary if the technology is expected to work across banks, fintechs, payment networks and other organizations rather than mainly inside Fobi's own products.
Fobi is also positioning post quantum security as part of the platform. Financial firms are already preparing for post quantum cryptography as new security standards replace encryption that future quantum computers could threaten. Fobi has not identified which algorithms or standards it uses, or provided independent technical validation. For now, quantum readiness remains a product claim that still needs evidence rather than the main reason to assess the launch.
The more immediate opportunity is digital trust. Identity can establish the person. Ongoing authentication can flag when something changes. Authorization can control what a person or AI agent is allowed to do. Those capabilities also connect digital identity, cybersecurity and automated finance across the Financial Innovation Map.
Fobi now has to prove that its technology can join those pieces in practice. A financial institution deployment, support for open credentials or documented controls for delegated authority would make the case much stronger. Until then, the launch is a credible expansion of Fobi's digital identity technology into a financial problem that is becoming harder as software gains more authority.
As AI agents gain access to payments, financial accounts and digital credentials, will proving identity once be enough, or will financial services need to keep verifying who is in control and exactly what they are allowed to do?
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Aug 17, 2026

A mid-size alternative lender in Vilnius pulls company registry filings, marketplace pricing and sanctions lists into its underwriting model every night. None of it is illegal to read. Most of it becomes a liability the moment it is copied, stored and combined with something else. That gap between "publicly visible" and "lawfully processed" is where fintech compliance teams keep losing arguments with their own data science departments.
Public web data – company filings, marketplace listings, court dockets, sanctions databases, social media bios – has become a standard input for credit scoring, fraud detection, KYB and competitive pricing in financial services. In Meta Platforms v. Bright Data, a federal district court held that Bright Data had not breached Meta's terms of service by collecting data from logged-out pages, which was the specific conduct at issue. The ruling turned on Bright Data's particular conduct and its contractual relationship with Meta rather than establishing a general rule for scraping public websites. For a regulated entity, that distinction is not academic. A bank's third-party risk team, an EU DORA auditor or a state attorney general does not care whether the data was "technically public" if the collection method itself created exposure.
hiQ Labs v. LinkedIn is still the reference case for US practitioners, and it is more nuanced than the headlines from 2019 suggest. The Ninth Circuit held twice, first in 2019 and again on remand in 2022, that scraping data from pages open to any visitor does not amount to accessing a computer "without authorization" under the Computer Fraud and Abuse Act. That took the CFAA off the table as a criminal exposure for reading public pages. It did not end the case. hiQ and LinkedIn settled the remaining contract claims in 2022, and hiQ agreed to destroy the data it had already collected and pay damages, because its scraping still violated LinkedIn's user agreement. The lesson for a fintech legal team is specific: CFAA risk and contract risk are two separate questions, and winning on one does not close the other.
On the EU side, the CFAA question barely matters, because GDPR does not distinguish between public and private personal data. Article 4 defines personal data by whether it relates to an identifiable natural person, not by where it was found. A LinkedIn bio, a court filing with a defendant's name, or a marketplace seller profile with a real name attached all fall inside GDPR's scope the moment they are collected, and Article 6 still requires a lawful basis – legitimate interest is workable for adverse-media or fraud screening, but it requires a documented balancing test, not just a note in a Confluence page.
Four use cases account for most of the public-data traffic coming out of fintech data engineering teams. Alternative underwriting pulls e-commerce store metrics, invoice marketplaces and gig-platform ratings to score borrowers who lack conventional credit files – Kabbage and, later, Amex built entire product lines on this. AML and sanctions screening cross-references OFAC, EU and UN lists against onboarding data, refreshed daily because list updates are unscheduled. Competitive pricing intelligence in embedded finance and BNPL tracks merchant-facing rates across marketplaces to benchmark interchange and fee structures. Fraud and adverse-media screening checks court records, press mentions and social profiles as a secondary signal alongside device fingerprinting.
Not all four carry the same regulatory weight. The table below is the one compliance teams actually need before greenlighting a collection project, not a generic "data source" taxonomy.
| Data source | Typical fintech use | Regulatory sensitivity | Main legal basis to check |
| Company registries (Companies House, EDGAR, EU BRIS) | KYB, beneficial ownership checks | Low to medium | Public register rules and applicable data protection law; filings may contain personal data of directors, officers, beneficial owners and other natural persons |
| Sanctions and PEP lists (OFAC, EU, UN) | AML/KYC screening | Low | Government-published, but update frequency and source authenticity matter |
| E-commerce and marketplace pricing | Competitive intelligence, embedded-finance pricing models | Low to medium | Terms of service and contract law; CFAA exposure may be lower for pages accessible without login (per hiQ v. LinkedIn) |
| Public social media profiles | Alternative credit signals, fraud indicators | Medium to high | GDPR/CCPA personal-data rules apply even if the profile is public |
| Court records and litigation databases | Adverse media, fraud investigation | High | Jurisdiction-specific rules on re-use of judicial data (varies widely, e.g. France's Article 33) |
The engineering choices matter as much as the legal analysis, because a regulator or a bank's third-party risk assessor will ask for logs, not intentions. A defensible pipeline has five properties, and they map to concrete infrastructure decisions rather than policy statements.

Figure 1
Figure 1. Each control maps to an artifact a third-party risk assessor can actually inspect. The first four are described below; request logging is the fifth, and the one the practical takeaway returns to.
Reading a site's robots.txt crawl-delay directive and setting concurrency accordingly is a five-minute engineering task that changes the legal character of the whole program. A crawler hitting a company registry at 200 requests per second looks like a denial-of-service test to the target's security team, regardless of what the data is used for afterward. Most production fintech scrapers we've reviewed cap at 1 request per 2-4 seconds per domain, which keeps CPU load on the target negligible and avoids the WAF triggers that generate abuse complaints in the first place.
This is the point where proxy infrastructure choice stops being a procurement decision and starts being a compliance decision. Rotating through residential or datacenter IPs to maintain a stable success rate against rate limits is standard engineering practice. Rotating IPs specifically to re-access a source after being blocked for a terms-of-service violation is the fact pattern that turned hiQ's win on CFAA into a loss on contract claims. The distinction sounds semantic until an opposing counsel reconstructs your request logs during discovery.
Filtering personal identifiers (names, emails, phone numbers, biometric-adjacent fields) before the data lands in a warehouse is materially cheaper than filtering it after ten analysts have already queried the raw table. A regex-and-NER pass at the collection layer, logged with a timestamp and a rule version, is the artifact a DPO can actually show an auditor.
GDPR's storage limitation principle (Article 5(1)(e)) and most US state privacy laws expect a defined retention period. "We keep everything indefinitely for model retraining" is the single most common finding in the DPIAs we've read for alt-data underwriting programs, and it is usually fixable with a 90-180 day rolling window plus a documented exception process for flagged accounts.
Proxy and scraping infrastructure choice affects three things a compliance file will ask about: whether the vendor itself runs KYC on IP sourcing, whether the billing model matches your actual usage pattern (per-IP monthly vs. per-GB bandwidth), and whether the vendor's own terms indicate the network is ethically sourced rather than built from compromised devices.
| Provider | Billing model | Entry price | Where it fits a fintech workload |
| Proxys.io | Per dedicated IP / month | From $1.40/mo (individual IPv4), $0.13/mo (IPv6) | Steady, low-volume monitoring jobs (registry checks, sanctions list refresh) where a fixed, auditable IP per data feed is easier to log than rotating bandwidth pools |
| Decodo (formerly Smartproxy) | Per GB, tiered | $2.00-$3.75/GB depending on volume | Mid-volume scraping across many source domains where bandwidth, not IP count, is the cost driver |
| Oxylabs | Per GB, sales-assisted | Roughly $8/GB at entry tier, KYC required before provisioning | Enterprises that want a vendor-side KYC record as part of their own third-party risk file |
| Bright Data | Per GB (PAYG or committed) | $8.40/GB PAYG residential, down to ~$3/GB committed; datacenter from ~$0.90/GB | Large, multi-region collection programs where volume discounts offset the higher entry rate |
The billing model split matters more than the headline price. A sanctions-list refresh job that hits the same twelve government sources every night at a predictable, low volume is a poor fit for per-GB bandwidth pricing – you're paying for a metric (data transferred) that has almost nothing to do with your actual constraint, which is IP reputation and consistency of access over time. Vendors like Proxys.io bill per dedicated IP per month, which lines up better with that access pattern and makes cost forecasting for a fixed set of monitored sources straightforward. A marketplace-pricing crawl that touches thousands of product pages across dozens of domains is the opposite case: bandwidth is the real cost driver, and a per-GB model from Decodo, Oxylabs or Bright Data scales more predictably with that workload. Enterprises already running Oxylabs' or Bright Data's own KYC process may lean on that as one input to their own vendor risk assessment, though it doesn't substitute for one.
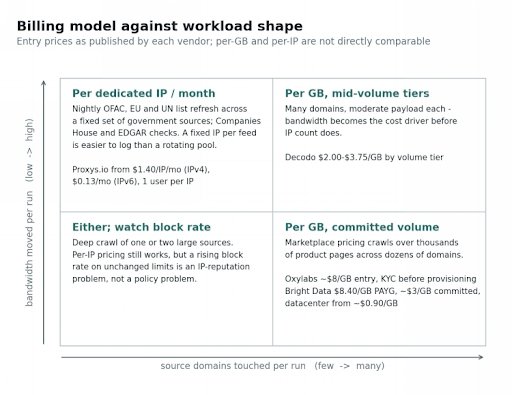
Figure 2
Figure 2. The two variables that move cost are how many domains a run touches and how much data it moves, not the headline price per unit. Per-IP and per-GB rates are quoted in different units and cannot be compared directly.
None of these vendors, including the ones with published ethics or KYC pages, remove the fintech's own obligation to define a lawful basis, log what was collected, and honor retention limits. The proxy layer solves an availability and reliability problem – consistent access to public pages without disproportionate load on the source – not a data protection problem.
Three signals usually mean a proxy or scraping setup needs to change, independent of price. First, a rising block rate on sources with unchanged rate limits – that's an IP-reputation problem the vendor's pool has accumulated, not something a compliance policy fixes. Second, the compliance team asking for source-level access logs the engineering stack can't currently produce – that's a signal the collection layer needs structured logging before it needs a new vendor. Third, a shift in workload shape, for example moving from a handful of steady, low-volume registry checks to broad multi-domain marketplace crawling, which usually means the per-IP pricing that worked for the first case stops making sense for the second.
A fintech data program built on public web sources holds up under regulatory review when three things are documented before the first request is ever sent: the lawful basis for each data category (not a blanket justification), the technical controls that keep collection proportionate to the source (rate limits, minimization, retention), and a request log detailed enough to reconstruct what was collected and why if a regulator or a counterparty's third-party risk team asks. The infrastructure vendor is a smaller decision than most procurement processes treat it as – it changes reliability and cost, not the underlying legal analysis.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |



August 26th, 2025

January 4th, 2024

June 1st, 2021

September 9th, 2020

July 9th, 2018

January 3rd, 2018

September 25th, 2017

June 20th, 2017

May 10th, 2017

December 14th, 2016
