




Karsten Wenzlaff, Advisor
August 26th, 2025
Karsten Wenzlaff is a Crowdfunding and Fintech Expert from Germany. He is Secretary-General of Digit[...]


Apr 29, 2026 | NCFA Resource | Artificial Intelligence And Data, Risk Compliance And Regtech
The MIT AI Risk Repository is an open database created by researchers at MIT to bring structure to AI risk. It compiles more than 1,700 documented risks from 74 existing frameworks and studies into a single system. The aim is practical. AI risk guidance exists, but it is scattered and inconsistent across sources. This repository organizes it into a shared taxonomy, with links that show how risks connect and compound across systems.
In practice, this gives teams a consistent way to map risk across AI systems.
Teams already running AI in production will get the most from this. If you’re operating models in lending, fraud, onboarding, or customer support, it gives you a structured way to think about risk across systems. Larger fintechs and financial institutions dealing with audit and regulatory pressure will find it useful quickly. Early stage teams without deployed models will likely find it heavy and not immediately relevant.
The strength here is structure. It turns fragmented AI risk concepts into something teams can actually use, and the causal links add depth that most frameworks miss. At the same time, it does not rank risks by likelihood or impact, and it does not translate directly into controls or regulatory compliance. Some classifications reflect interpretation across sources, and emerging risks may not be fully captured. Teams still need to apply judgment and build their own control layer on top.
Repository Homepage (AI risk overview and navigation)
Full Risk Database (AI risk dataset for audits)
Causal Taxonomy (AI risk relationships mapping)
Domain Taxonomy (AI risk classification framework)
Research Paper (AI risk methodology and design)
 The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
 |  |  |
|---|---|---|
 |  |  |
Apr 28, 2026 | NCFA Insight | Risk Compliance And Regtech, Digital Assets Blockchain And Tokenization, Open Banking Open Finance And Data Sharing, Payments And Market Infrastructure, Capital Markets And Funding

On Apr 28, 2026, the Government of Canada released its Spring Economic Update key measures. For fintech and financial institutions, a deeper and more integrated operating model is now taking form across fraud, payments, digital assets, banking fees, data access, and capital formation. Canada wants more competition in financial services, but not at the cost of weak controls. The update points to a more disciplined market where firms can win through lower costs, faster rails, better data access, and stronger fraud prevention (at least that's the strategic read).
François Philippe Champagne, Minister of Finance and National Revenue, Government of Canada:
“From geopolitical shifts to supply chain disruptions to rapid technological breakthroughs, including in artificial intelligence, the world is changing quickly and Canada must adapt to thrive.”
The update treats fraud as a structural weakness in the financial system, not just a policing problem. Canada will establish the Financial Crimes Agency as a dedicated federal body for serious and complex financial crime, with police powers, civilian leadership, specialized personnel, and an asset recovery mandate.
The funding is material. Ottawa proposes $352.7 million over five years and $82.1 million ongoing for the agency, plus $46.2 million over five years for the Public Prosecution Service of Canada and $19.6 million over five years for the Department of Finance Canada.
For fintechs, banks, platforms, and payment firms, this raises the bar. Fraud controls now need to work across onboarding, funding, transactions, identity, communications, reporting, and recovery. A good product experience will not carry a weak risk model.
The clearest digital asset measure is the proposed crypto ATM ban. Annex 2 goes further than a policy signal. It proposes amendments to the Proceeds of Crime Money Laundering and Terrorist Financing Act and regulations to make it a criminal offence to operate a cryptocurrency automated teller machine.
Crypto ATMs connect cash to crypto quickly with limited friction, and can move scam proceeds outside the banking system before recovery becomes realistic. CBC reported that Canada has nearly 4,000 crypto ATMs, the most per capita in the world, and that some smaller deposits require only a phone number when under $1,000.
It's a targeted intervention of digital assets at what the government feels is the weakest access point. Serious crypto firms, custodians, exchanges, and tokenized finance builders should take note. Regulatory pressure will always look to where where money enters, exits, and escapes oversight.
The update recognizes that money services businesses support remittances, currency exchange, digital payments, competition, and inclusion. It also says criminals increasingly abuse MSBs for money laundering, terrorist financing, sanctions evasion, and fraud.
FINTRAC revoked the registration of 84 MSBs in March 2026 alone. Ottawa now proposes new Ministerial Directive powers, expanded authority for FINTRAC to refuse or revoke MSB registration, measures to prevent non compliant MSBs from re registering, more criminal record checks, action on shelf MSBs, and better visibility into what services each MSB actually provides.
This resets the perimeter. MSBs are now seen as critical risk gateways that can no longer just sit at the edge of the system as light infrastructure. This will help strong operators over time because weak competitors will find it harder to hide behind registration status alone.
The update links competition policy directly to household financial costs. New NSF fee rules cap charges at $10, down from $45 to $50, with expected consumer savings of more than $600 million annually. Ottawa also intends to consult on prohibiting investment account transfer fees at federally regulated financial institutions. Those fees currently cost Canadians an average of $150 per transfer.
Fee friction has long protected incumbent economics. Lower caps and easier switching reward firms that use better data, real time balance checks, clearer pricing, and lower operating costs. Fintechs should treat this as a product opening opportunity.
The update keeps consumer driven banking as part of Canada's competition agenda. It says amendments to complete the Consumer Driven Banking Act have passed, giving consumers greater control over their finances.
Annex 2 also points to related amendments involving the Retail Payment Activities Act, the Payment Clearing and Settlement Act, the Consumer Driven Banking Act, and the Stablecoin Act as part of Bank of Canada cost recovery consolidation.
Read this as infrastructure alignment. Canada is preparing the back office of regulation for a more digital financial system.
The Canada Strong Fund creates another fintech touchpoint. Ottawa describes it as a national investment initiative focused mainly on equity investments in strategic Canadian projects and companies. The government also intends to offer Canadians a widely accessible retail investment product tied to the fund.
Canada wants citizens to participate directly in national growth assets while protecting initial invested capital. If Canadians can invest in strategic projects through a national vehicle, how directly competitive will it be and what role will regulated online investment platforms, exempt market dealers, wealthtech firms, and investor education tools play?
Canada is finally becoming more competitive, albeit with a much tighter control layer. Fraud enforcement gets funding and focus. Crypto ATMs face prohibition. MSBs face deeper scrutiny. Banking fees face compression. Open banking remains active. Payments, stablecoins, and data access move into more coordinated oversight. Retail capital access gets a new public investment model.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Apr 28, 2026 | NCFA Insight | Risk Compliance And Regtech
Image: Freepik
On Apr 26, 2026, the CBC reported that Premier Wab Kinew announced at a weekend fundraiser that Manitoba plans to restrict youth access to social media and AI chatbots.
At the time of publishing, an official government release, bill or consultation paper wasn't available so treat this as early insight rather than a confirmed regulatory event (just yet). The stronger proof is already visible in global policy patterns, so it's only a matter of time.
Australia’s social media minimum age rules took effect on Dec 10, 2025, and eSafety reported that platforms had removed access to 4.7 million under 16 accounts across Australia by mid December 2025.
In Europe, the European Commission has published minor protection guidelines under the Digital Services Act, and the European Parliament has backed a minimum age of 16 for access to social media, video sharing platforms, and AI companions.
Given the trajectory and potential risks of AI, the debate isn't just about doom scrolling any more. It's fuelling a compliance market for age assurance, safer design, and AI access controls.
Australian government's rules put responsibility on age restricted platforms to take reasonable steps, not on parents to police every account. So age restrictions and assurance are now an infrastructure issue. A checkbox, self declared birth date, or parental reminder won't satisfy regulators when millions of accounts need to be assessed, restricted, or removed.
Children can get pulled into endless feeds, autoplay videos, harmful recommendations, bullying, sexual exploitation, self harm content, eating disorder content, and late night scrolling that cuts into sleep. That's why social media is getting the attention from lawmakers first. The bigger question for fintech and digital identity comes next. Once governments make platforms check age, the same requirement can spread to other digital services used by minors.
The EU hasn't implemented a social media ban on age just yet, but it's building the infrastructure that could support stricter controls. On July 14, 2025, the European Commission released an age verification app prototype under the Digital Services Act. The Commission says the app would let users prove they are over 18 when accessing restricted adult content while keeping control of other personal information, including their exact age and identity.
The Commission’s age verification page says the solution was technically ready for implementation as of Apr 15, 2026. The blueprint also gives platforms a practical build plan. It covers the technical specs, system design, data connections, and open source code needed to support age checks. Age assurance now has to protect children without creating a new privacy problem. Platforms need a trusted age signal. Users should not have to share a full identity file just to prove they meet an age limit.
The clearest policy clue comes from Europe’s treatment of AI companions. On Nov 26, 2025, the European Parliament voted 483 in favour, 92 against, and 86 abstentions on a non legislative report calling for a minimum age of 16 for social media, video sharing platforms, and AI companions, unless parents authorize access for users aged 13 to 16.
The same Parliament release cites research that 97% of young people go online every day, 78% of 13 to 17 year olds check their devices at least hourly, and one in four minors show problematic or dysfunctional smartphone use. It also cites 2025 Eurobarometer impact of digitalisation findings that more than 90% of Europeans see online child protection as urgent, including 93% for social media’s negative impact on mental health, 92% for cyberbullying, and 92% for restricting access to age inappropriate content.
Those numbers explain why AI gets pulled into the same debate. Doom scrolling rules target addictive design and harmful content discovery. AI companion rules target interaction, dependency, personalized responses, manipulation, and adult like conversations with minors. NCFA has already examined youth AI protection risks, including lawsuits involving generative AI and vulnerable users. Regulators are starting to connect age, vulnerability, consent, product design, and AI behaviour into one compliance problem.
The public debate may start with under 16 social media bans. The business reality runs deeper. Governments want digital services to know when a user is a child, adjust the experience, and prove that controls work. Age assurance is becoming part of digital trust infrastructure. AI makes the stakes higher because the product doesn't just offer access to content anymore. It talks back, adapts, remembers, and can build dependence. That's why kid risk now part of the compliance stack. Once age becomes a regulated access condition, the same logic can reach payments, gaming, lending, investing, AI assistants, marketplaces, app stores, and identity wallets.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Apr 27, 2026 | NCFA Fintech Insight | Cybersecurity And AI Risk
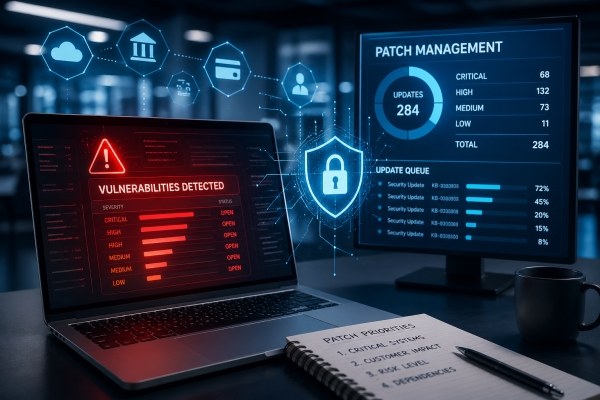
On April 21, 2026, Mozilla's Firefox team said early access to Anthropic’s Claude Mythos Preview helped identify 271 vulnerabilities in Firefox 150, after an earlier Anthropic collaboration with Opus 4.6 helped fix 22 security sensitive bugs in Firefox 148. It's a real world test Warning that AI has started to compress months of expert vulnerability research into a much shorter discovery cycle.
The deeper issue for financial services isn’t whether AI can find bugs. Mozilla’s post makes that answer fairly clear. The harder question is whether banks, fintechs, payment providers, cloud vendors, and critical infrastructure operators can test, rank, schedule, and deploy fixes fast enough once the bug volume rises?
Security teams have always fought an unfair game. That is attackers only need one weakness while defenders have to protect the full surface. Mozilla’s Bobby Holley wrote that elite security researchers find bugs that fuzzers miss by reasoning through source code, and that computers “were completely incapable of doing this a few months ago, and now they excel at it.” He also wrote that Mythos Preview was “every bit as capable” as the best security researchers Mozilla has studied.
Limited human cyber security expertise no longer limits discovery in the same way. Once AI can reason through large codebases, the volume of known vulnerabilities rises quickly. Mozilla for example jumped from 22 bugs in Firefox 148 to 271 vulnerabilities in Firefox 150. Detection capacity jumps faster than operational capacity.
For fintechs, that means security teams may see more vendor alerts, more emergency updates, more dependency risk, and more pressure to patch without breaking customer facing systems. More discovery helps defenders, but only when organizations can practically execute on the risk.
The Financial Times reported that companies with Mythos access want stronger joint defense across government and business, especially for hospitals, banks, utilities, and other critical infrastructure. It also reported that Microsoft, Fifth Third’s technology provider, has rolled out almost 150 software updates since Mythos’s release. Patching can affect numerous areas, such as customer access, payments, fraud controls, and vendor dependencies.
Financial infrastructure like core banking systems, payment gateways, and fraud engines operate on tight turnaround schedules and a bad patch or gap can interrupt service, leaving a known weakness open. And the tradeoff becomes harder when AI expands the queue of fixes beyond human capacity.
A 2026 analysis summarized on the Harvard Law School Forum on Corporate Governance found that Russell 3000 companies hit by significant cyber incidents underperformed the broader market by about 5% on average over three years. The study reviewed 176 unique cyber events from 2022 through 2024, and found that finance, banking, and health care accounted for more than half of reported incidents. That means board failures, patch delays, poor vendor oversight can damage shareholder value for years.
The old comfort of quarterly patch cycles won’t hold up well in a world where AI can surface hundreds of issues at once.
Reuters reported on April 21 that unauthorized users accessed Mythos through what Anthropic described as a third party vendor environment. Anthropic said it was investigating the report and had no evidence that the access affected Anthropic systems.
If a tool can find bugs as well as top security experts, then that tool becomes a prime target. Anyone who gets access to it could shortcut months of work and go straight to weak points. That means security is no longer just about protecting your systems. It also includes controlling who can use these AI security tools, how they’re accessed, and what they can see across your vendors and environments.
Warnings from Palo Alto Networks point to where this could go. These tools may allow attackers to link multiple weaknesses together and automate attacks. That’s why the unauthorized access issue matters even without confirmed misuse. The real risk is that the capability itself could leak.
Canadian fintechs don’t run everything themselves. They depend on cloud providers, banks, payment networks, identity services, and other vendors. That means they don’t control when fixes happen, but they still carry the risk if something goes wrong.
That puts pressure on knowing how vendors handle security. Fintech teams need to understand how quickly partners fix serious issues, how they report problems, and whether important updates get priority. Even smaller firms can push for clearer answers before relying on a vendor for critical services.
Regulators should pay attention too. AI can help find problems faster, but only if companies can act on that information in a coordinated way. If not, bigger firms with early access move ahead, while smaller ones fall behind. In Canada, where many fintechs depend on a few key providers, that gap could widen quickly.
Mozilla believes there’s a limit to how many bugs exist, and that defenders may finally be able to find them all. That could happen over time. Right now, though, things will feel messy. More bugs will show up. Fix lists will get longer. Vendors will have to decide what to fix first. Leaders will have to choose between keeping systems running and fixing issues right away. For banks and fintechs, the edge will go to those who can move faster, work closely with partners, and handle frequent updates without disrupting customers, payments, or data.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
April 24, 2026 | NCFA Fintech Whisperer Weekly Intelligence | Payments And Market Infrastructure, Digital Assets Blockchain And Tokenization, Regulation And Policy, Artificial Intelligence And Data

Image: Freepik
This live weekly NCFA intelligence page tracks financial technology developments that significantly affect how fintechs build, sell, raise capital, and operate under scrutiny. Coverage prioritizes Canada and includes global events that directly influence competitive conditions, market access, and execution realities across fintech sectors. This page will be updated throughout the week with market movers in a live format and then each week we'll close the prior week's contents in prep for the upcoming week, and continue on a rolling basis. (Missed prior week's Fintech Whisperer? (December 6-12, 2025, December 13-19, 2025, January 1-9, 2026, January 10-16, 2026, January 17-23, 2026, January 24-30, 2026, January 31-February 6, 2026, February 7-13, 2026, February 14-20, 2026, February 21-27, 2026, February 28-March 6, 2026, March 7-13, 2026, March 14-20, 2026, March 21-27, 2026, March 28-April 3, 2026, April 4-10, 2026, April 11-17, 2026).
RBI has moved from restriction to licence cancellation. Payments banks, wallets, sponsor banks, and fintech platforms should treat this as a hard reminder that governance, compliance controls, depositor protection, and supervisory responsiveness decide whether a regulated licence survives under stress.
Instant payments are starting to add shared, rail-level risk intelligence. Banks and vendors that can plug network signals into fraud controls and payment decisioning will gain speed without giving up control.
The UK is pulling payments reform, stablecoins, open banking, and AI-agent payments into one policy agenda. That gives banks, fintechs, and infrastructure firms a clearer build direction for the next phase of digital money and payment rails.
The PACE Act would move direct rail access from a bank only model toward a supervised nonbank pathway. Payment firms, wallets, remittance providers, and crypto platforms should watch whether Congress turns scale, reserves, and OCC oversight into the price of direct Fed access.
The fee cap changes the economics of Canadian order flow in securities traded on both sides of the border. Marketplaces, brokers, and trading firms need to revisit rebate models, routing logic, and best execution analytics before Nov 2026.
The SEC and CFTC are reducing reporting load while keeping coverage of the largest funds. That lowers compliance cost for smaller firms and shifts the reporting system toward large, systemically relevant managers.
Treasury clearing is now forcing decisions on affiliate repo, cross border booking, liquidity management, and contingency planning. That puts market structure, funding, and clearing operations under live pressure ahead of the compliance dates.
Finfluencer enforcement is now coordinated across jurisdictions and aimed at the platforms as well as the promoters. That raises the compliance and monitoring burden for firms using social channels for distribution and puts more pressure on platforms to block illegal promotions at source.
Client money control failures are still drawing fast and expensive action. Firms handling safeguarded funds need clean role separation, approval controls, reconciliations, and evidence trails that hold up under review.
SMCR reform is now moving from policy into implementation. Banks, fintechs, and regulated firms need to update role mapping, certification processes, accountability records, and reporting workflows without leaving control gaps during the transition.
The rule change is now live. Fund managers, administrators, auditors, and reporting vendors need to update related party reporting workflows and disclosure logic from this reporting cycle forward.
This gives firms a live FCA pathway for AI in production. Providers building AI for payments, risk, compliance, and customer decisioning now have a clearer read on how regulators expect live testing, monitoring, and evidence to be handled.
The UK is refining its crypto framework before implementation to ensure stablecoin payments work within regulated financial systems. For fintechs, this points to a clear direction: stablecoins are moving into formal payment rules, not operating outside them.
OSFI is aligning regulatory reporting with IFRS 18. Insurers, auditors, and regtech providers will need to update reporting systems, data classification, and validation processes ahead of the 2027 transition.
Australia is moving digital asset platforms from patchwork treatment into a licensing regime with custody, settlement, market conduct, and financial resource expectations. For exchanges, brokers, custodians, and tokenised custody platforms, this raises the operating floor before the regime starts in 2027.
N3XT puts tokenized bank money directly onto blockchain rails while retaining the deposit relationship with the issuing institution. That operating model now sits beside tokenized deposits for corporate treasury being developed by much larger banks, but N3XT entered the market with a live product built around continuous settlement from the outset. The difference between bank issued deposit tokens and reserve backed stablecoins is becoming commercially relevant as both compete for institutional payments, liquidity and onchain settlement.
This puts focus on how firms log interactions, flag risk, assign review, and retain records. See related coverage on AI escalation controls and AI chat exposure in court.
Fintech execution is getting more technical and less forgiving. Payments now need network-level risk data. Markets need tighter routing, clearing, and reporting controls. AI and social distribution need evidence, safeguards, and audit trails. The advantage belongs to firms that can turn regulatory change into product, compliance, and infrastructure readiness faster than competitors. NCFA offers various curated resources to help founders and investors stay current on developments that impact fintech markets, subscribe to NCFA weekly newsletter updates, view a rundown of current fintech news and insights, or dive into the latest fintech industry research.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
Apr 21, 2026 | NCFA Feature | Artificial Intelligence And Data
Apr 21, 2026, Florida Attorney General James Uthmeier announced a criminal investigation into OpenAI and ChatGPT following a Florida State University shooting on Apr 17, bringing AI safeguards, records, and escalation controls into a far more serious legal setting. Prosecutors issued subpoenas for materials tied to safeguards, training, and crime reporting, while AP News reports that investigators reviewing AI chat logs linked to the accused shooter. OpenAI says ChatGPT didn't promote harm and that it's cooperating with law enforcement.
For AI operators, it's no longer a question whether or not AI system can generate harmful responses. Numerous use cases and verified facts are escalating the need for strong governance and requirement to show what AI systems produced, what controls were in place, what records were kept, and what happened when risk appeared.
The Florida case stands on its own, but it also fits into a repeatable pattern that keeps building. When AI interacts with vulnerable users, influences behaviour, or operates in sensitive contexts, accountability expands beyond model output.
That includes minors and mental health. NCFA has already outlined AI protection gaps for youth and trust risks tied to AI psychosis claims. Legal claims tied to chatbot interactions and teen harm are now testing whether platforms owe a duty of care. That question isn't yet settled, but it's now active in courts and regulatory discussions.
Exposure doesn't stop with responses alone. Agentic AI systems that can act on their own are being scrutinized because they are starting to trigger workflows, retrieve data, connect tools, and influence real decisions. That expands the scope beyond what the model says. It now includes what the system does, what it initiates, what it fails to flag, and who owns the outcome.
It also raises a second layer of risk. These systems aren't only acting, but are making judgment calls inside those workflows. NCFA has explored this trend in how AI systems are moving from guardrails to judgment, where deciding outcomes is now part of system behaviour, not just model output.
As these systems connect to money, identity, and operational processes, weak controls become visible fast. Risk exposure moves beyond the prompt interface and into the infrastructure where decisions are made and executed.
The legal system doesn't yet have a stable way to classify AI. Different cases treat it as a tool, a product, or an automated process. That uncertainty affects liability, discoverability, and the standard of care expected from firms.
What investigators ask for is starting to line up across cases. Logs. Escalation triggers. Review steps. Retention policies. Safeguards. These are the records that show how a system behaved and how a firm responded. Recent NCFA coverage on AI chat exposure in court and AI escalation controls under test points to the same pressure area. The Florida probe adds another example. When outcomes are challenged, this is where scrutiny begins.
For founders, executives, and boards, responsibility doesn't stop at model performance. It extends to system design, deployment context, monitoring, and response when risk appears. That includes safeguards, escalation thresholds, human review, and whether systems should act in high risk scenarios at all.
When AI becomes central to operations, governance, oversight, and risk controls that affects diligence and board discussions. Investors with board roles or influence over strategy may face questions about what risks were understood, what controls were expected, and how oversight was exercised.
Investors are not insulated. As AI becomes embedded in core operations, governance and risk controls affect diligence and board oversight. When outcomes are challenged, companies will need to show they anticipated risk, implemented controls, and acted on signals.
Thoughts on mitigation? Systems need clear boundaries. Escalation triggers need to be defined before deployment. Logs need to capture full interaction context. Human review needs clear ownership. Agentic systems need limits on when they can act without intervention.
There are also clear red flags. The situations that will attract scrutiny first.
In the near term, markets should expect more subpoenas, more edge case litigation, and more focus on how AI interactions are recorded and reviewed. Over time, governance will tighten around system level accountability. That includes how decisions are chained, how risk is surfaced, and how AI companies demonstrate that they acted when it mattered.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |
April 21, 2026

Image: Pexels
W-2 and 1099 forms filing is one of the least understood areas of running a business.
Get it wrong and the IRS will come after you. Get it right and taxes will be a breeze.
The good news? Once the differences click, it's pretty straightforward.
Both forms report income received during the year. However they are used for very different circumstances.
A W-2 form gets sent to employees. It shows wages earned and all taxes withheld (federal income tax, Social Security, Medicare). The employer automatically withheld those amounts during the year.
A 1099 form is sent to contractors and freelancers. The most familiar one is called a 1099-NEC, which stands for nonemployee compensation. With a 1099 they don't withhold taxes at all. The contractor is responsible for paying it all themselves.
Here's why getting this right matters from day one...
Accuracy is not negotiable when it comes to W-2 and 1099 forms filing. Whether processing just a few contractors or hundreds of employees, this software solution handles the guesswork of generating, filing, and distributing both W-2s and 1099s correctly — freeing up time and eliminating expensive mistakes.
This is where most businesses get tripped up.
The IRS Worker Classification Test evaluates three distinct factors. They are as follows:
If everyone says yes... then that worker is most likely an employee that requires a W-2.
If the worker gets to set their own schedule, uses their own tools and equipment, and gets paid per project... chances are they are an independent contractor that requires a 1099-NEC.
Pretty straightforward, right?
Here are a few quick examples to make it clear:
W-2 employees typically include:
1099 contractors typically include:
With over 36% of the US workforce now freelancing — that's over 70 million Americans — understanding the 1099 side of things has never been more important.
This is the part that catches a lot of people off guard.
When it comes to W-2 employees, the employer handles payroll taxes. This includes withholding federal income tax, state income tax, and paying half of the FICA tax (Social Security and Medicare taxes) while the employee pays the other half.
For 1099 contractors, it is a completely different story.
Taxes aren't automatically withheld from their paycheck. Instead, they pay estimated quarterly taxes directly to the IRS.
What's more, the self-employment tax sits at 15.3% — twice as much as what a W-2 employee pays. Why? Because 1099 workers pay both the employer and employee portion of Social Security and Medicare taxes.
Granted, 1099 workers have one benefit. Many of their work-related expenses are deductible on Schedule C. This includes home office expenses, equipment, software, mileage, etc. These write-offs lower taxable income, partially negating that higher rate.
It balances out for many contractors — but only if they track everything properly.
Missing these deadlines comes with real penalties. So mark the calendar.
January 31 is the IRS deadline for W-2 and 1099-NEC forms.
Here is what needs to happen by that date:
One final 1099-NEC tidbit... File a form for any contractor paid $600 or more. In 2026, the minimum increases to $2,000 per new law. Regardless, keep records of contractor payments all year long — not just January.
Misclassifying workers is not just a paperwork problem. It is a financial one.
Misclassification is taken very seriously by the IRS. When a company willfully misclassifies employees as contractors to evade paying payroll taxes, the penalties stack up fast:
And the IRS typically goes back three years when auditing unpaid employment taxes.
The silver lining? If there is genuine uncertainty about whether a worker is a W-2 employee or a 1099 contractor, businesses can file Form SS-8 and let the IRS make the call.
Staying compliant with W-2 and 1099 forms filing does not have to be stressful.
Here is a simple process to follow:
The biggest mistake businesses make is waiting until January. By January it is a frenzy. Start with a clean system and tax season is a non-event.
When it comes to W-2 and 1099 forms filing, there's really only one question. How is the worker classified?
W-2 employees receive W-2 forms. 1099 contractors receive 1099-NEC forms. The taxes, deadlines, and penalties are entirely different.
To quickly recap what matters most:
Classify properly, stay ahead of deadlines, and implement with the correct toolset. Those are the only things needed to stay clean and compliant year after year.
The National Crowdfunding & Fintech Association (NCFA Canada) is a financial innovation ecosystem that provides education, market intelligence, industry stewardship, networking and funding opportunities and services to thousands of community members and works closely with industry, government, partners and affiliates to create a vibrant and innovative fintech and funding industry in Canada. Decentralized and distributed, NCFA is engaged with global stakeholders and helps incubate projects and investment in fintech, alternative finance, crowdfunding, peer-to-peer finance, payments, digital assets and tokens, artificial intelligence, blockchain, cryptocurrency, regtech, and insurtech sectors. Join Canada's Fintech & Funding Community today FREE! Or become a contributing member and get perks. For more information, please visit: www.ncfacanada.org
| | |
|---|---|---|
| | |


August 26th, 2025

January 4th, 2024

June 1st, 2021

September 9th, 2020

July 9th, 2018

January 3rd, 2018

September 25th, 2017

June 20th, 2017

May 10th, 2017

December 14th, 2016